Explore GyaanGrid Vault
Masterclasses
Comics Library
Issue #1
Kafka Explained: The Million Request Problem
Issue #2
Retrieval-Augmented Generation (RAG) Explained: A Simple Comic Book Guide to RAG, LLMs, Vector Databases, Semantic Search, and Modern AI for Beginners.
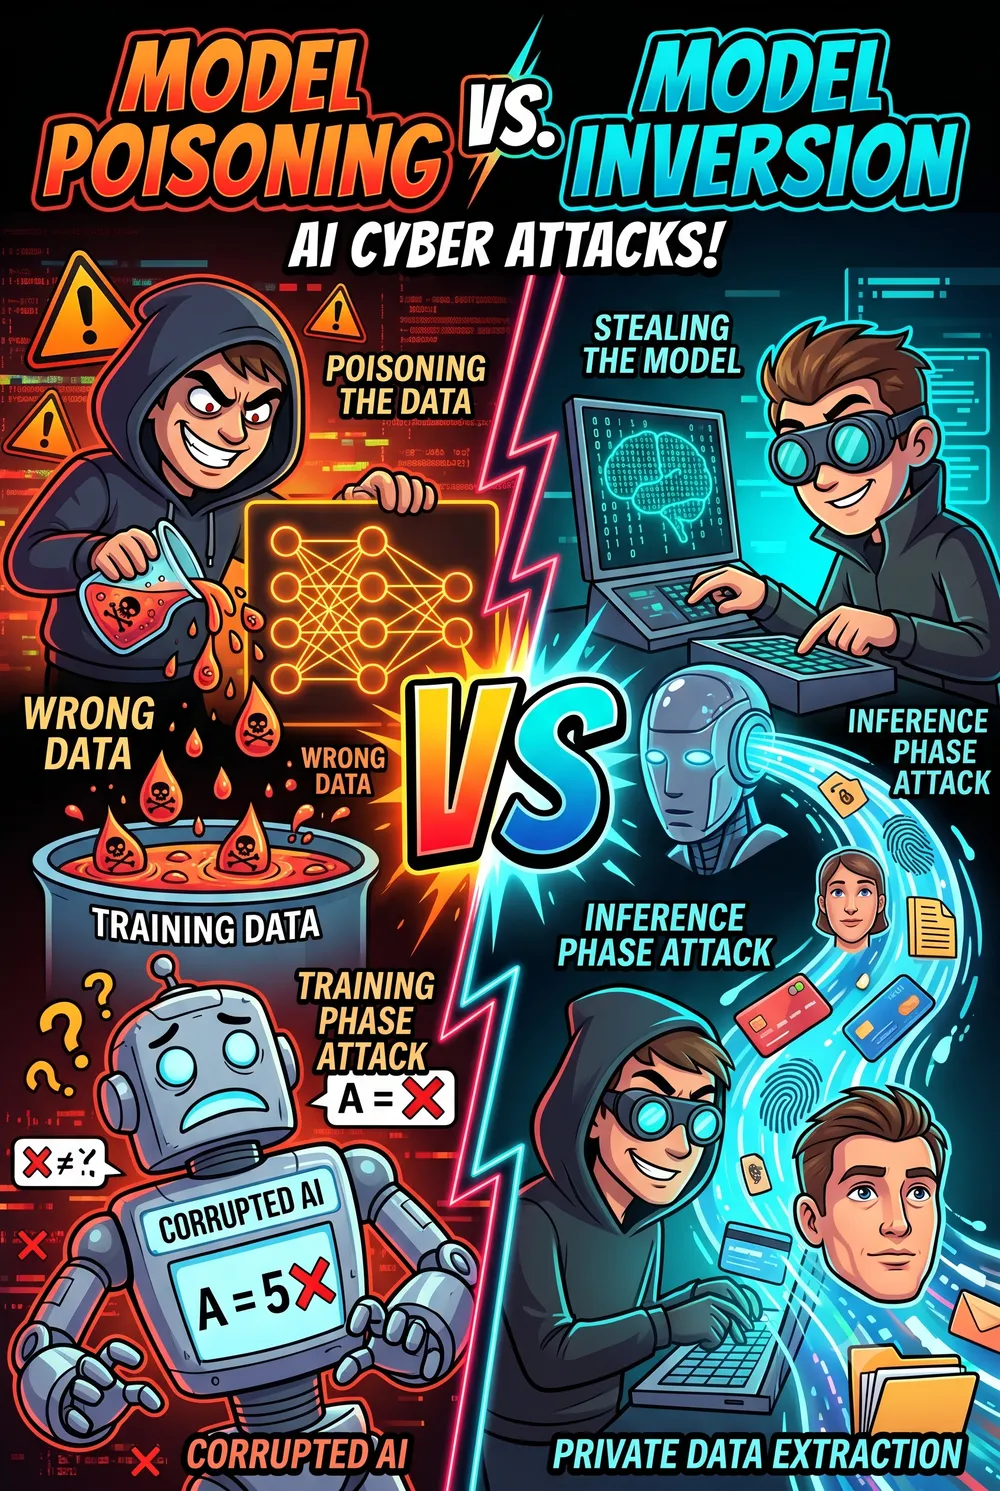
Issue #3
Understanding Model Poisoning vs. Model Inversion Attacks in AI Security
Issue #4
Canary Token
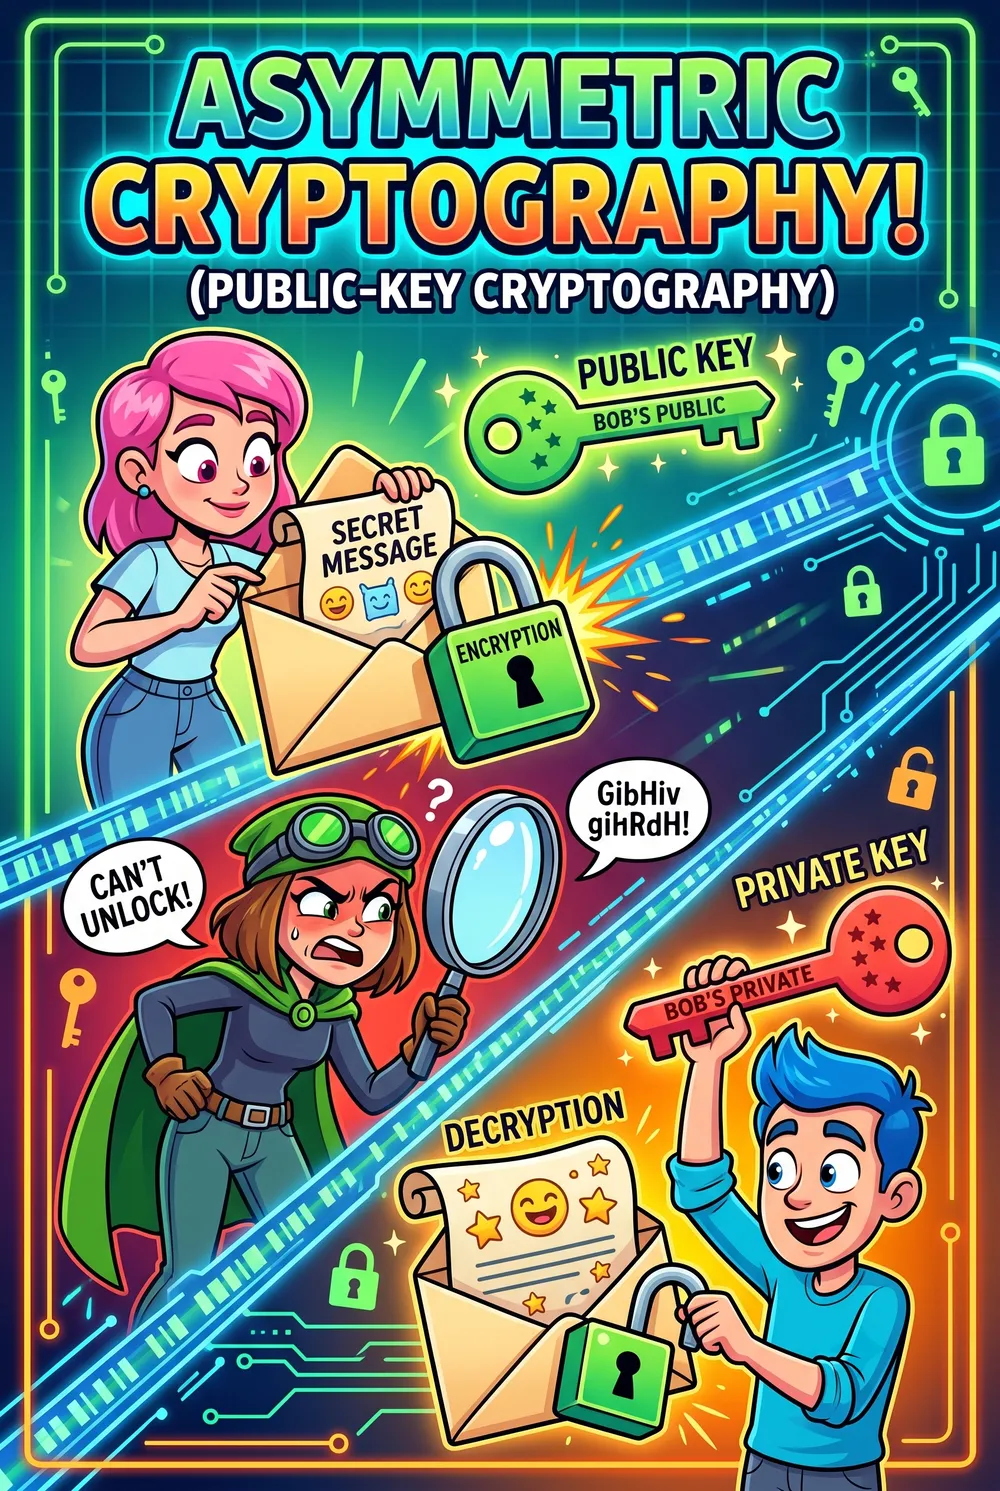
Issue #5
Asymmetic Cryptography
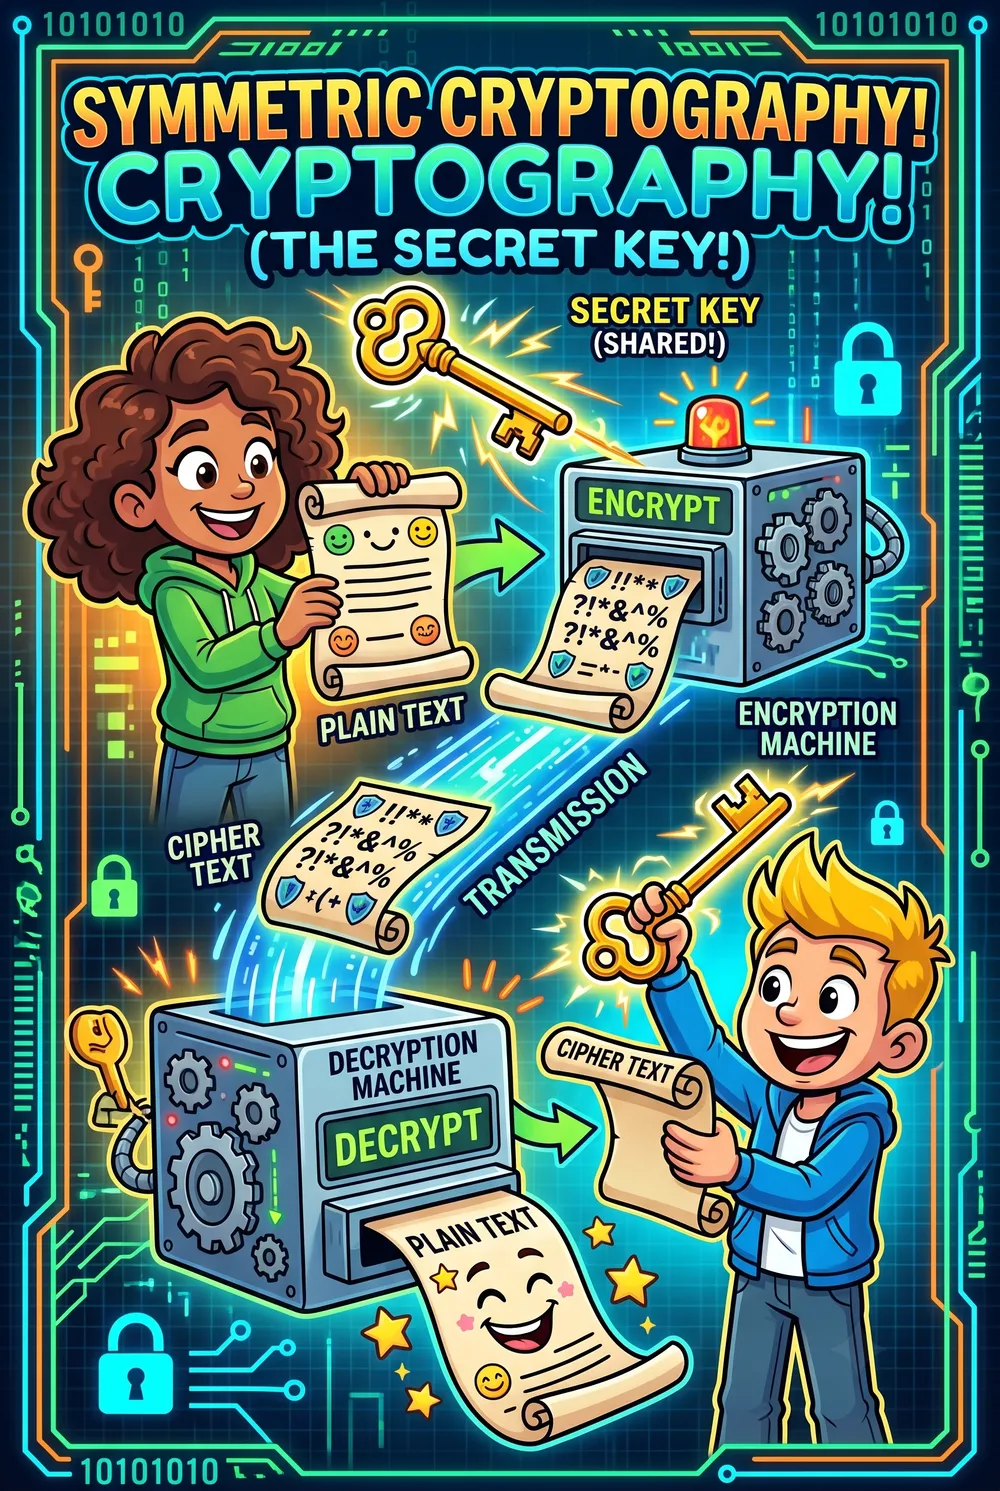
Issue #6
Symmetric Cryptography
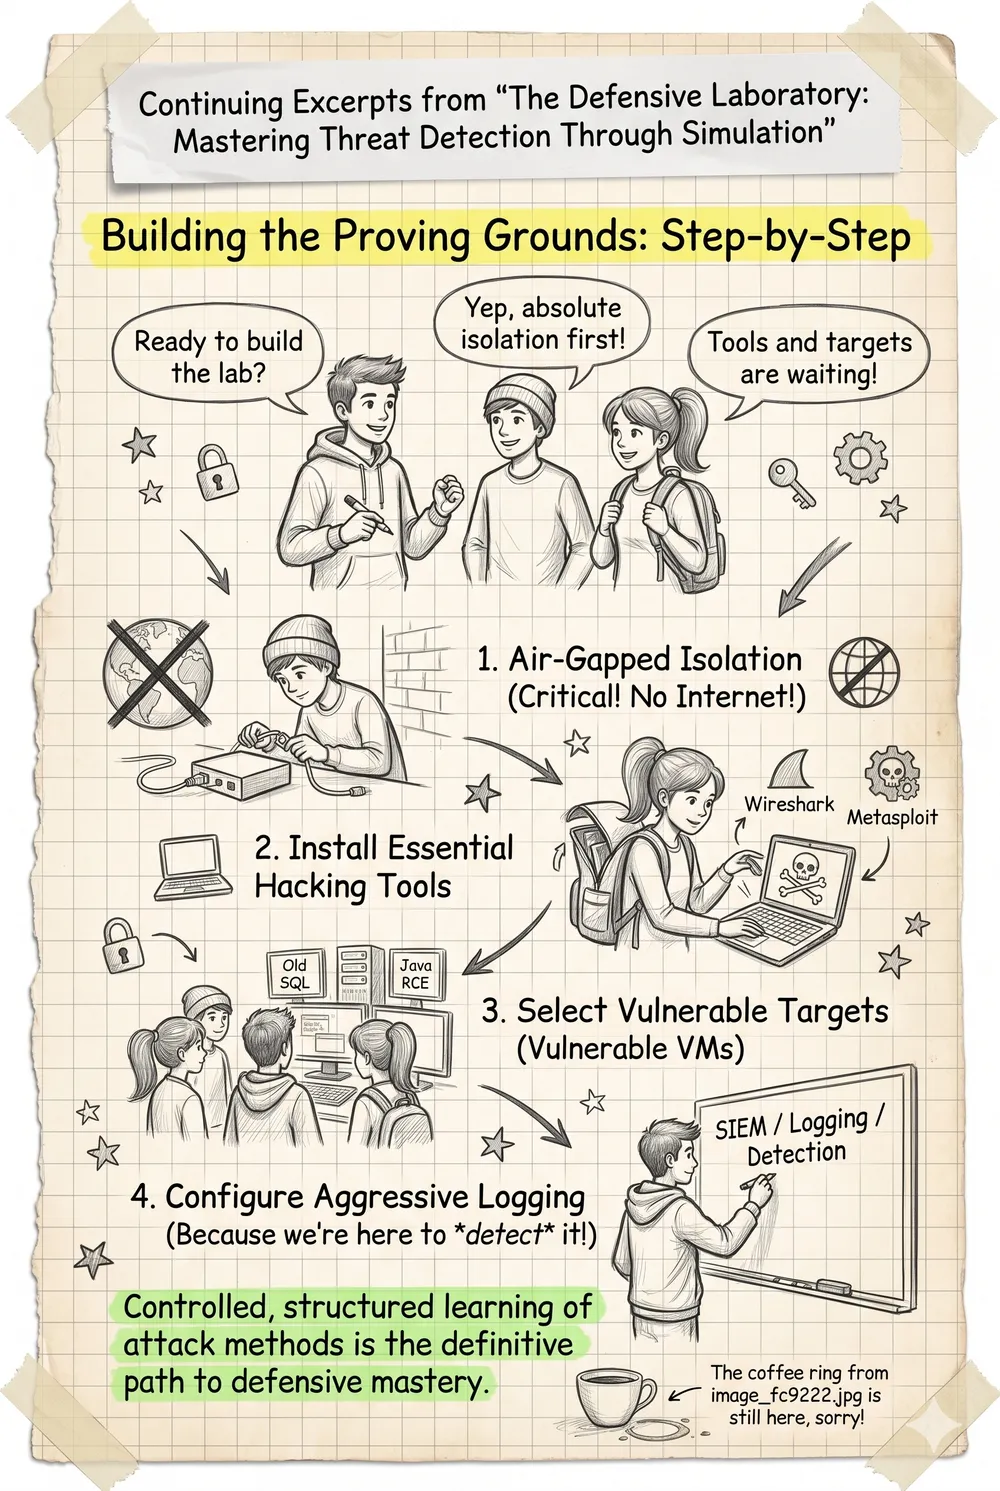
Issue #7
Practical_Threat_Detection
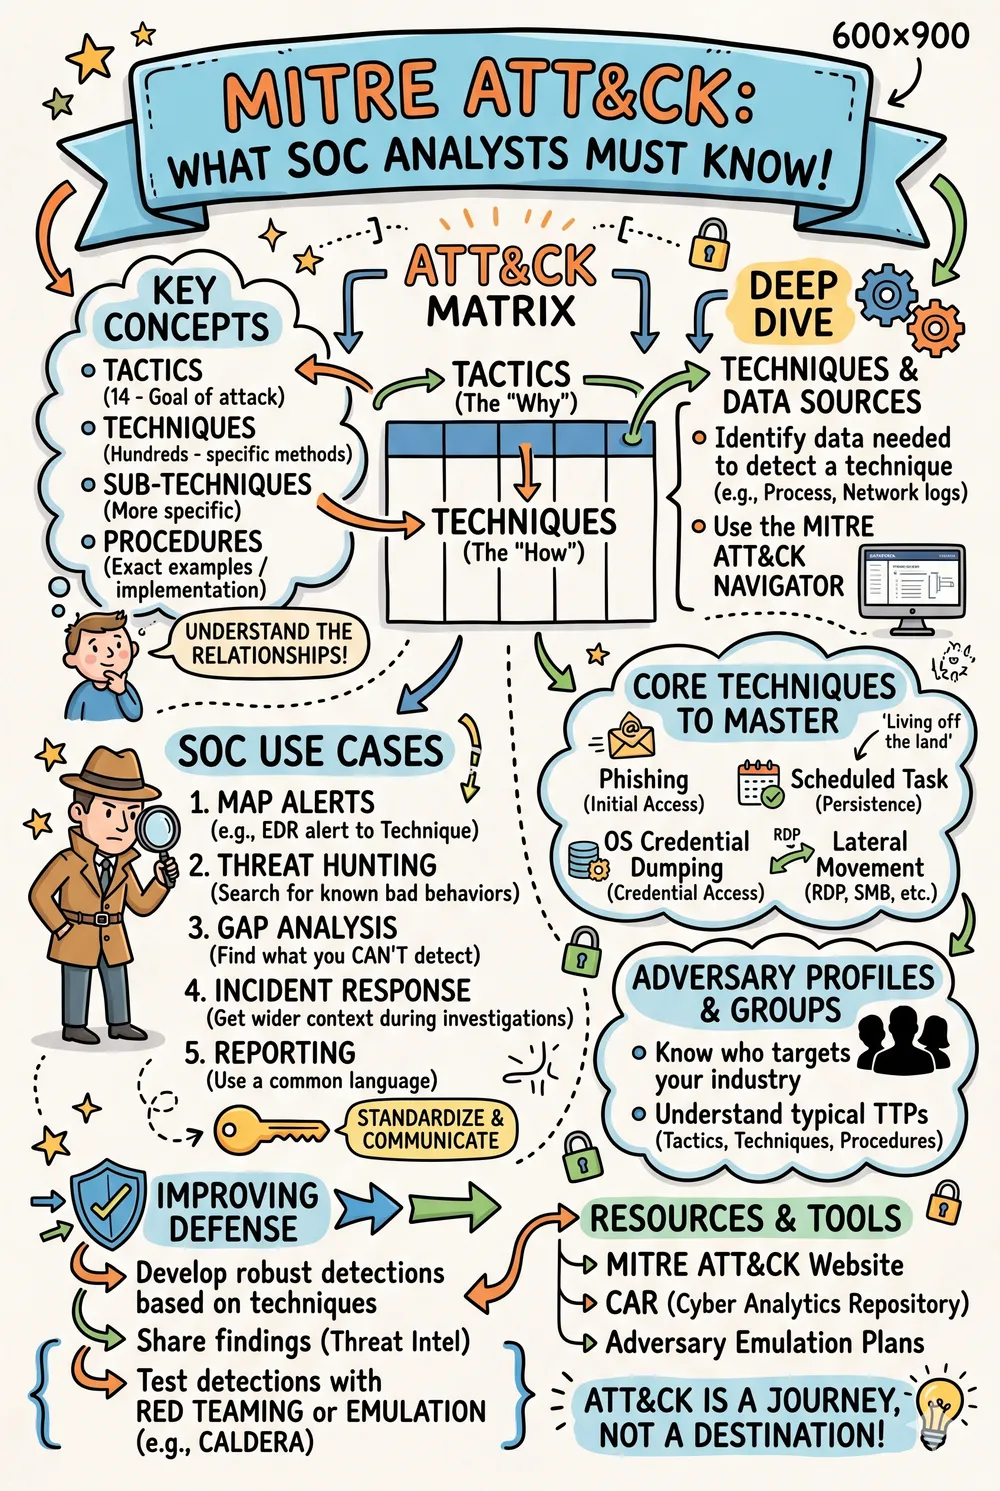
Issue #8
The_MITRE_ATT_CK_Map
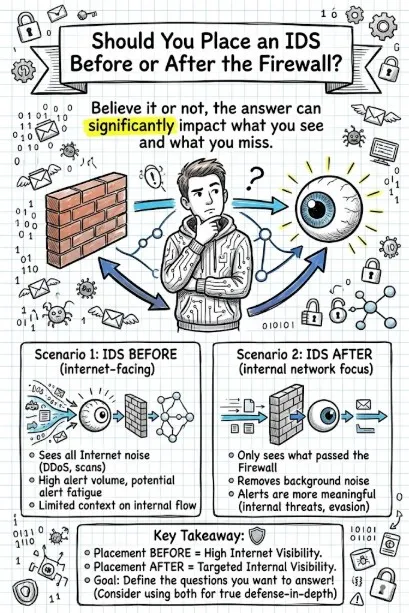
Issue #9
IDS Placement Strategies
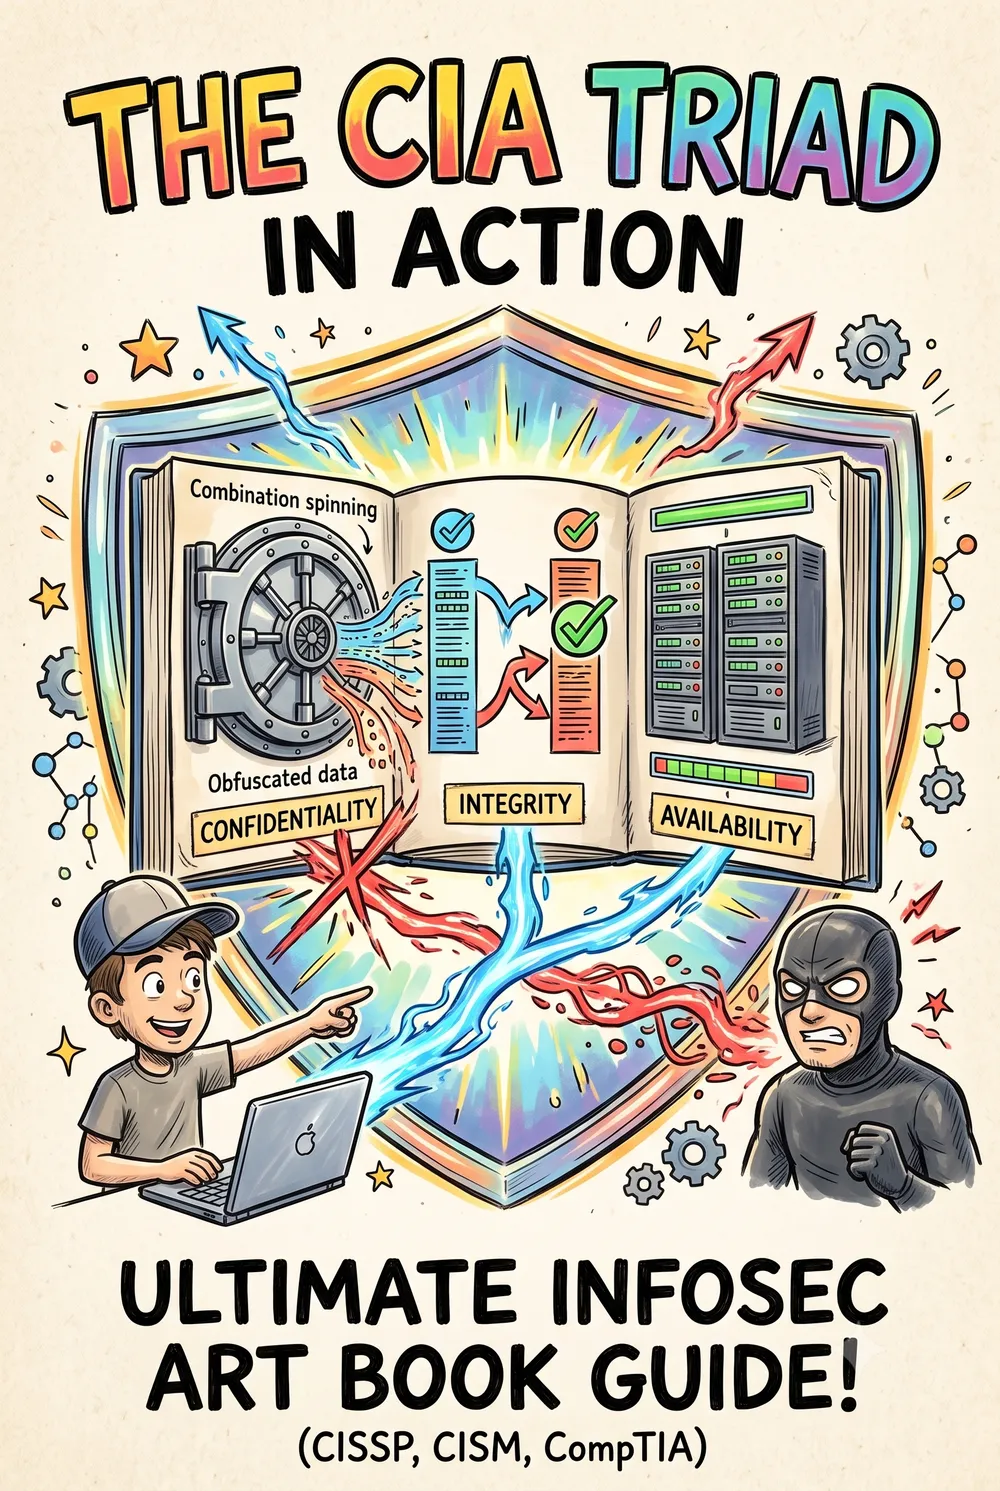
Issue #10
Mastering CIA
Issue #11
The SOC project for fresher :1
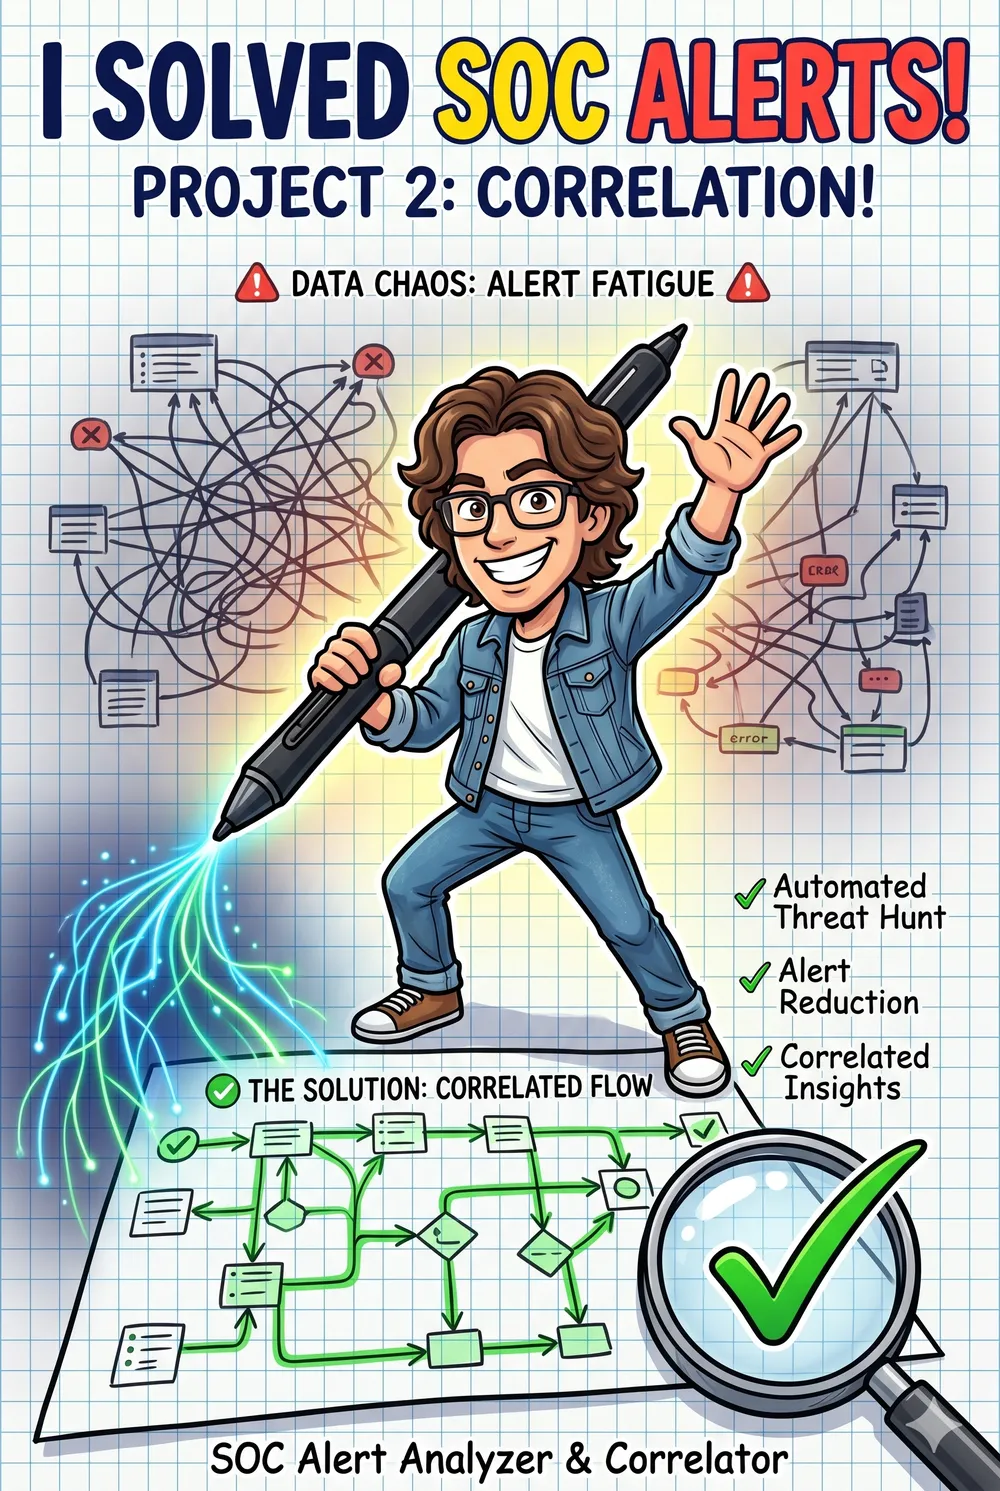
Issue #12
The SOC Project for Fresher :2
Issue #13
The Mechanics of Trust: How SSL Certificates Secure Connections
Issue #14
1. The CISSP Manager Mindset
Issue #15
2.The CIA Triad
Issue #16
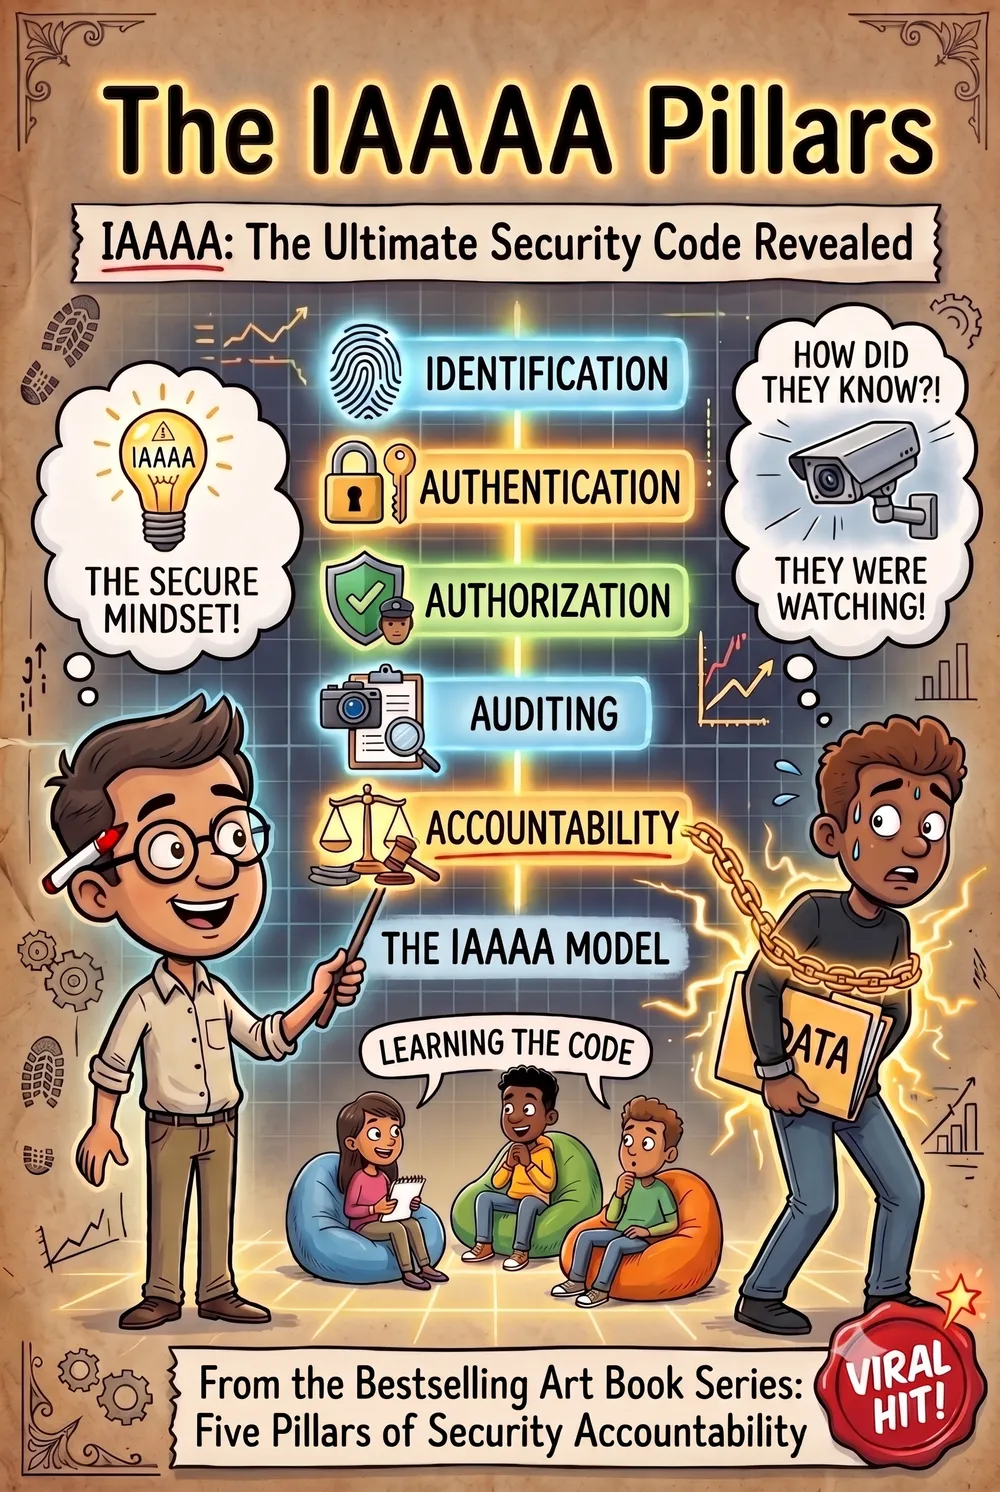
3. The_IAAAA_Pillars
Issue #17
4. Non-Repudiation
Issue #18
5. Mastering_the_CISSP_Mindset
Issue #19
6. Aligning Security Functions
Issue #20
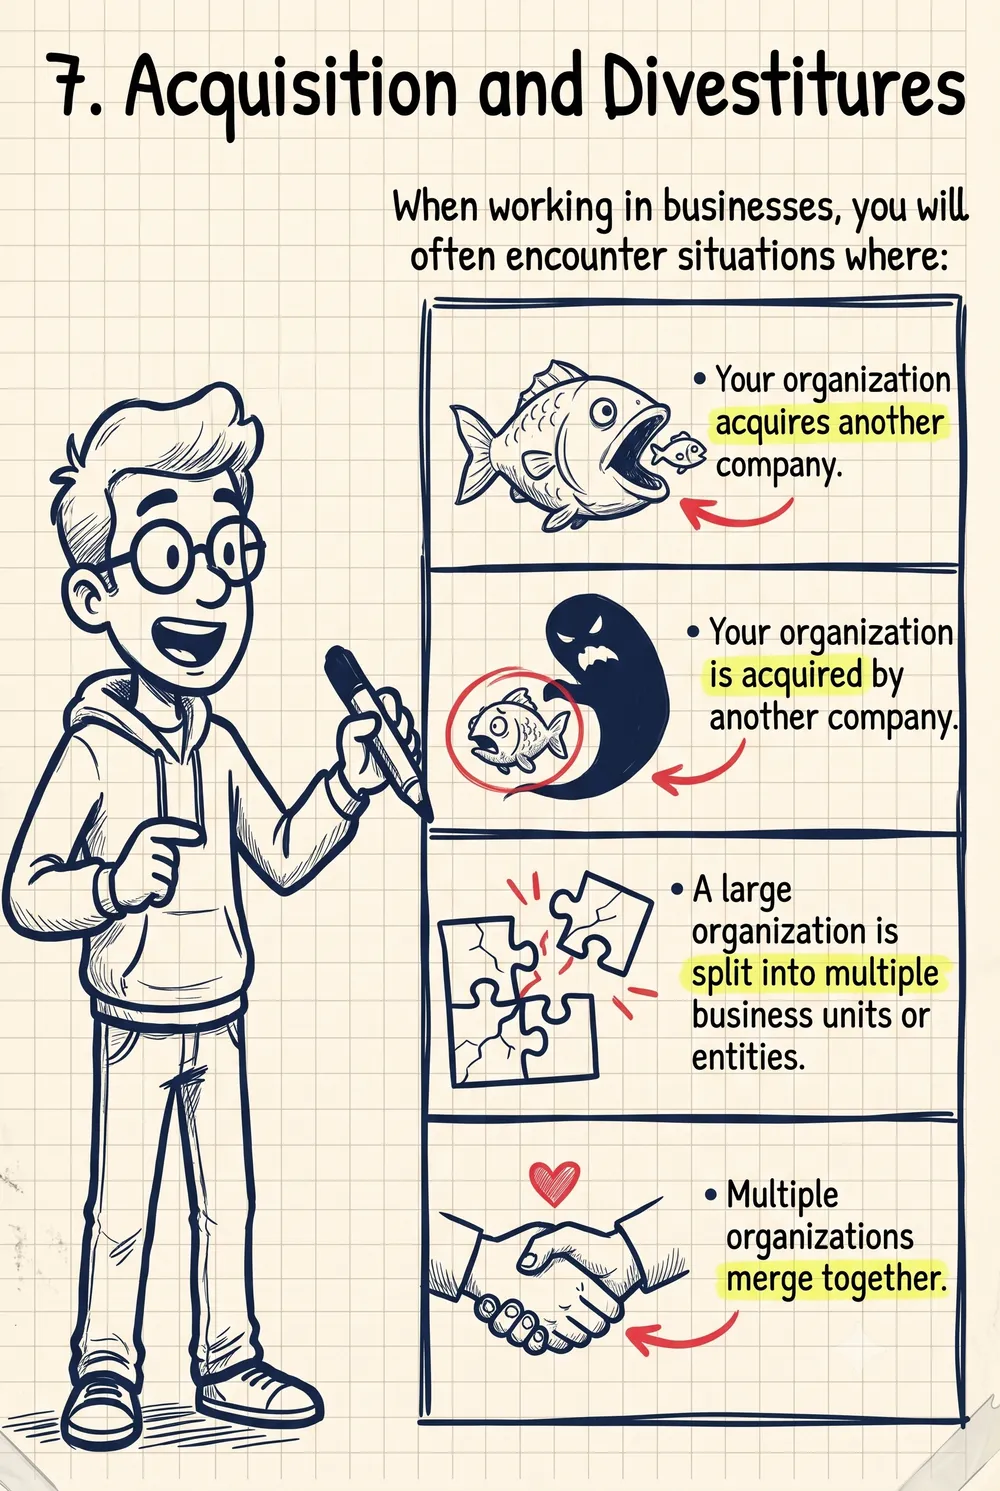
7 .Acquisition and Divestitures
Issue #21
8. Security Governance Mindset
Issue #22
9. Security_Roles
Issue #23
10. Illustrated CISSP Frameworks
Issue #24
11. Due Care and Due Diligence
Issue #25
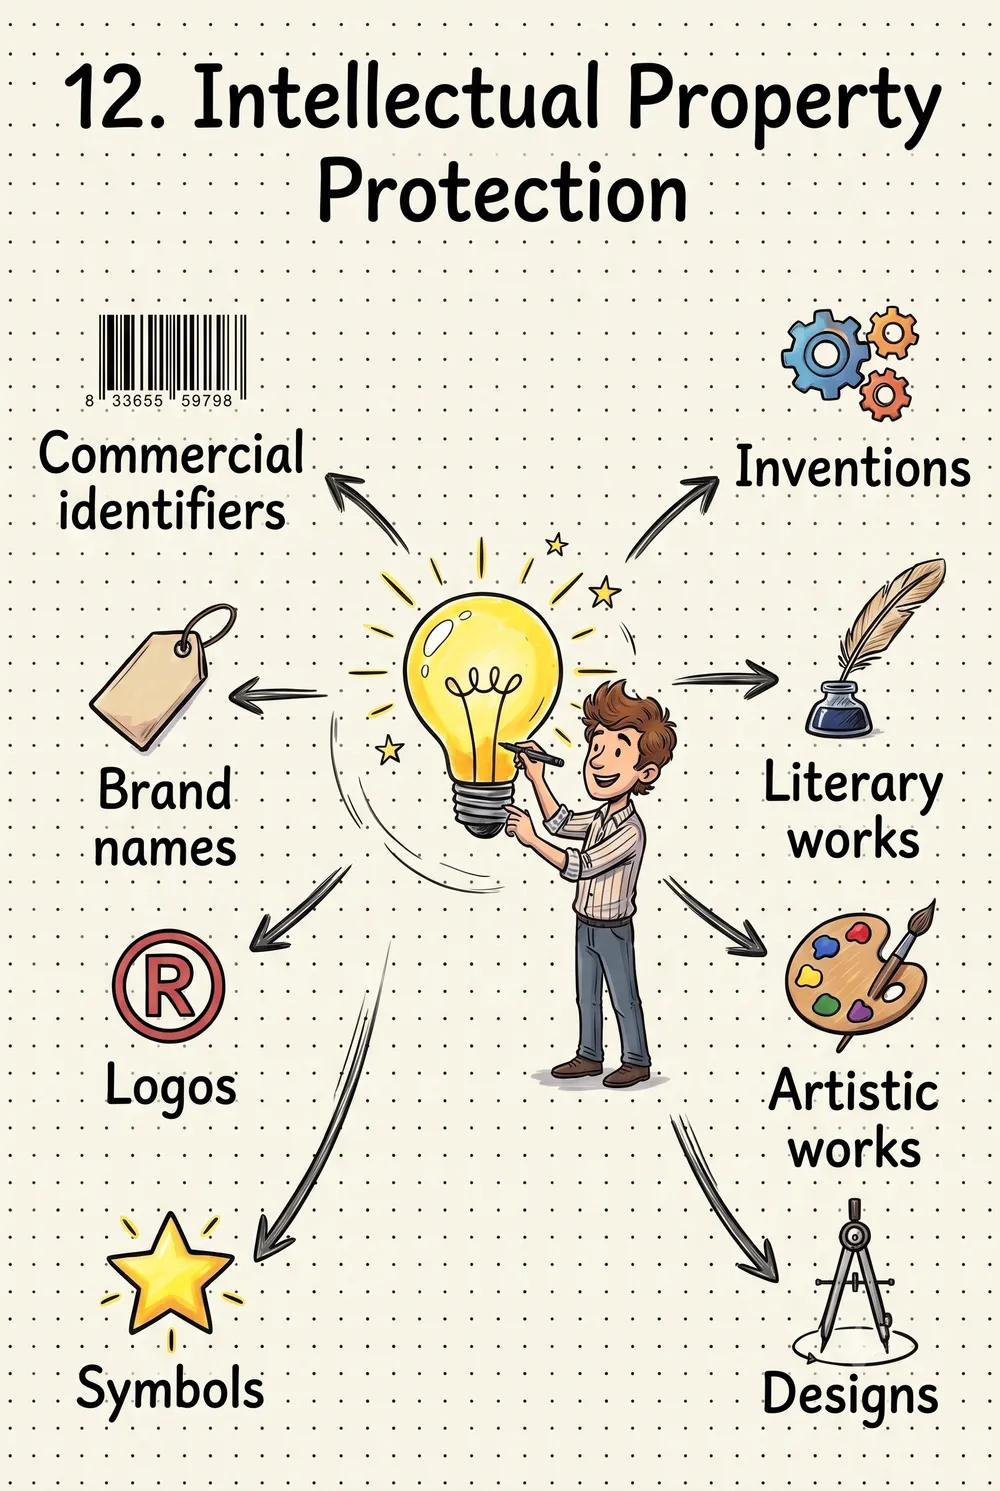
12. Intellectual Property Protection
Issue #26
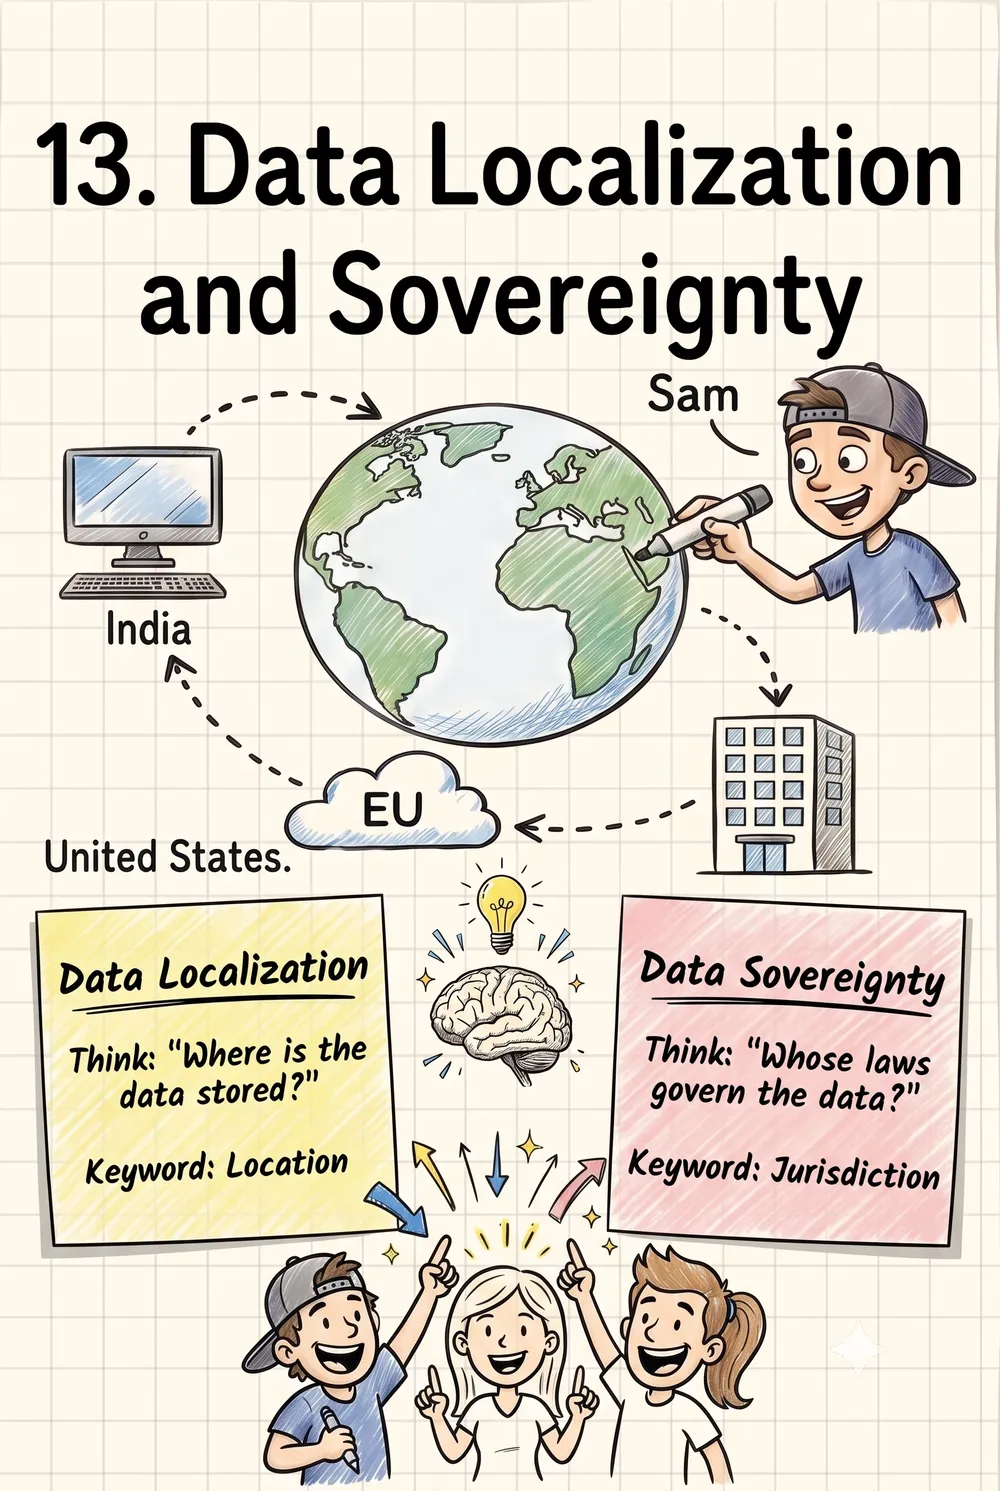
13. Data Localization and Sovereignty
Issue #27
14. Import and Export Laws
Issue #28
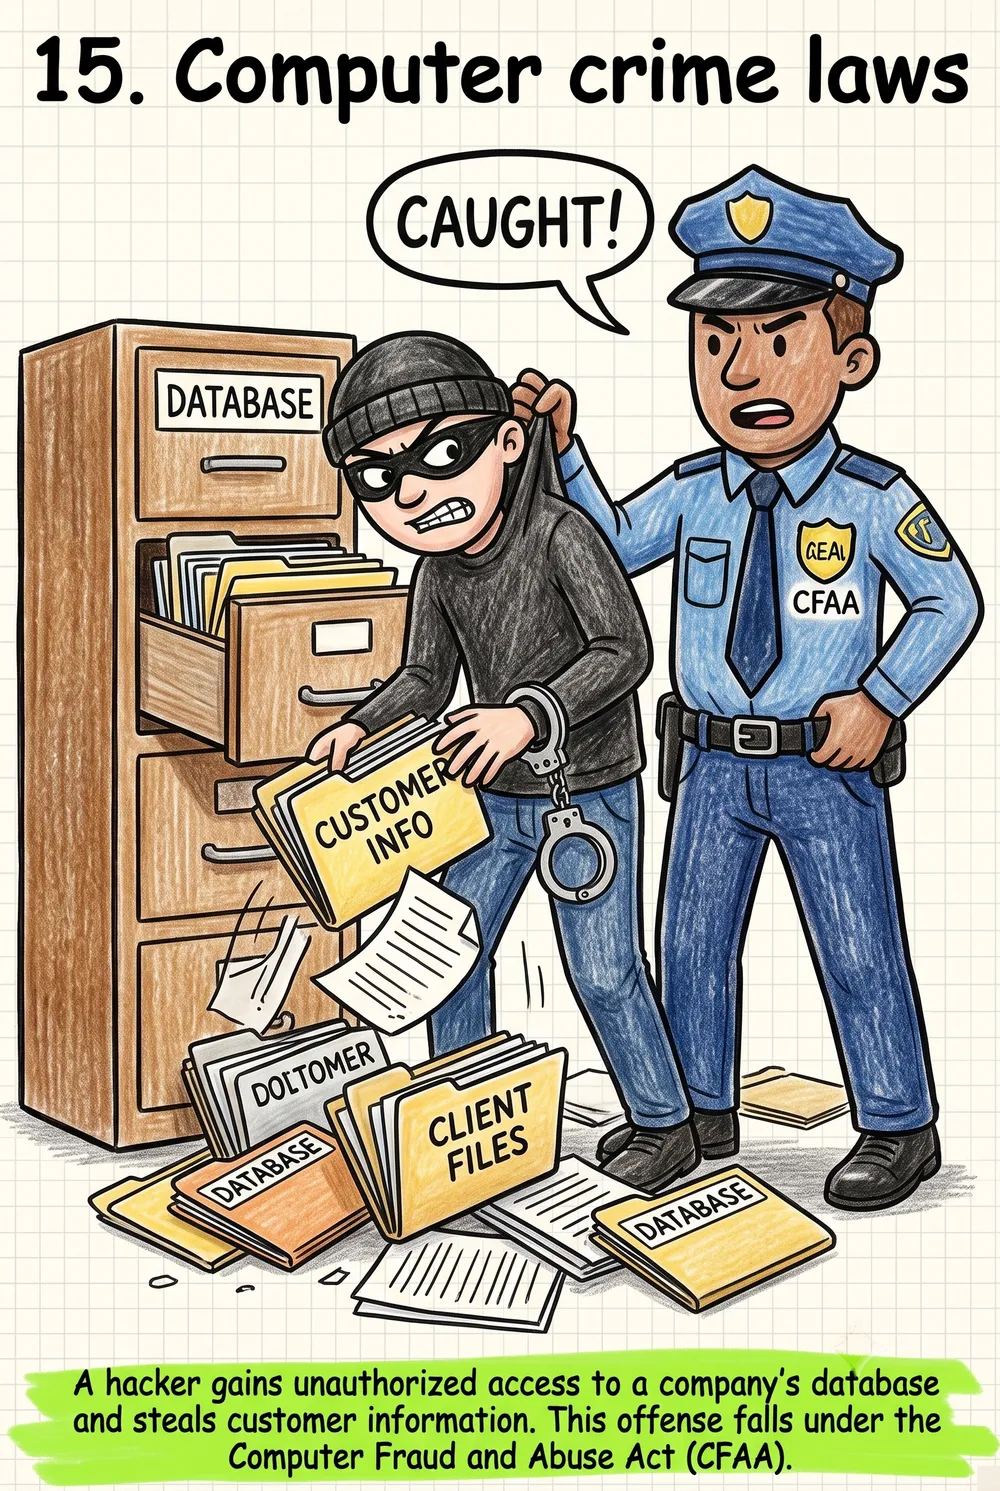
15. Computer crime laws
Issue #29
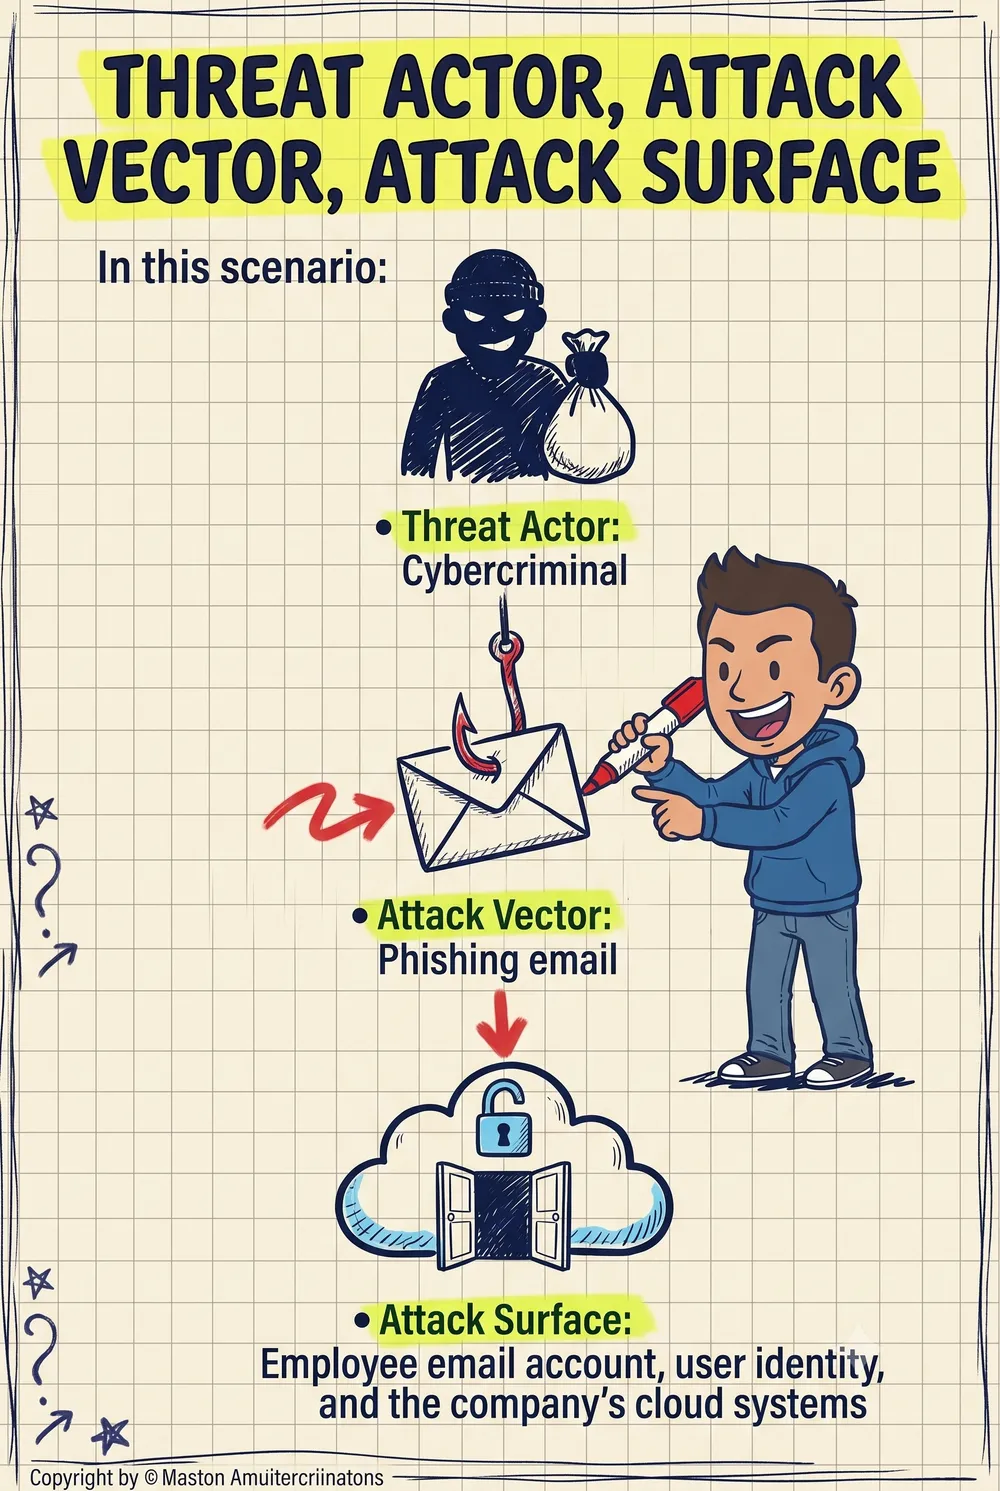
Threat Actor Attack Vector Attack Surface
Issue #30
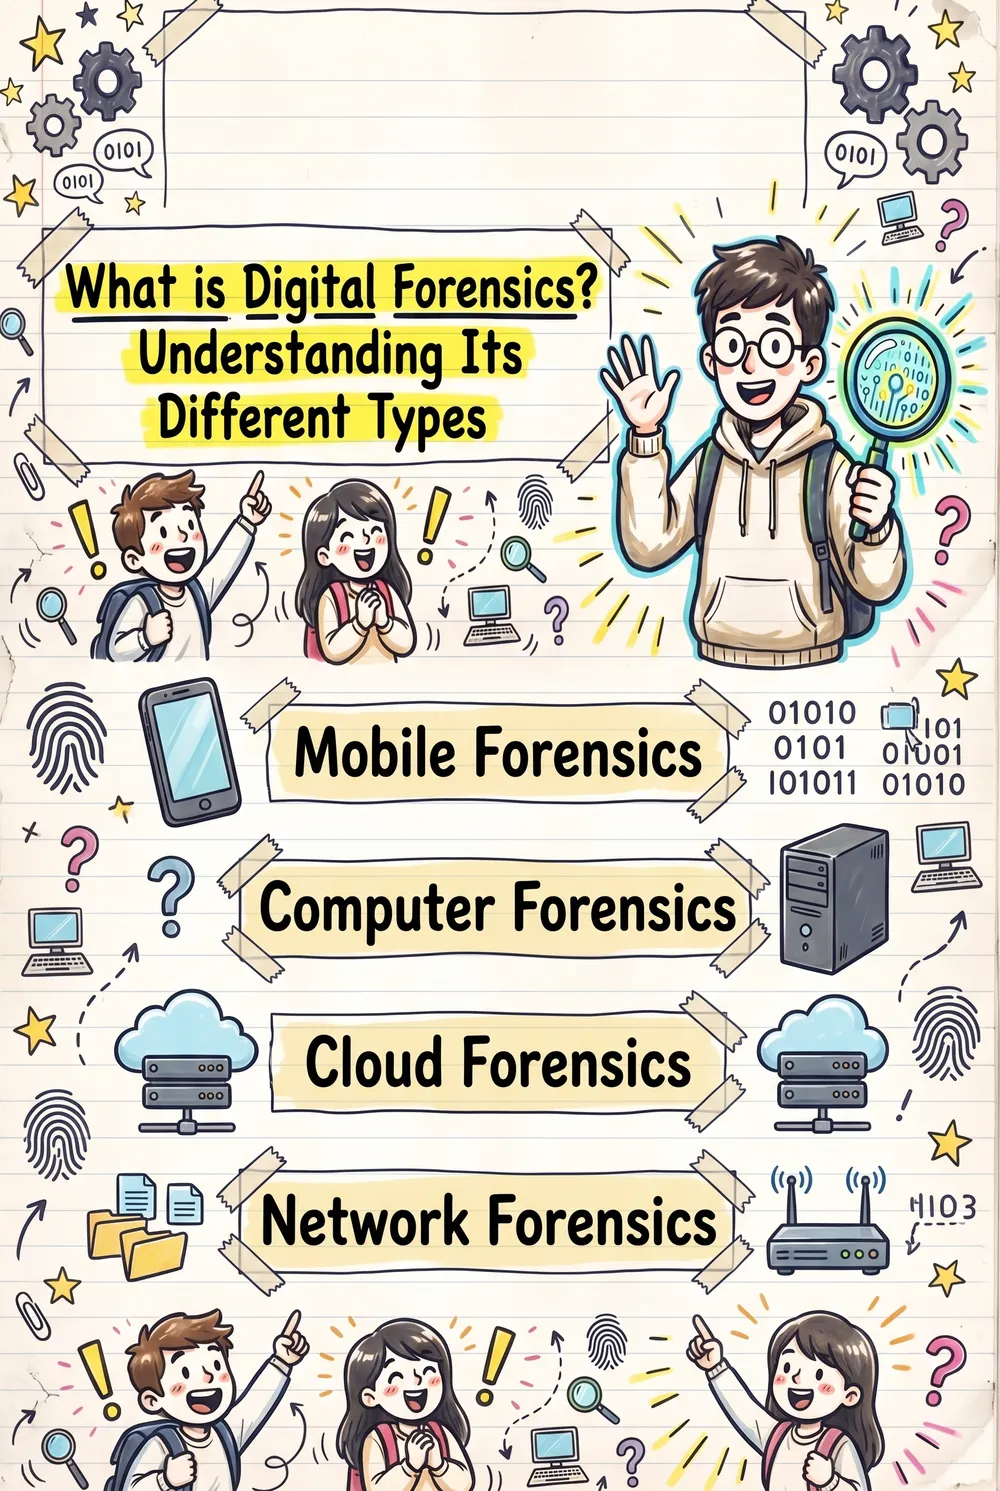
What is Digital Forensics ?
Issue #31
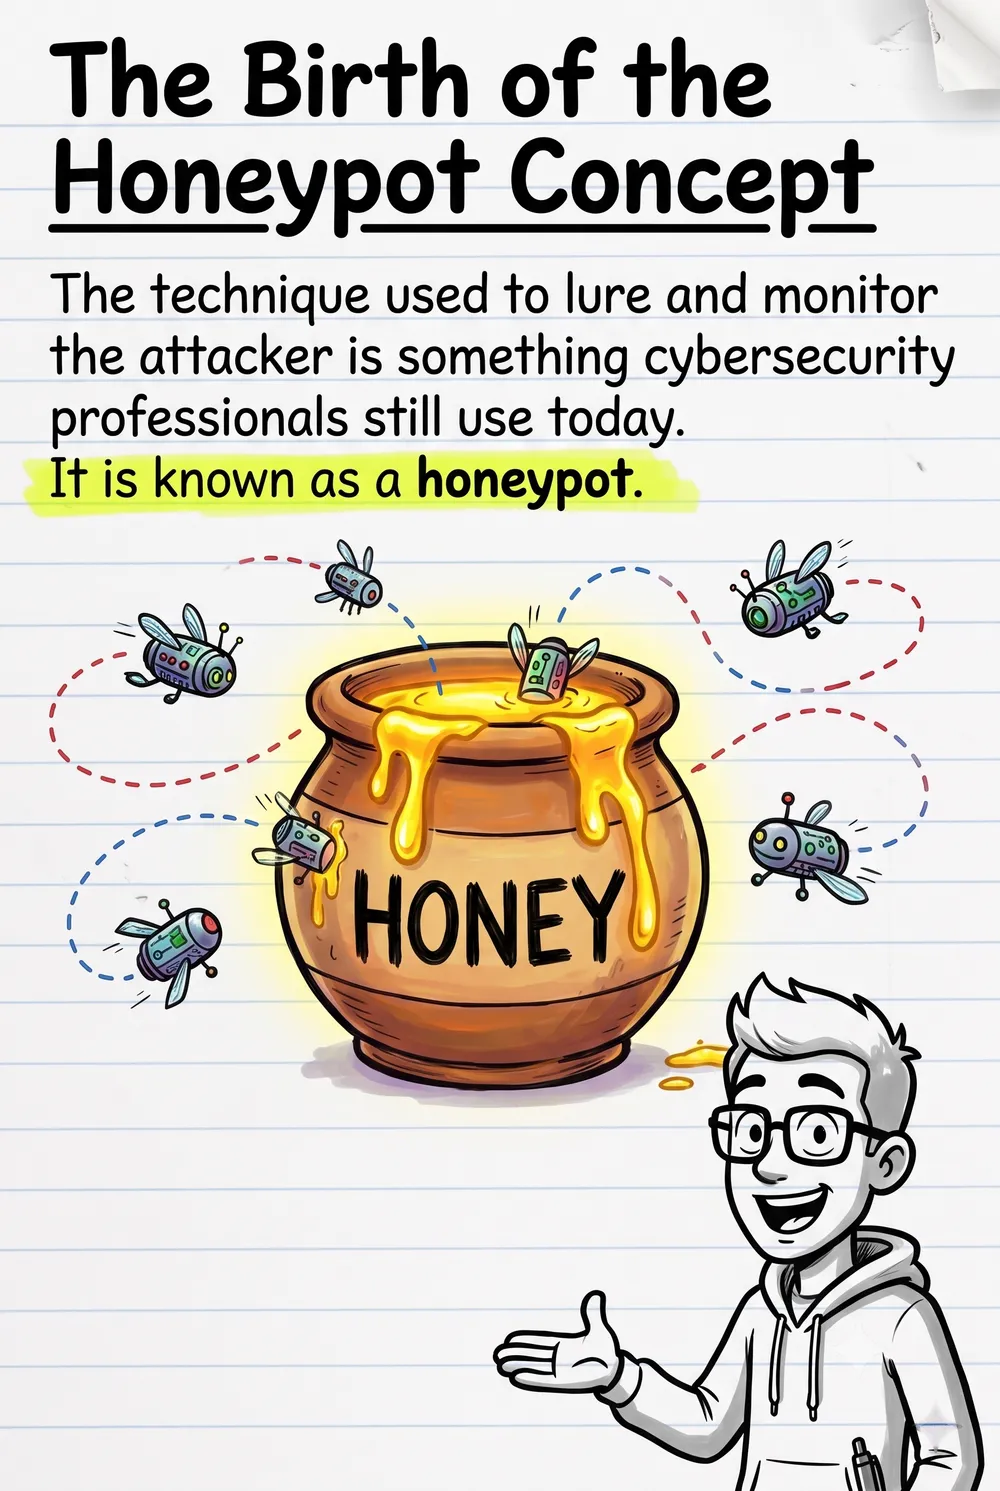
The birth of the honeypot concept
Issue #32
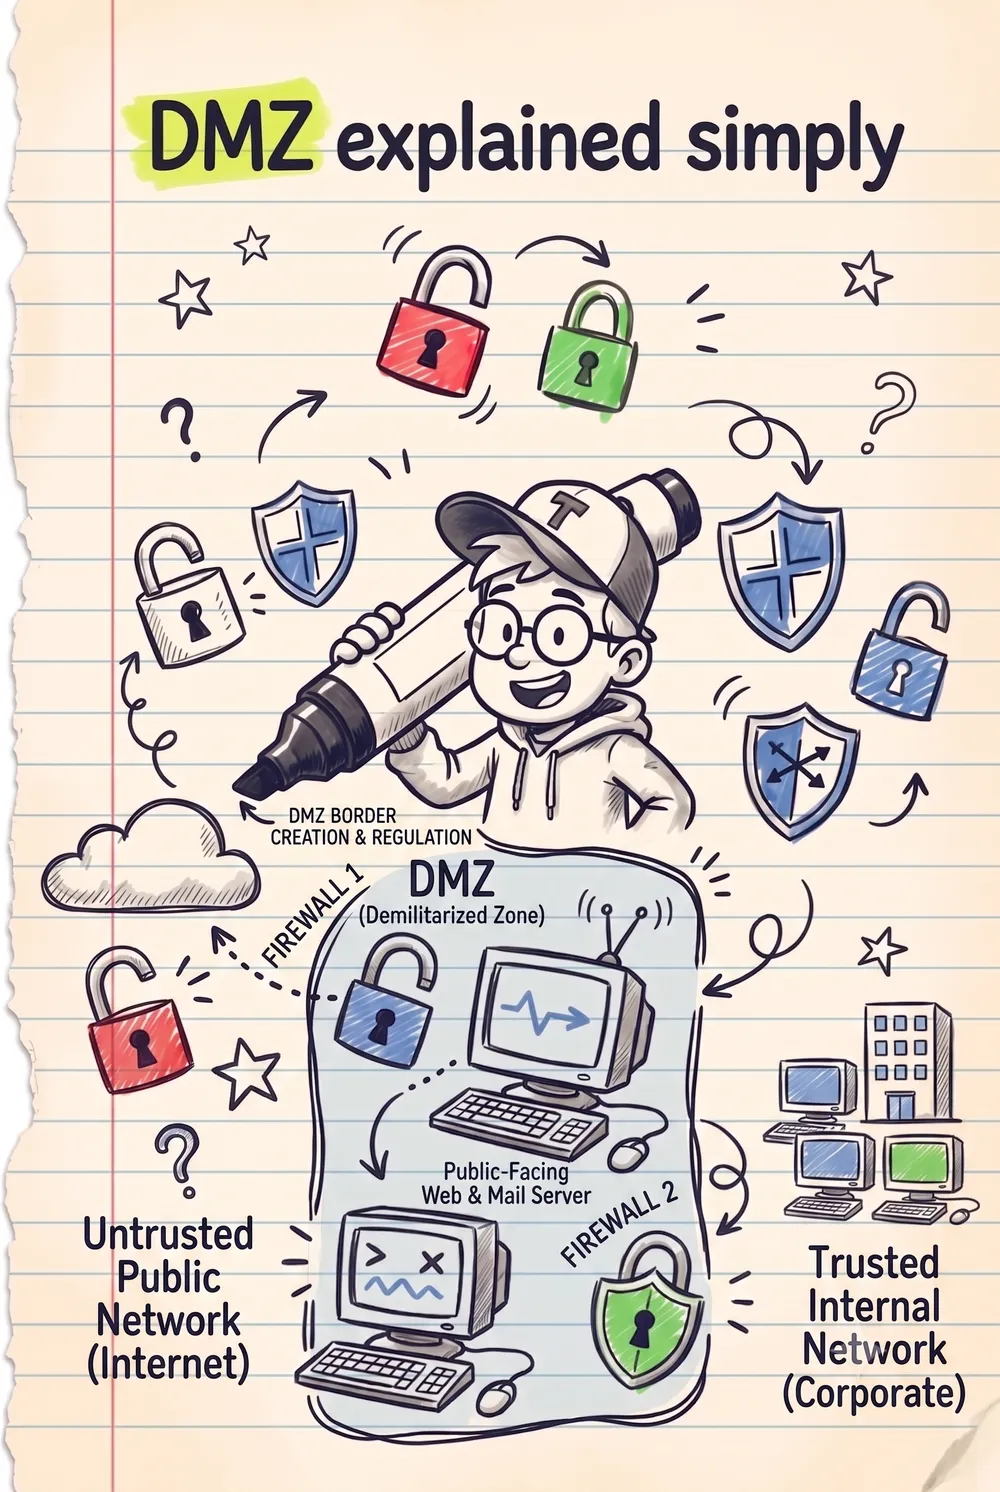
DMZ Explained Simply
Issue #33
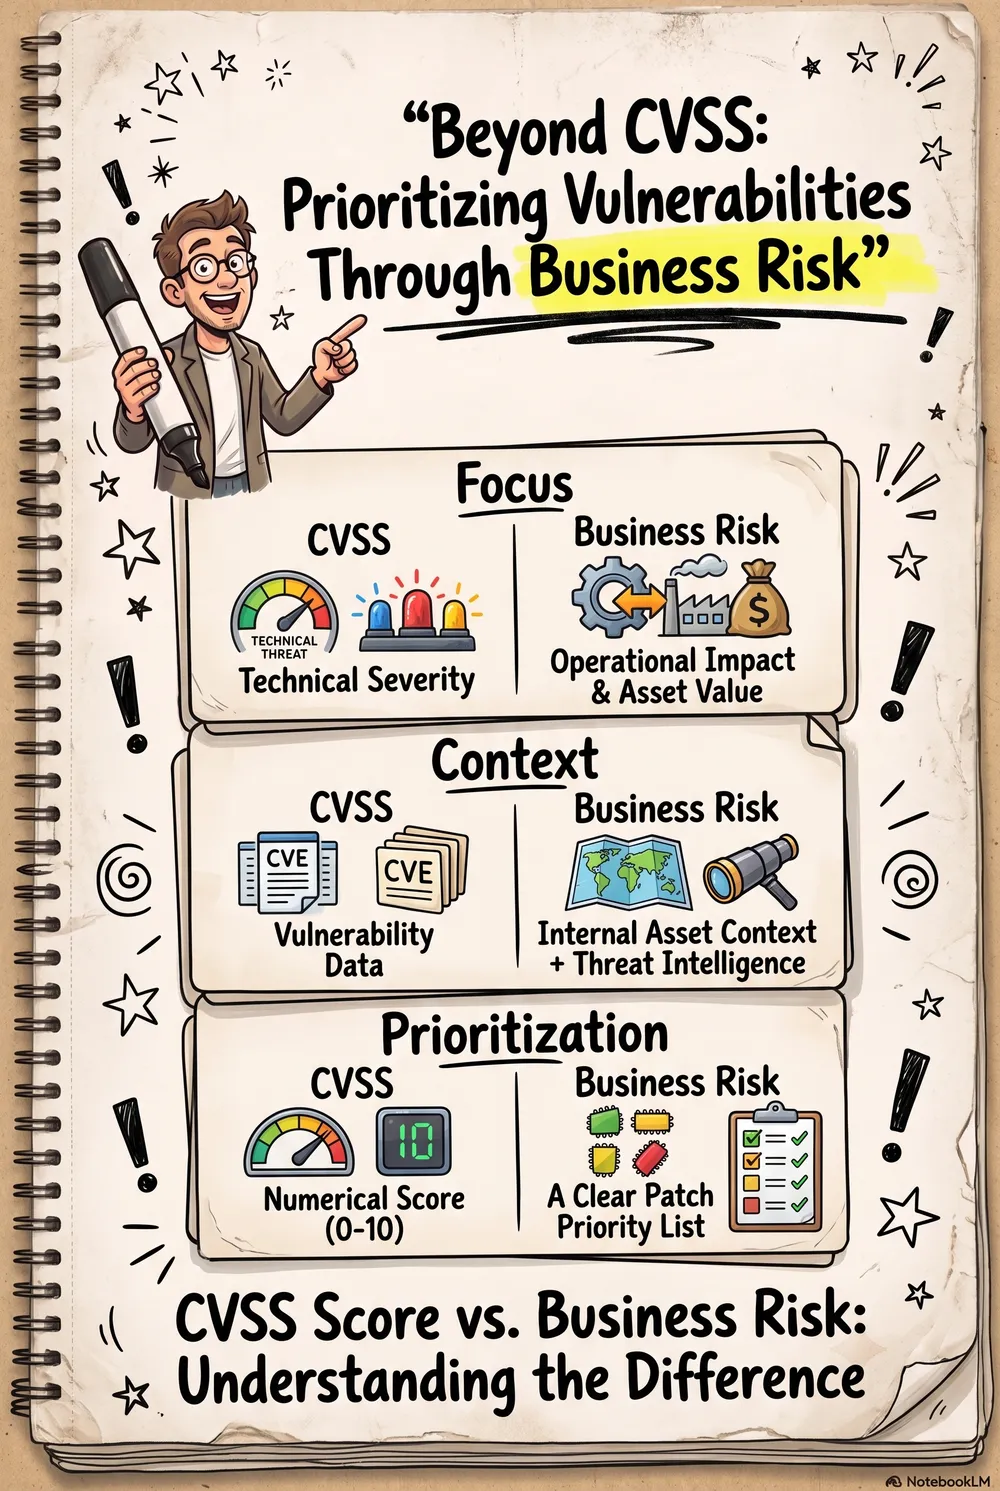
Prioritizing Beyond CVSS
Issue #34
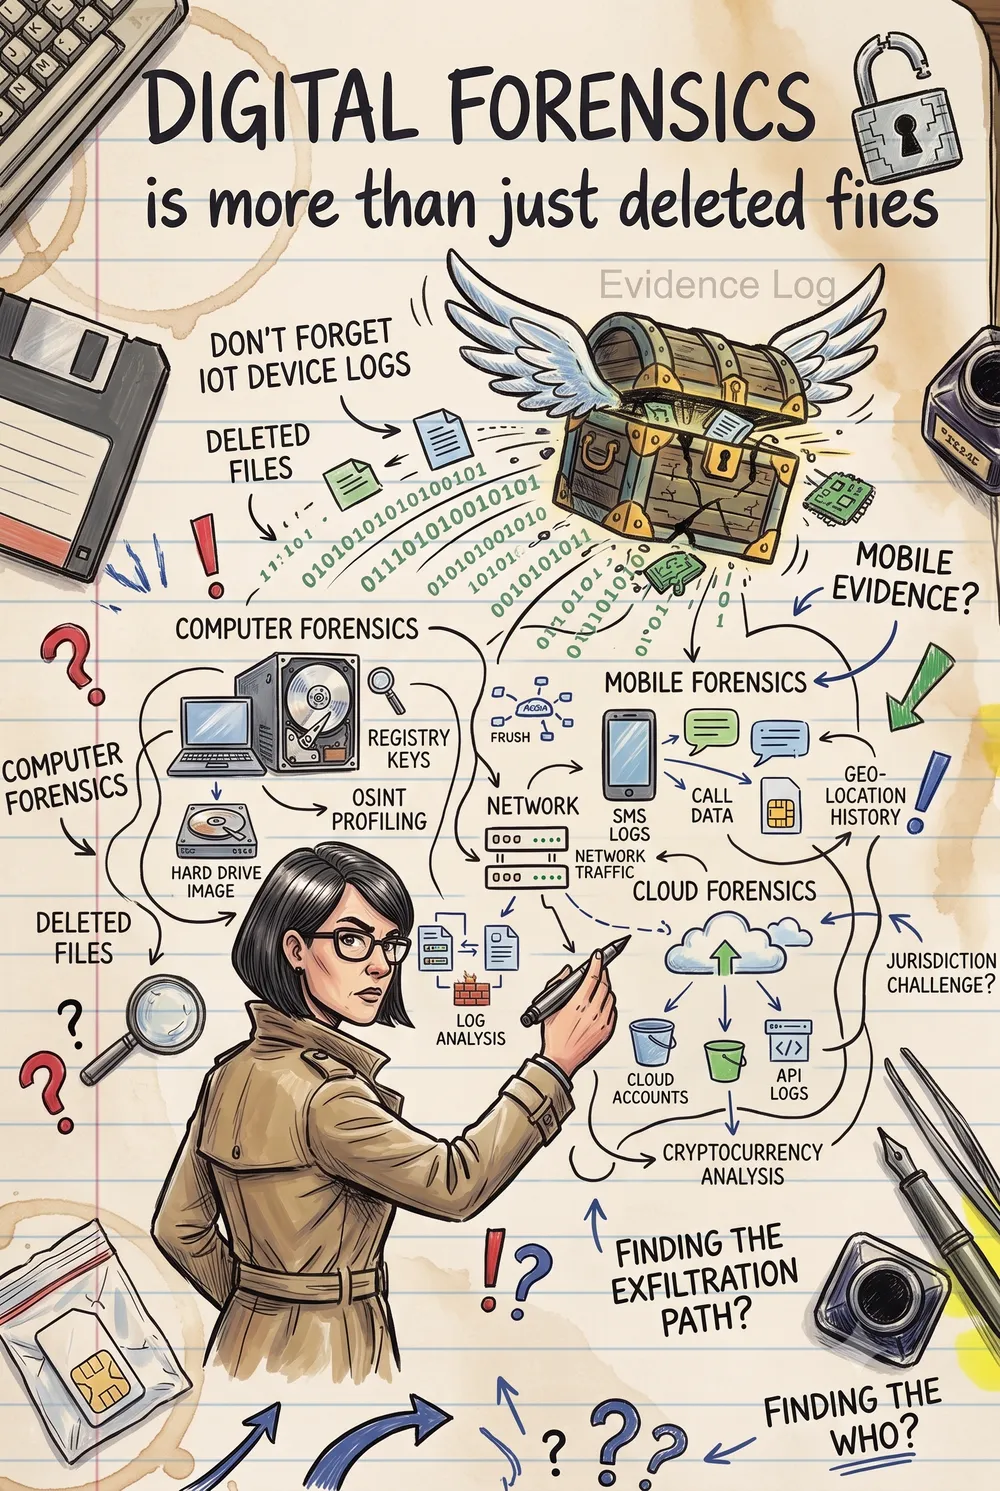
Digital Forensics and Its Branches
Issue #35
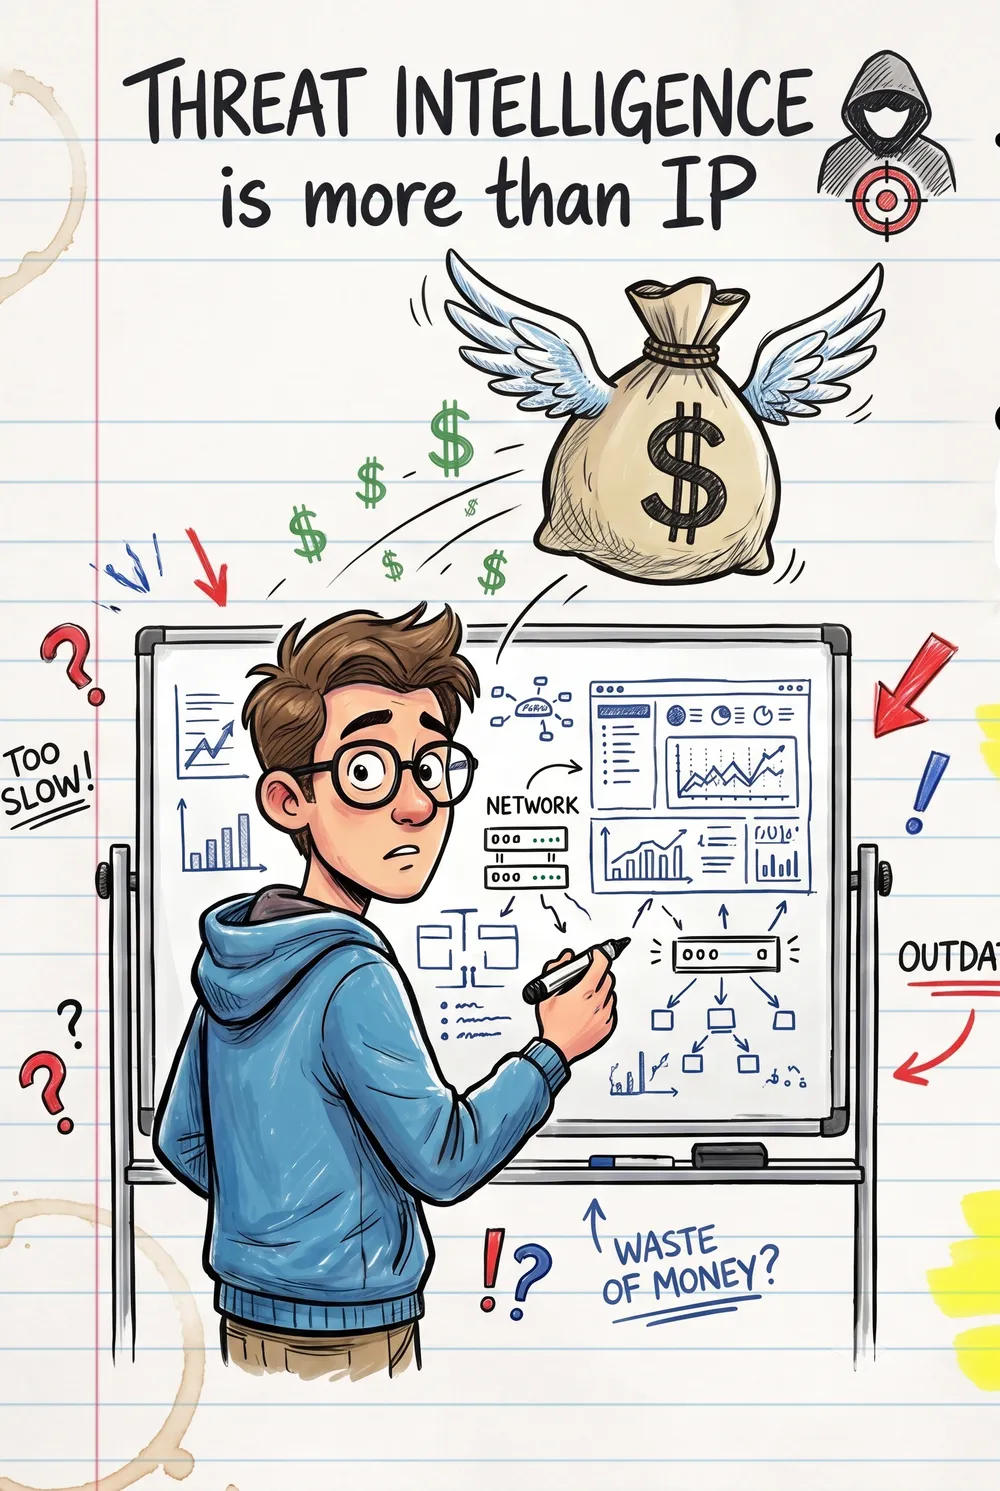
Threat Intelligence Is More Than IP
Issue #36
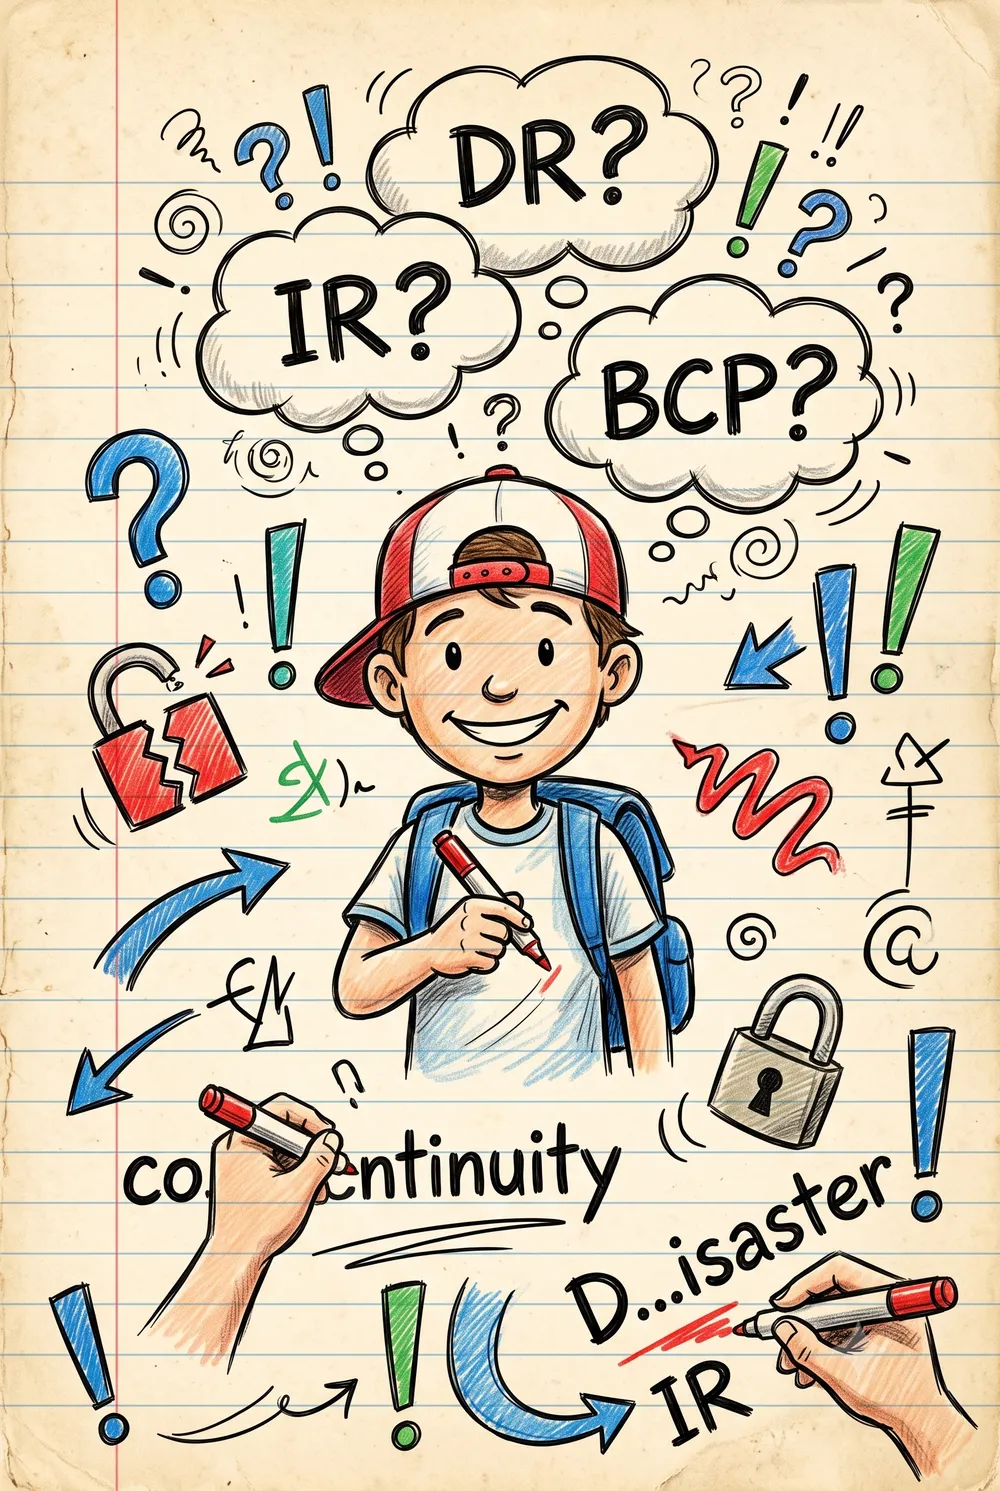
IR DR and BCP Essentials
Issue #37
Build a CSPM Tool
Issue #38
Malware Sandbox Project
Issue #39
Ransomware Traffic Detector Project
Issue #40
Civil Versus Criminal Law
Issue #41
SOC Analyst Roadmap 2026
Issue #42
1. Kerberos Simply Explained
Issue #43
2. RADIUS Simply Explained
Issue #44
3. TACACS Simply Explained
Issue #45
PAP CHAP EAP simply Explained
Issue #46
GDPR Playbook
Issue #47
Policies Procedures Guidelines Frameworks
Issue #48
Risk Management Questions
Issue #49
Security Audit Log Essentials
Issue #50
Domain5 : Identity and Access Management
Issue #51
1. Type 1 Authentication
Issue #52
2. Something You Have
Issue #53
Type 3 Authentication Something you are
Issue #54
4. Authorization
Issue #55
5. Accountability and Auditing
Issue #56
6. Access Control Systems
Issue #57
7. Policy Decision Point, Policy Enforcement Point and Service Account Management
Issue #58
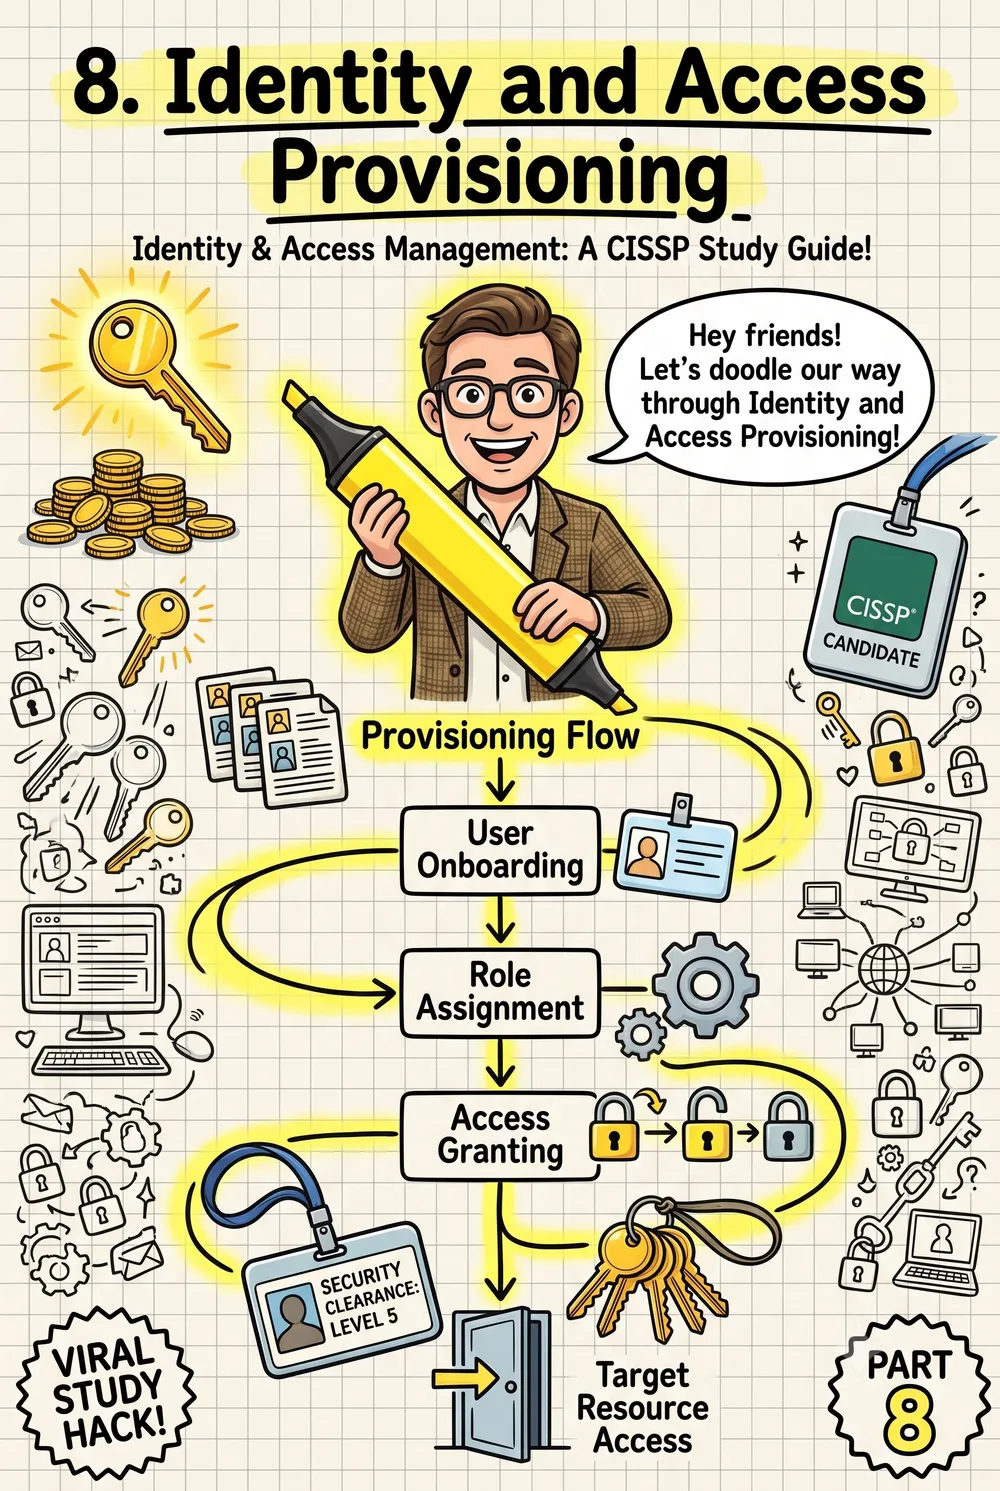
8. Identity and Access Provisioning
Issue #59
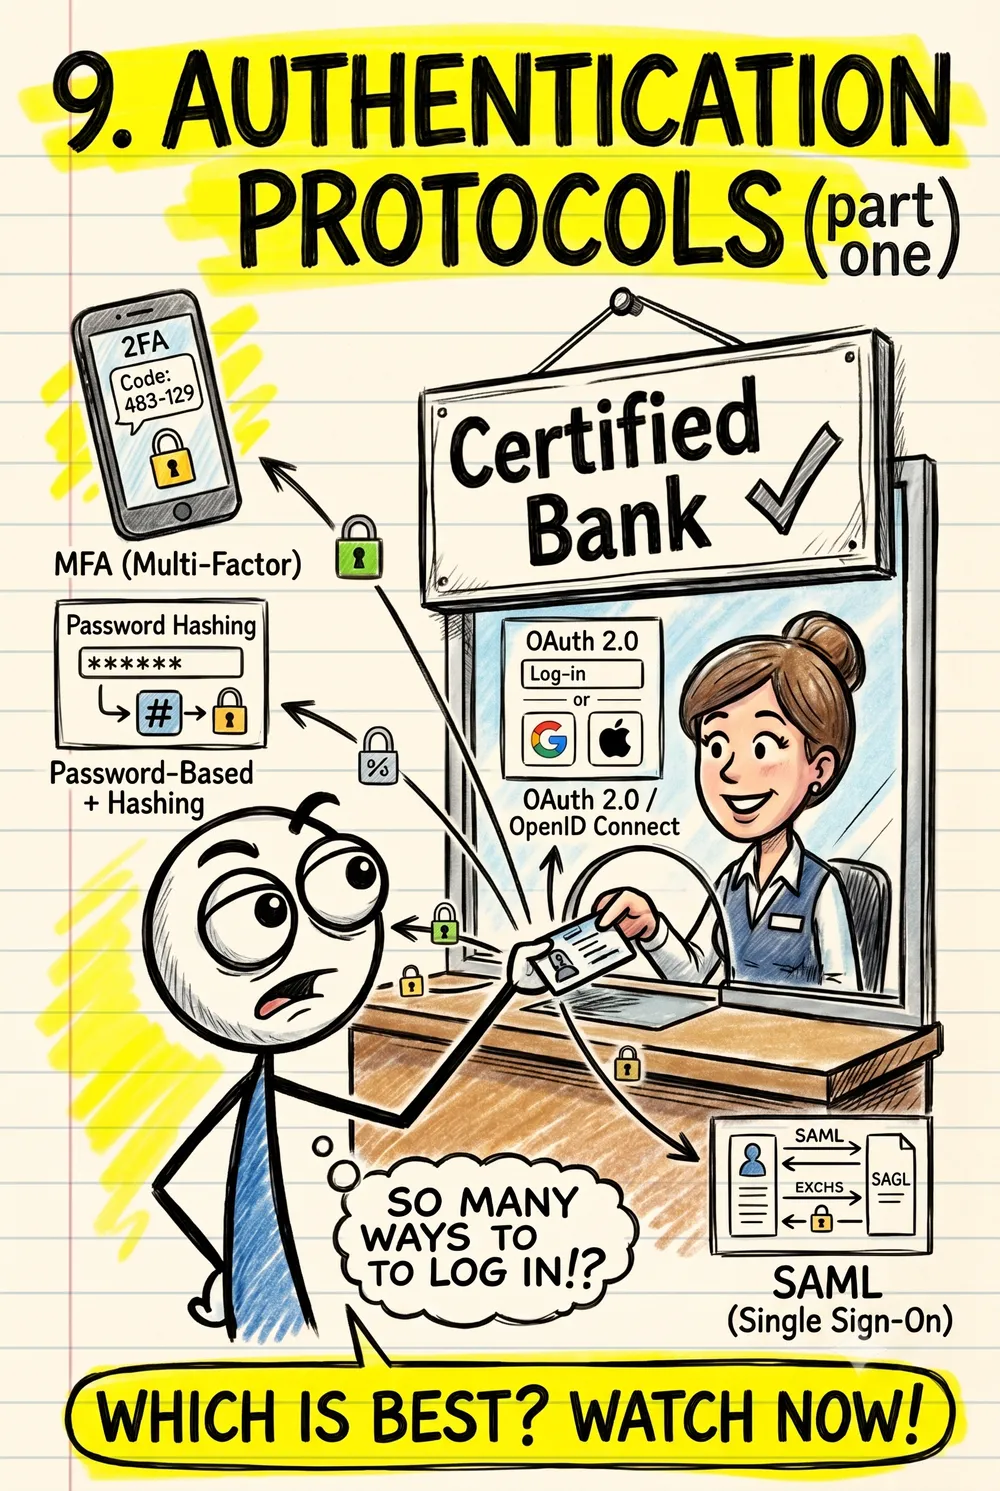
9. Authentication Protocols and Kerberos
Issue #60
Authentication Protocol Part 2
Issue #61
Domain 2: What we will be covering
Issue #62
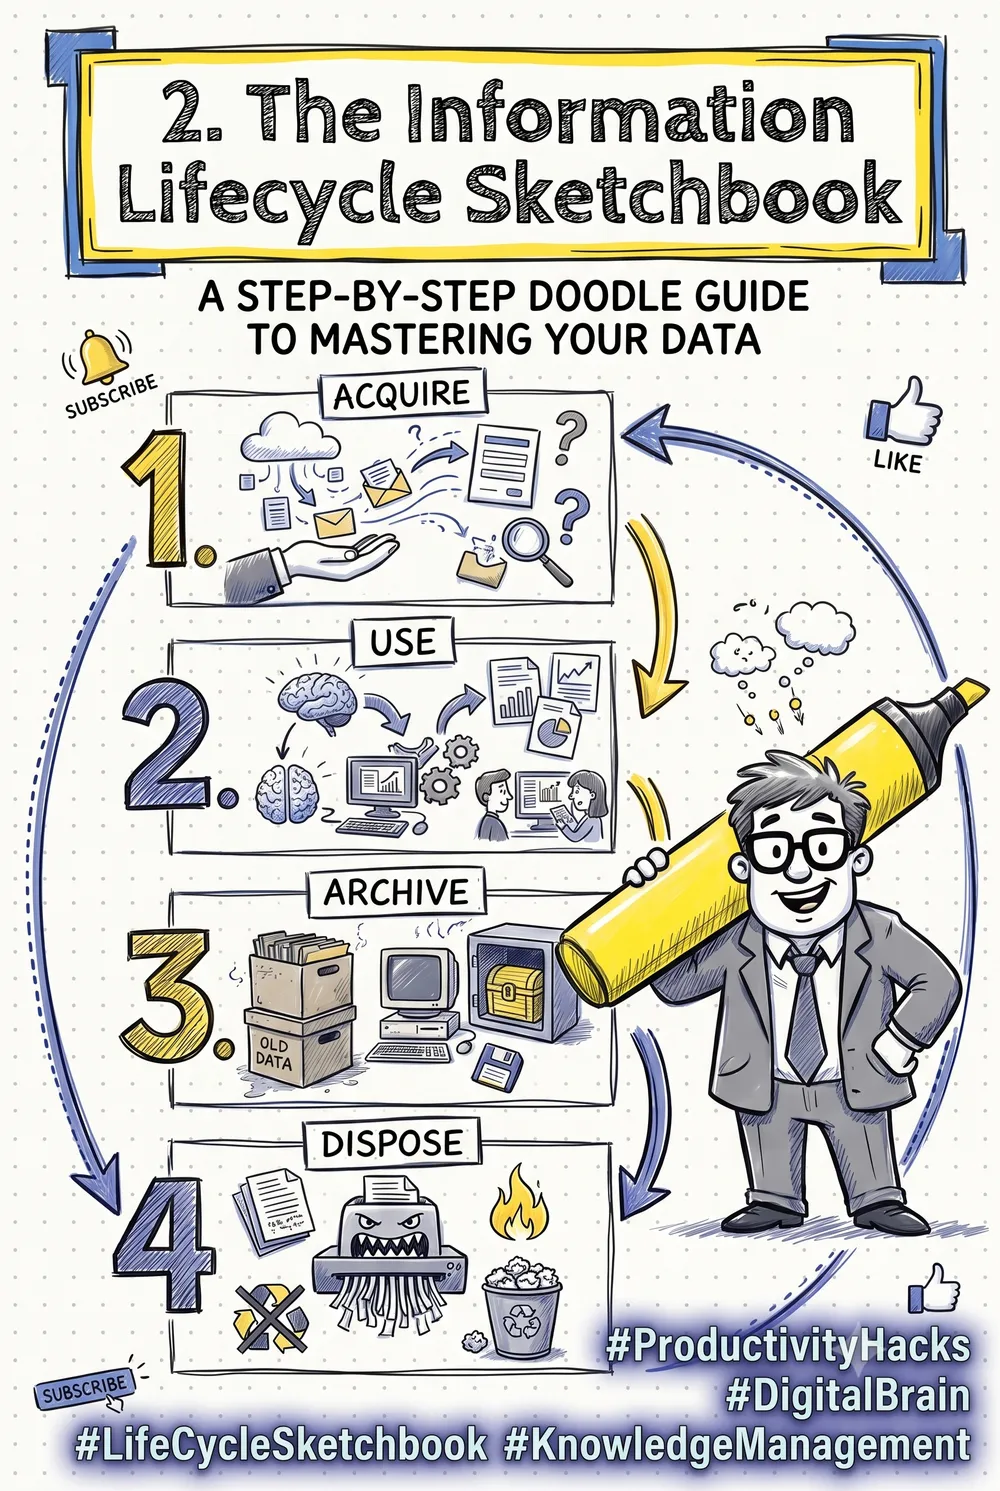
1. The Information Lifecycle Sketchbook
Issue #63
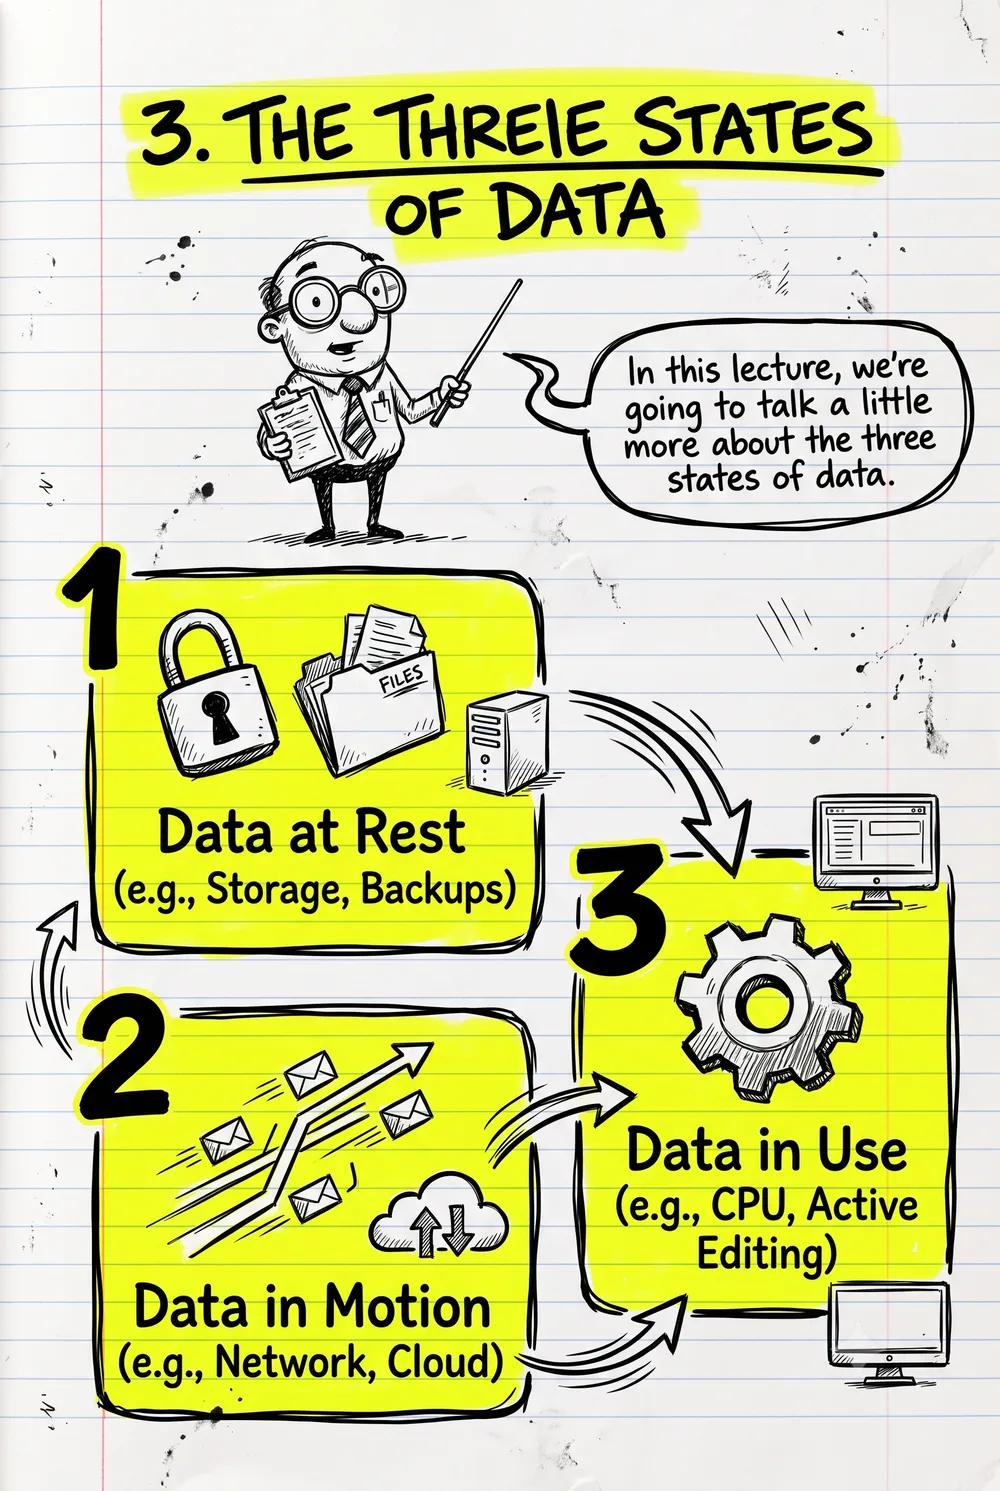
2. The Three States of Data
Issue #64
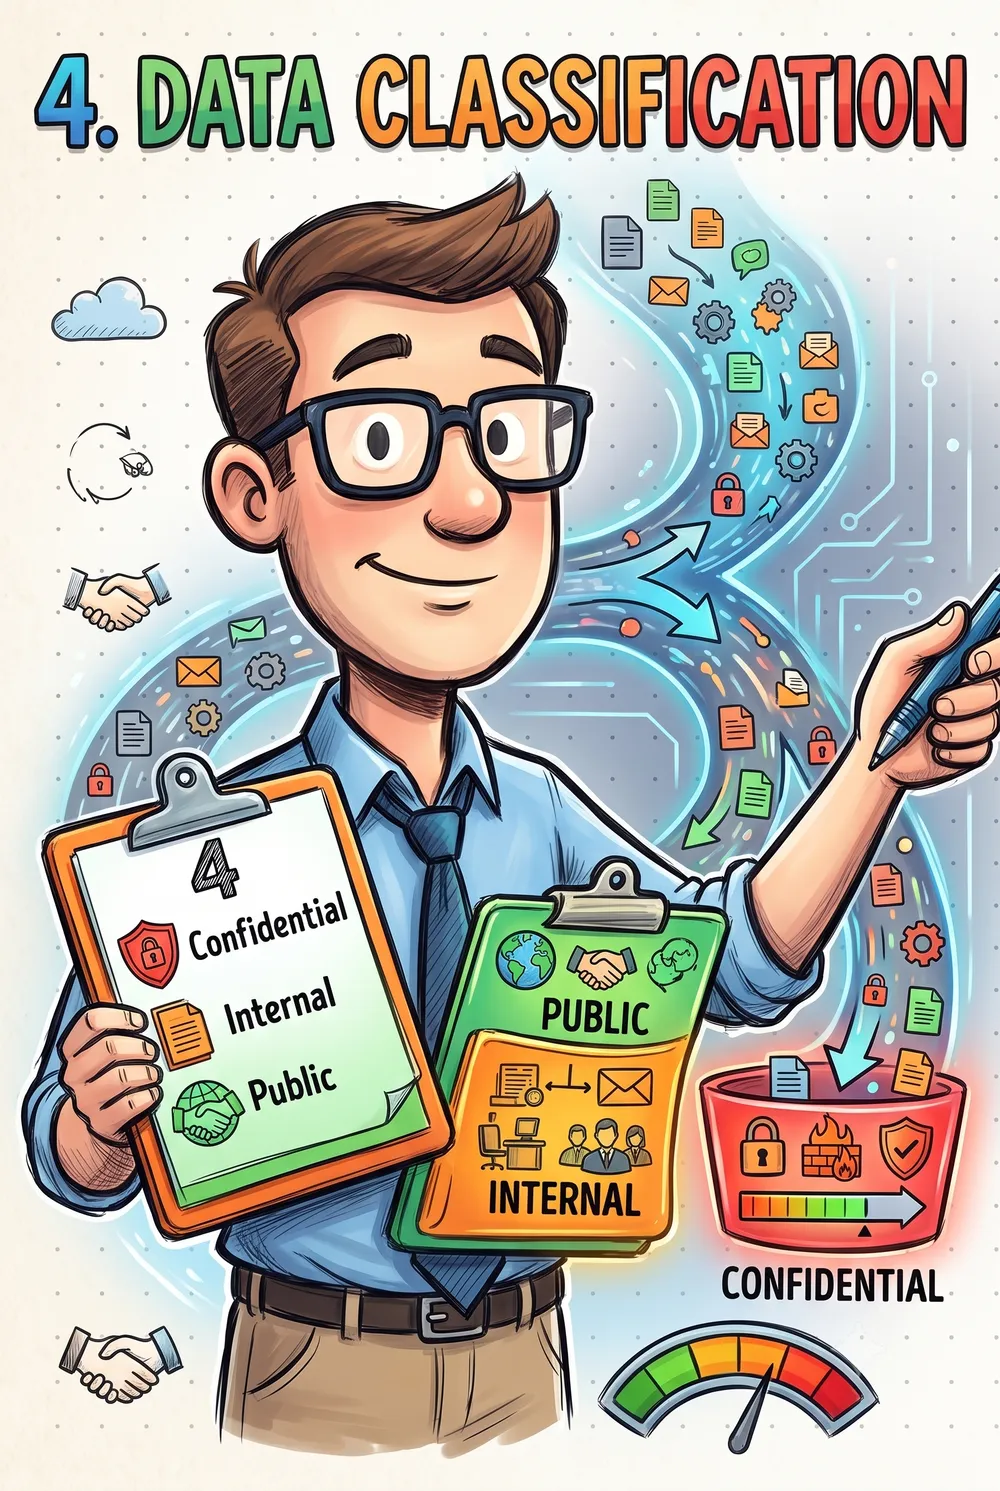
3. Data Classification and Clearance
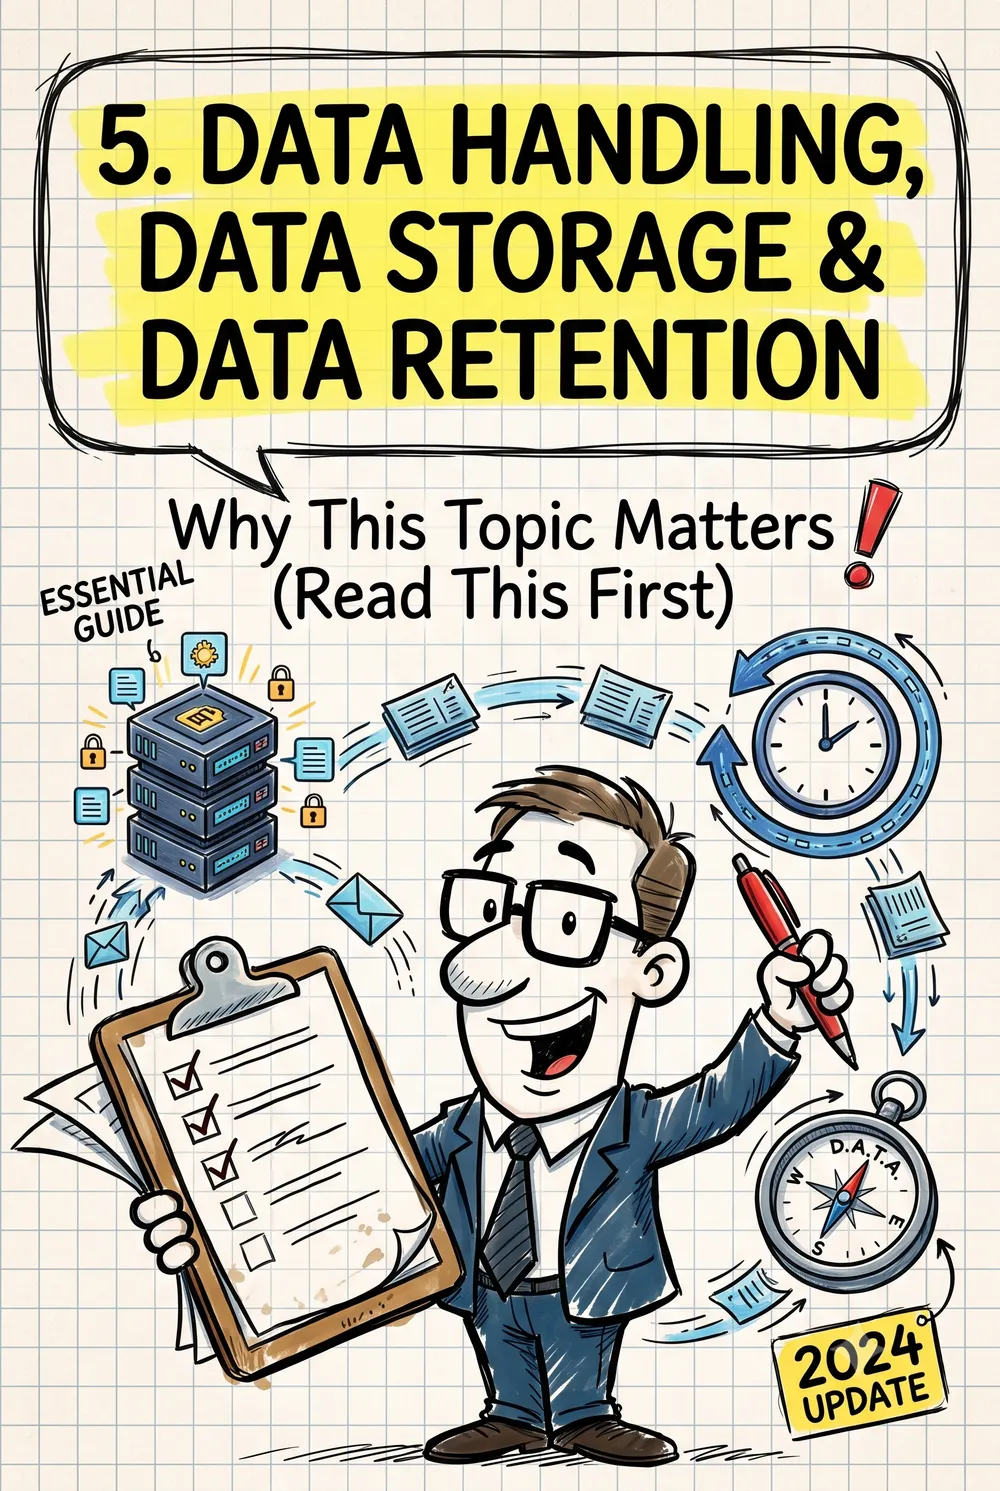
Issue #65
4. Data Handling Storage Retention
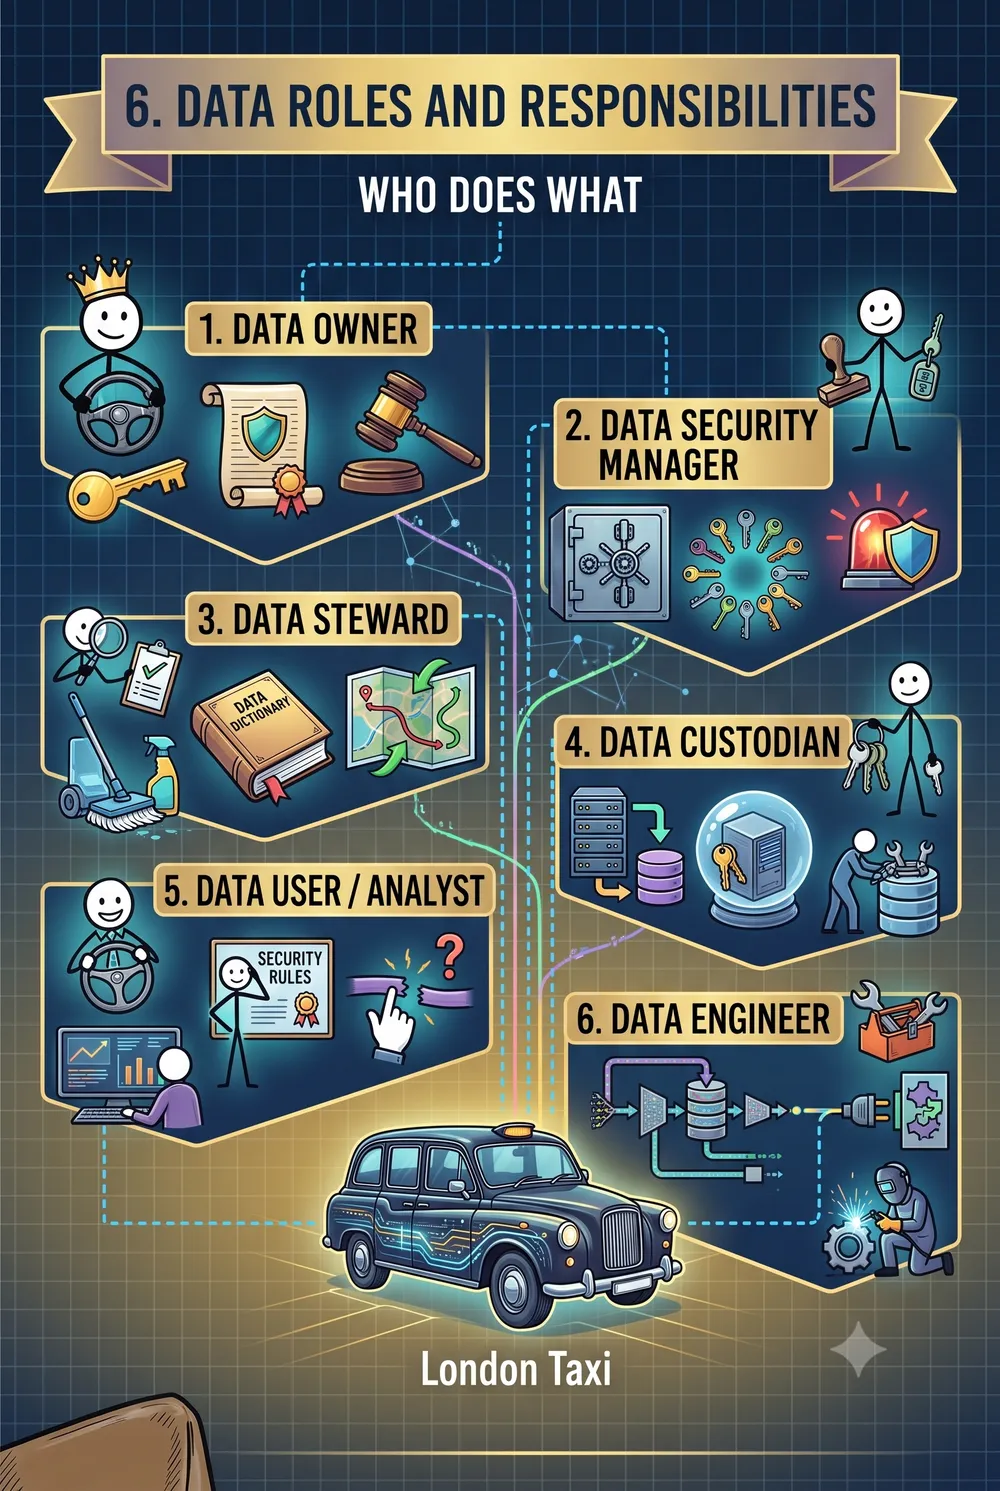
Issue #66
5. Data Roles and Responsibilities Who Does What
Issue #67
Hacking the Hackers
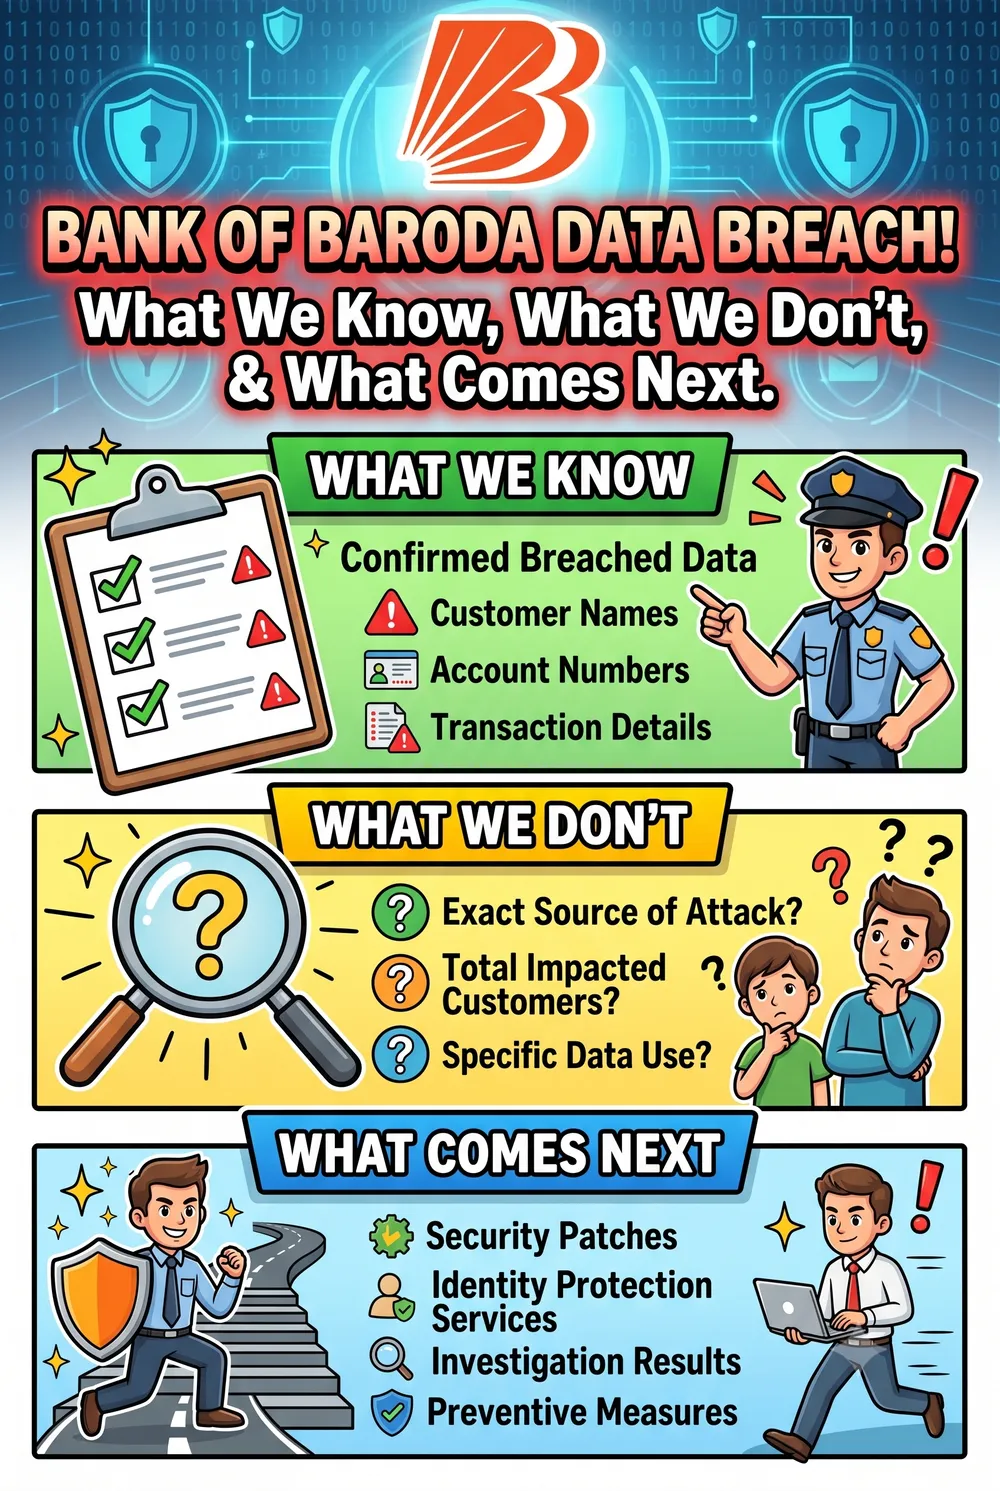
Issue #68
Bank Of Baroda Breach
Issue #69
Levi Strauss Cybersecurity Incident
Issue #70
Dark Patterns Simplified
Issue #71
Tata Electronics Incident

Issue #72
1. What is AAISM and its prerequisites

Issue #73
2.AAISM Certification and Maintenance

Issue #74
3. AAISM Overview Corelation between three domains

Issue #75
4. AAISM Is Not a Data Science Certification

Issue #76
The Broken Chain of Trust

Issue #77
5. Start With Governance

Issue #78
6. Think in AI Lifecycle, not one time Deployment

Issue #79
7. AI for Security” and “Security for AI”

Issue #80
8. Risk Control Assurance
Issue #81
9. AAISM Formula
Issue #82
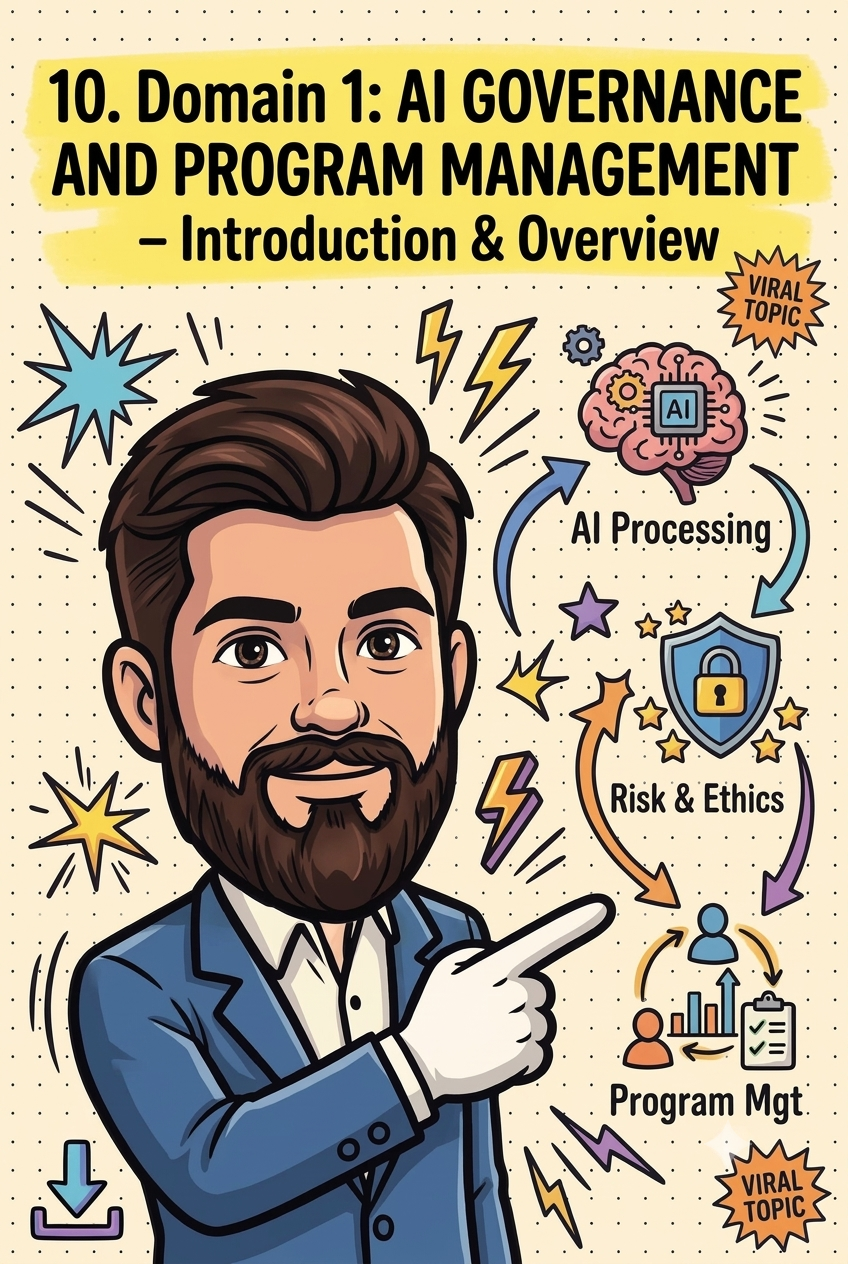
10. Domain 1 AI Governance and Program Management – Introduction & Overview
Issue #83
Unmasking_the_Boss_Scam
Issue #84
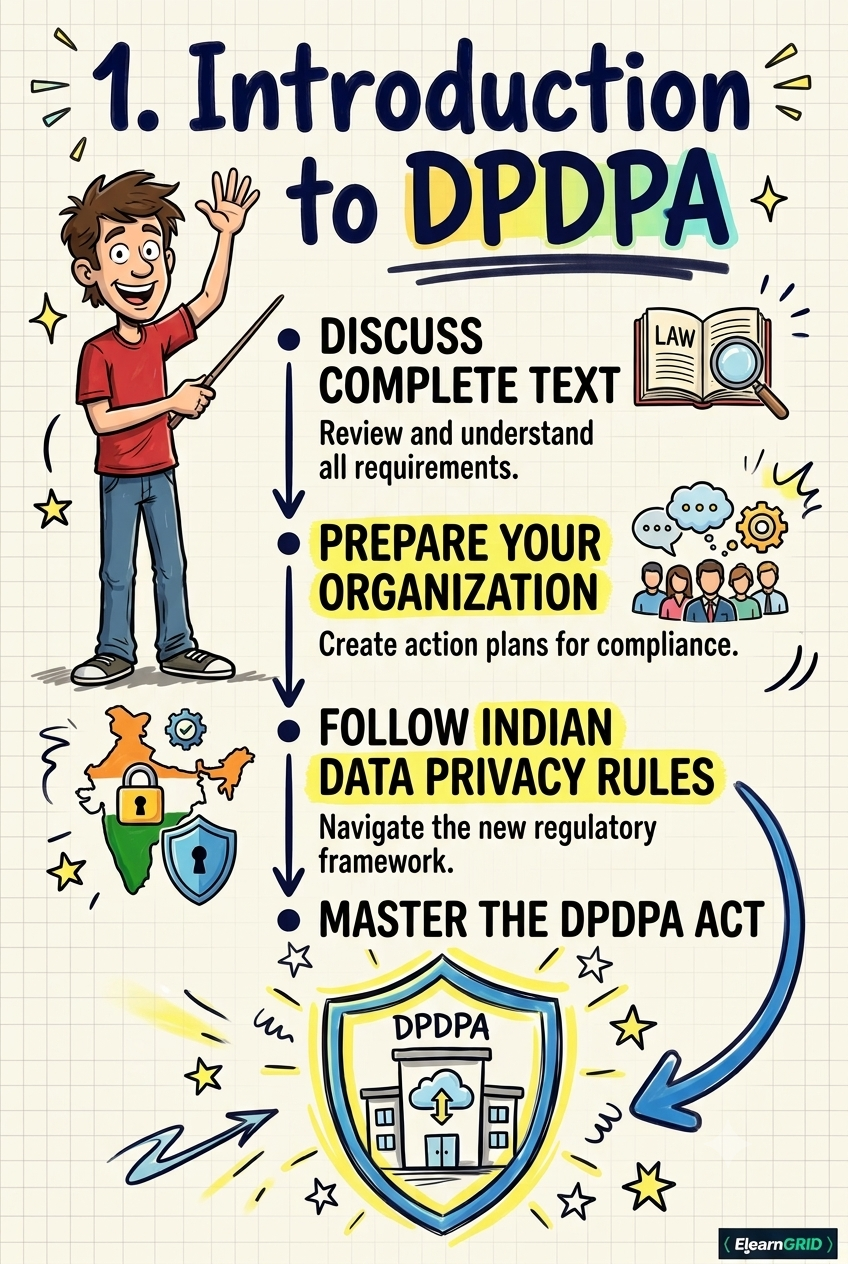
1. Introduction to DPDPA
Issue #85
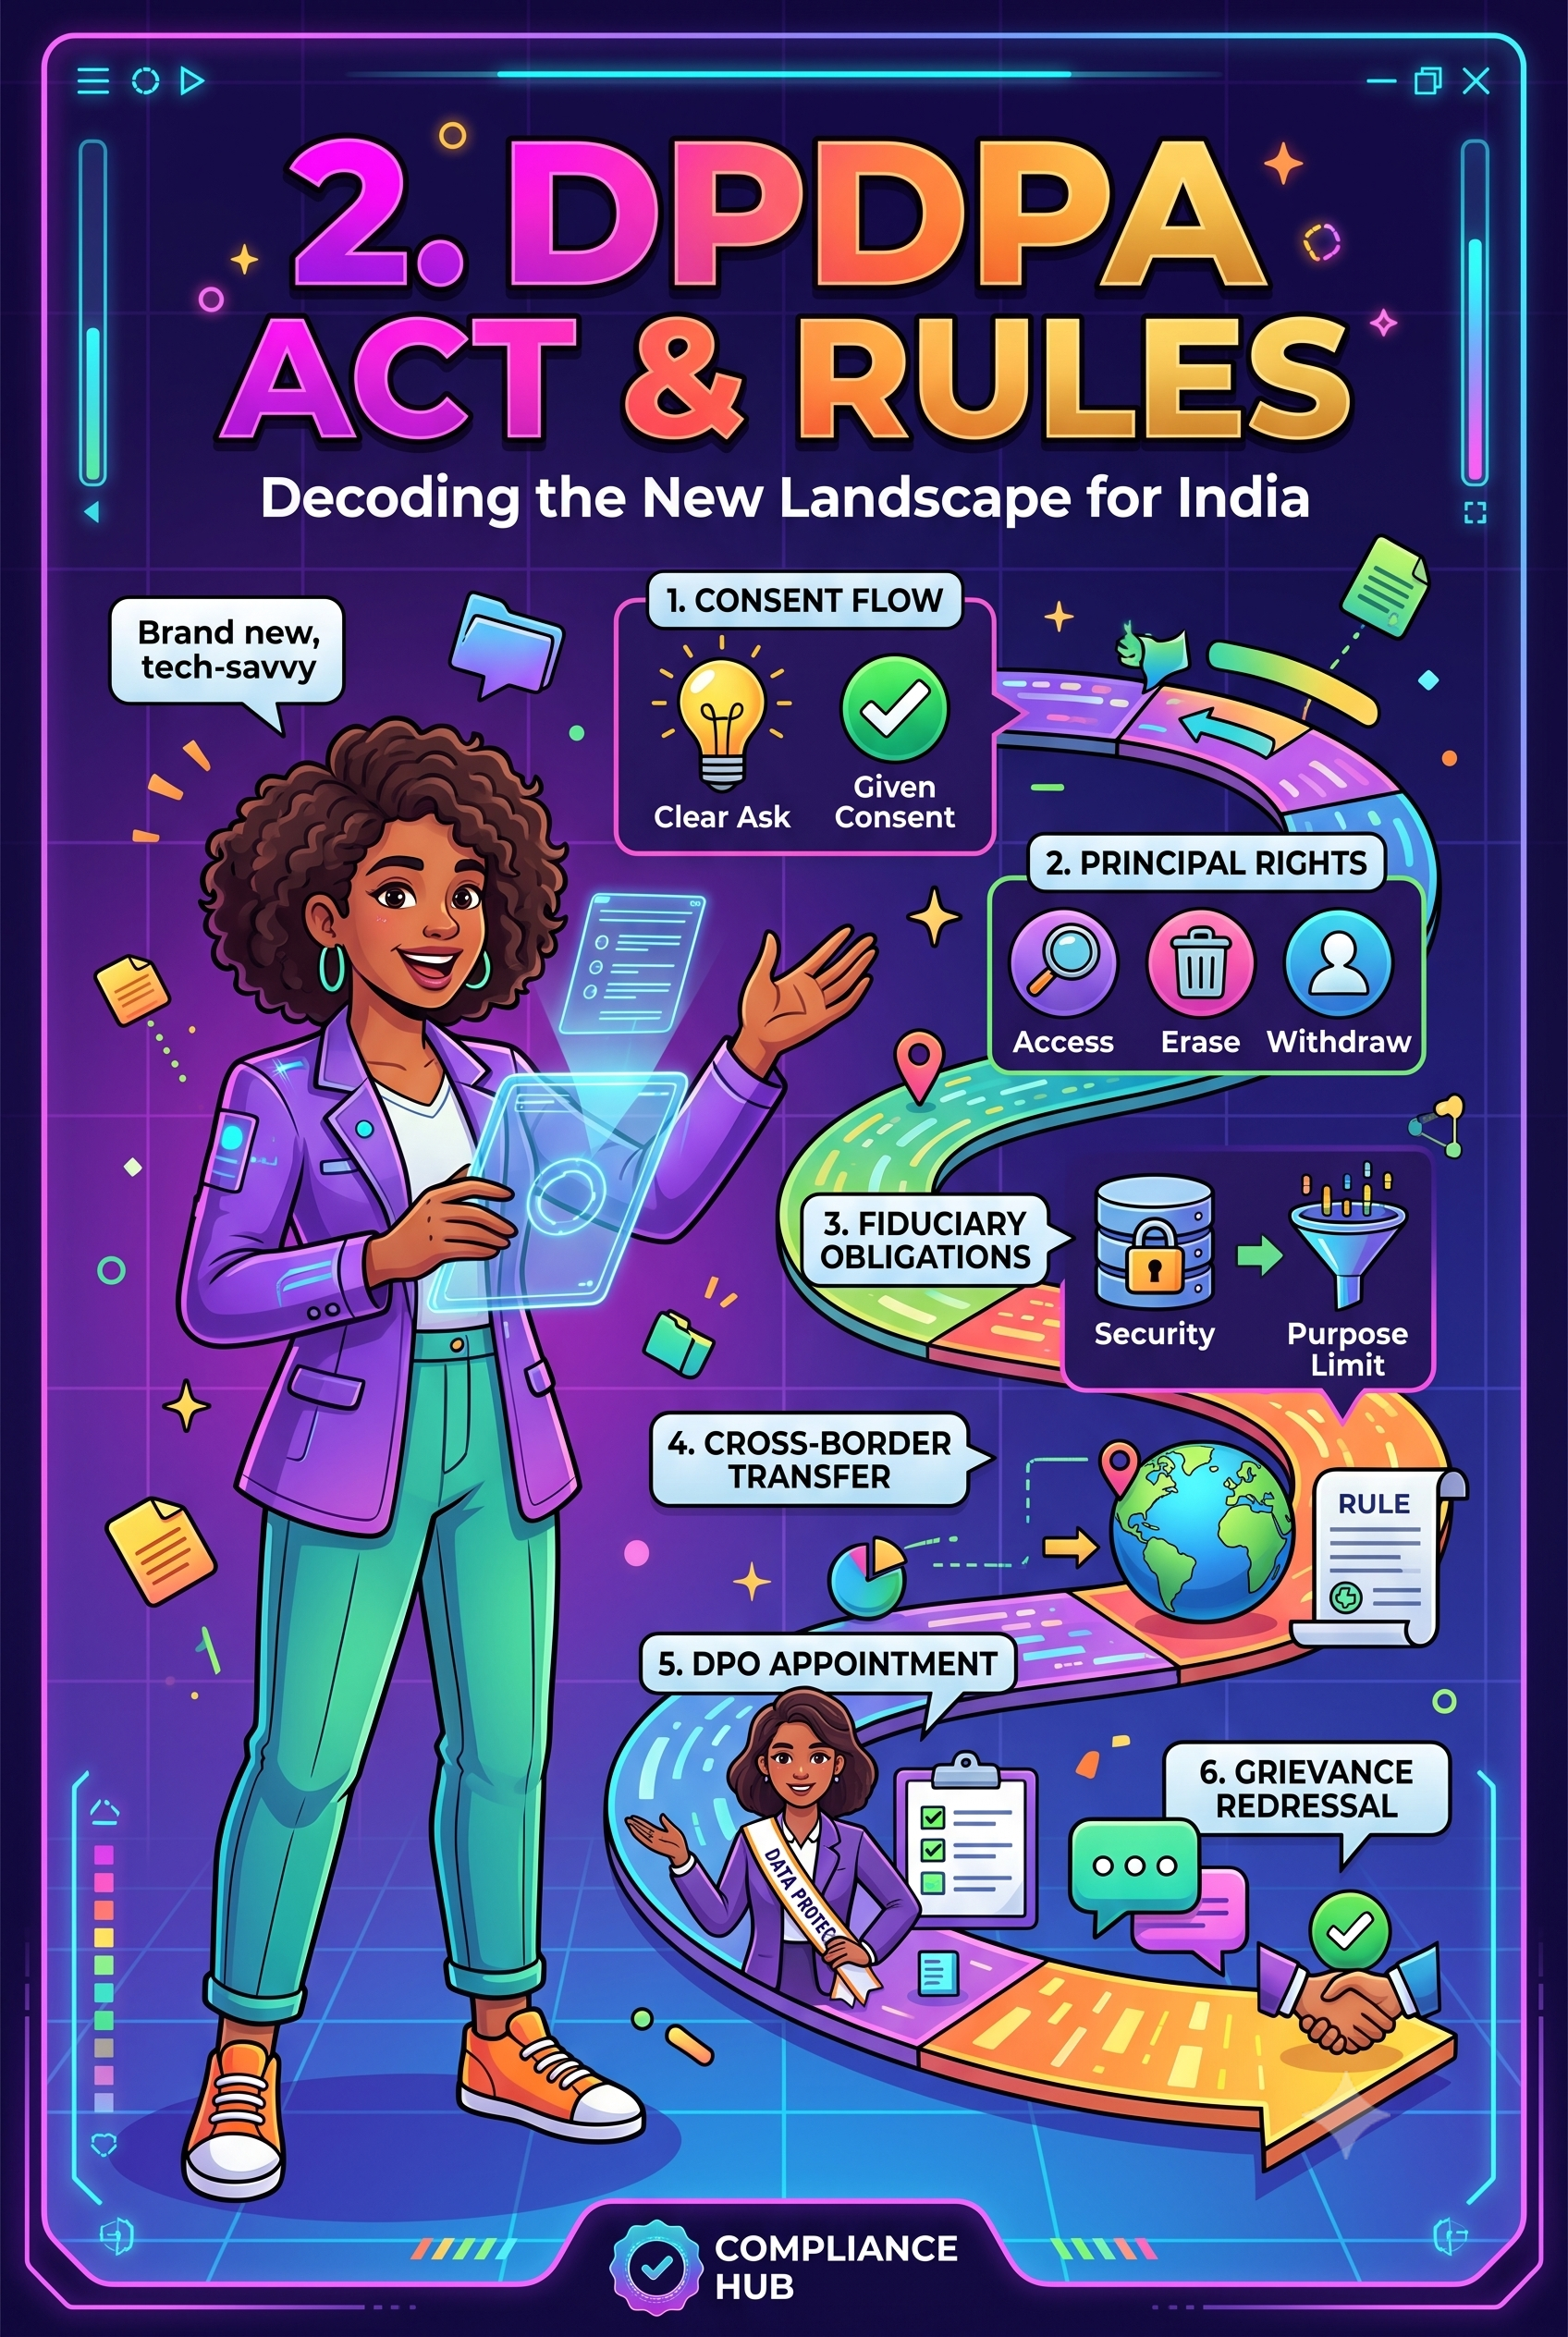
2. Part1 and Part 2
Issue #86
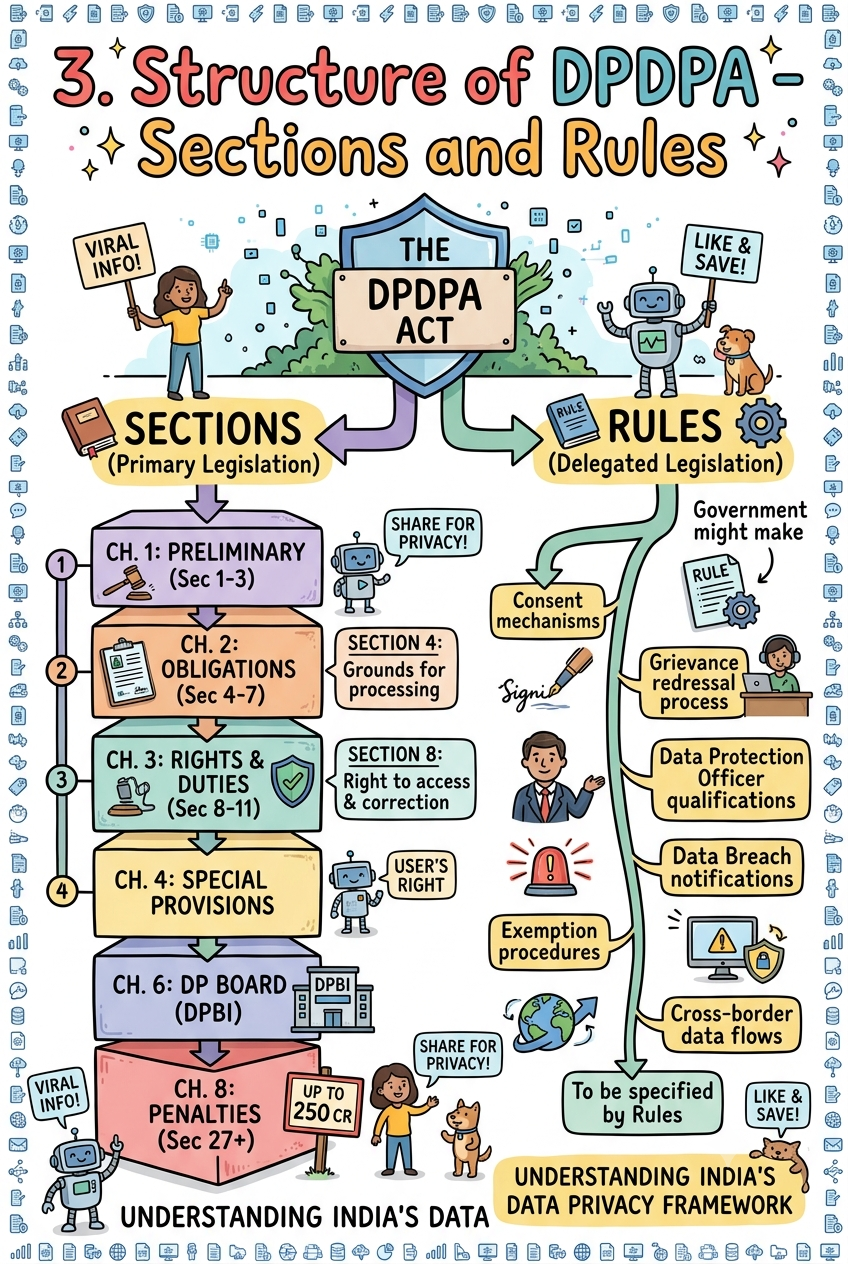
3: Structure of DPDPA - Sections and Rules
Issue #87
4. Key Terminology - The Foundation
Issue #88
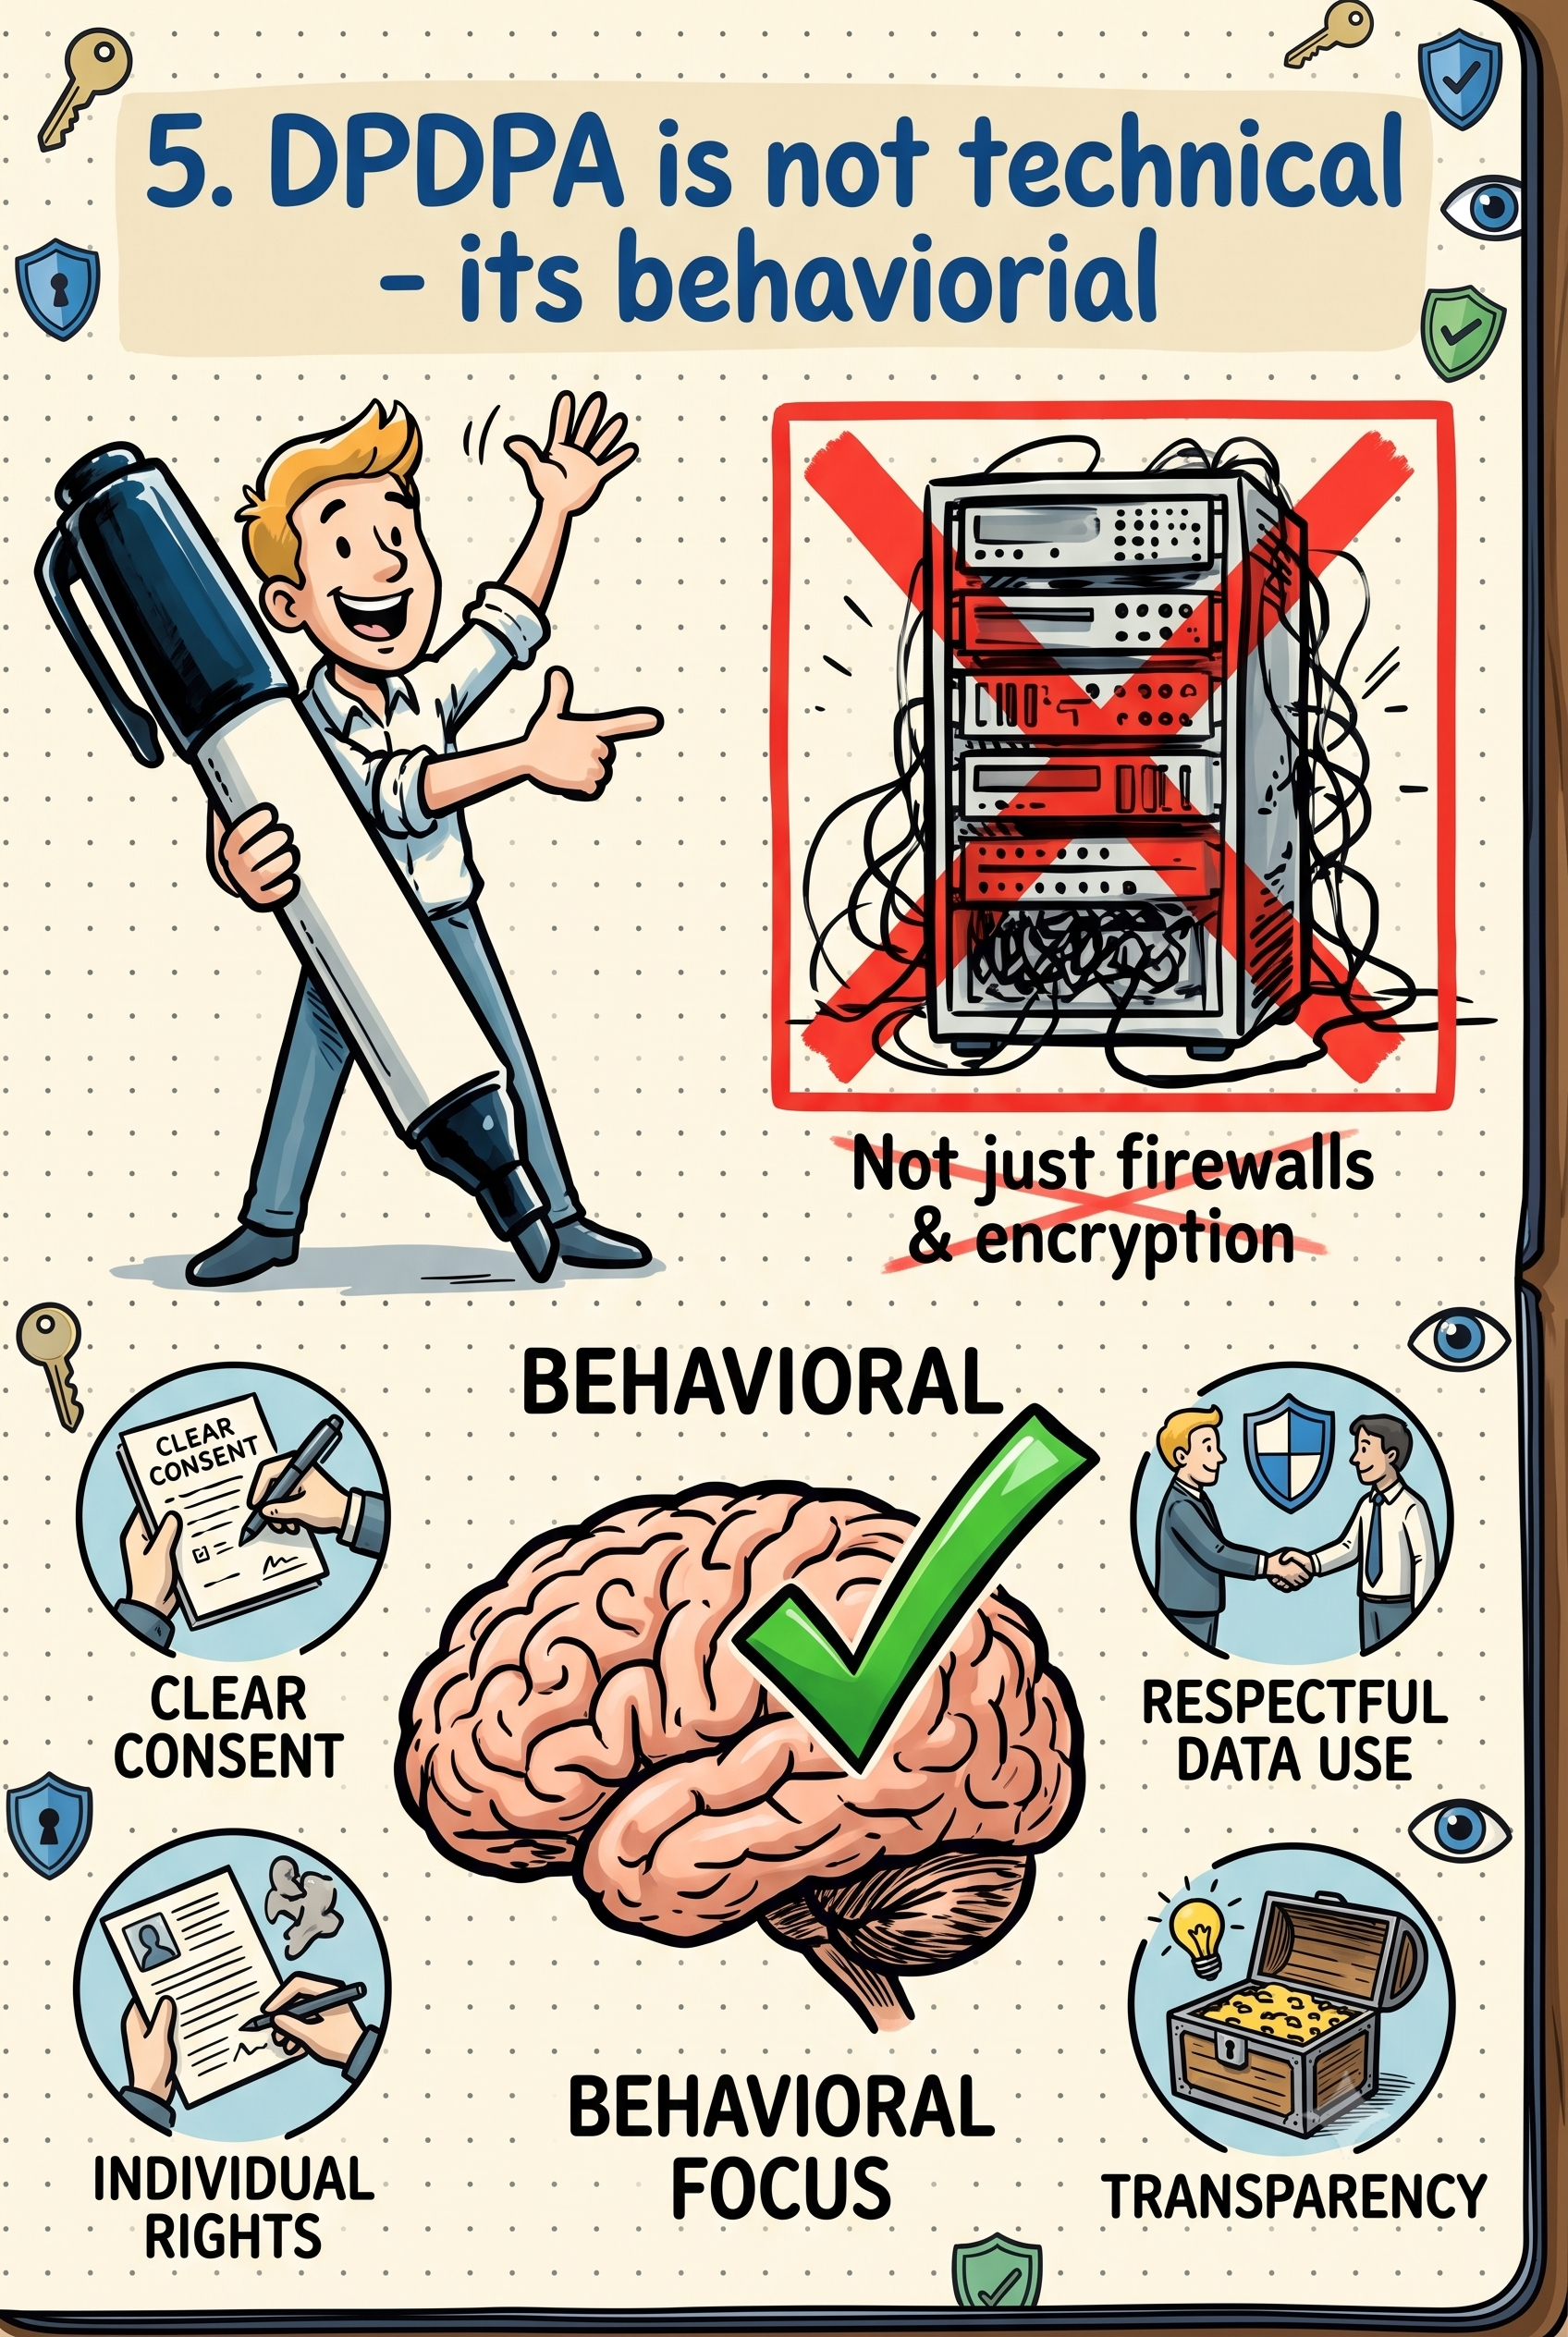
5. DPDPA is not Technical - It's Behavioral
Issue #89
6. The Ultimate Goal - Data Minimization
Issue #90
7. Five Things DPDPA Wants from You
Issue #91
8. Do I need to hire a consultant
Issue #92
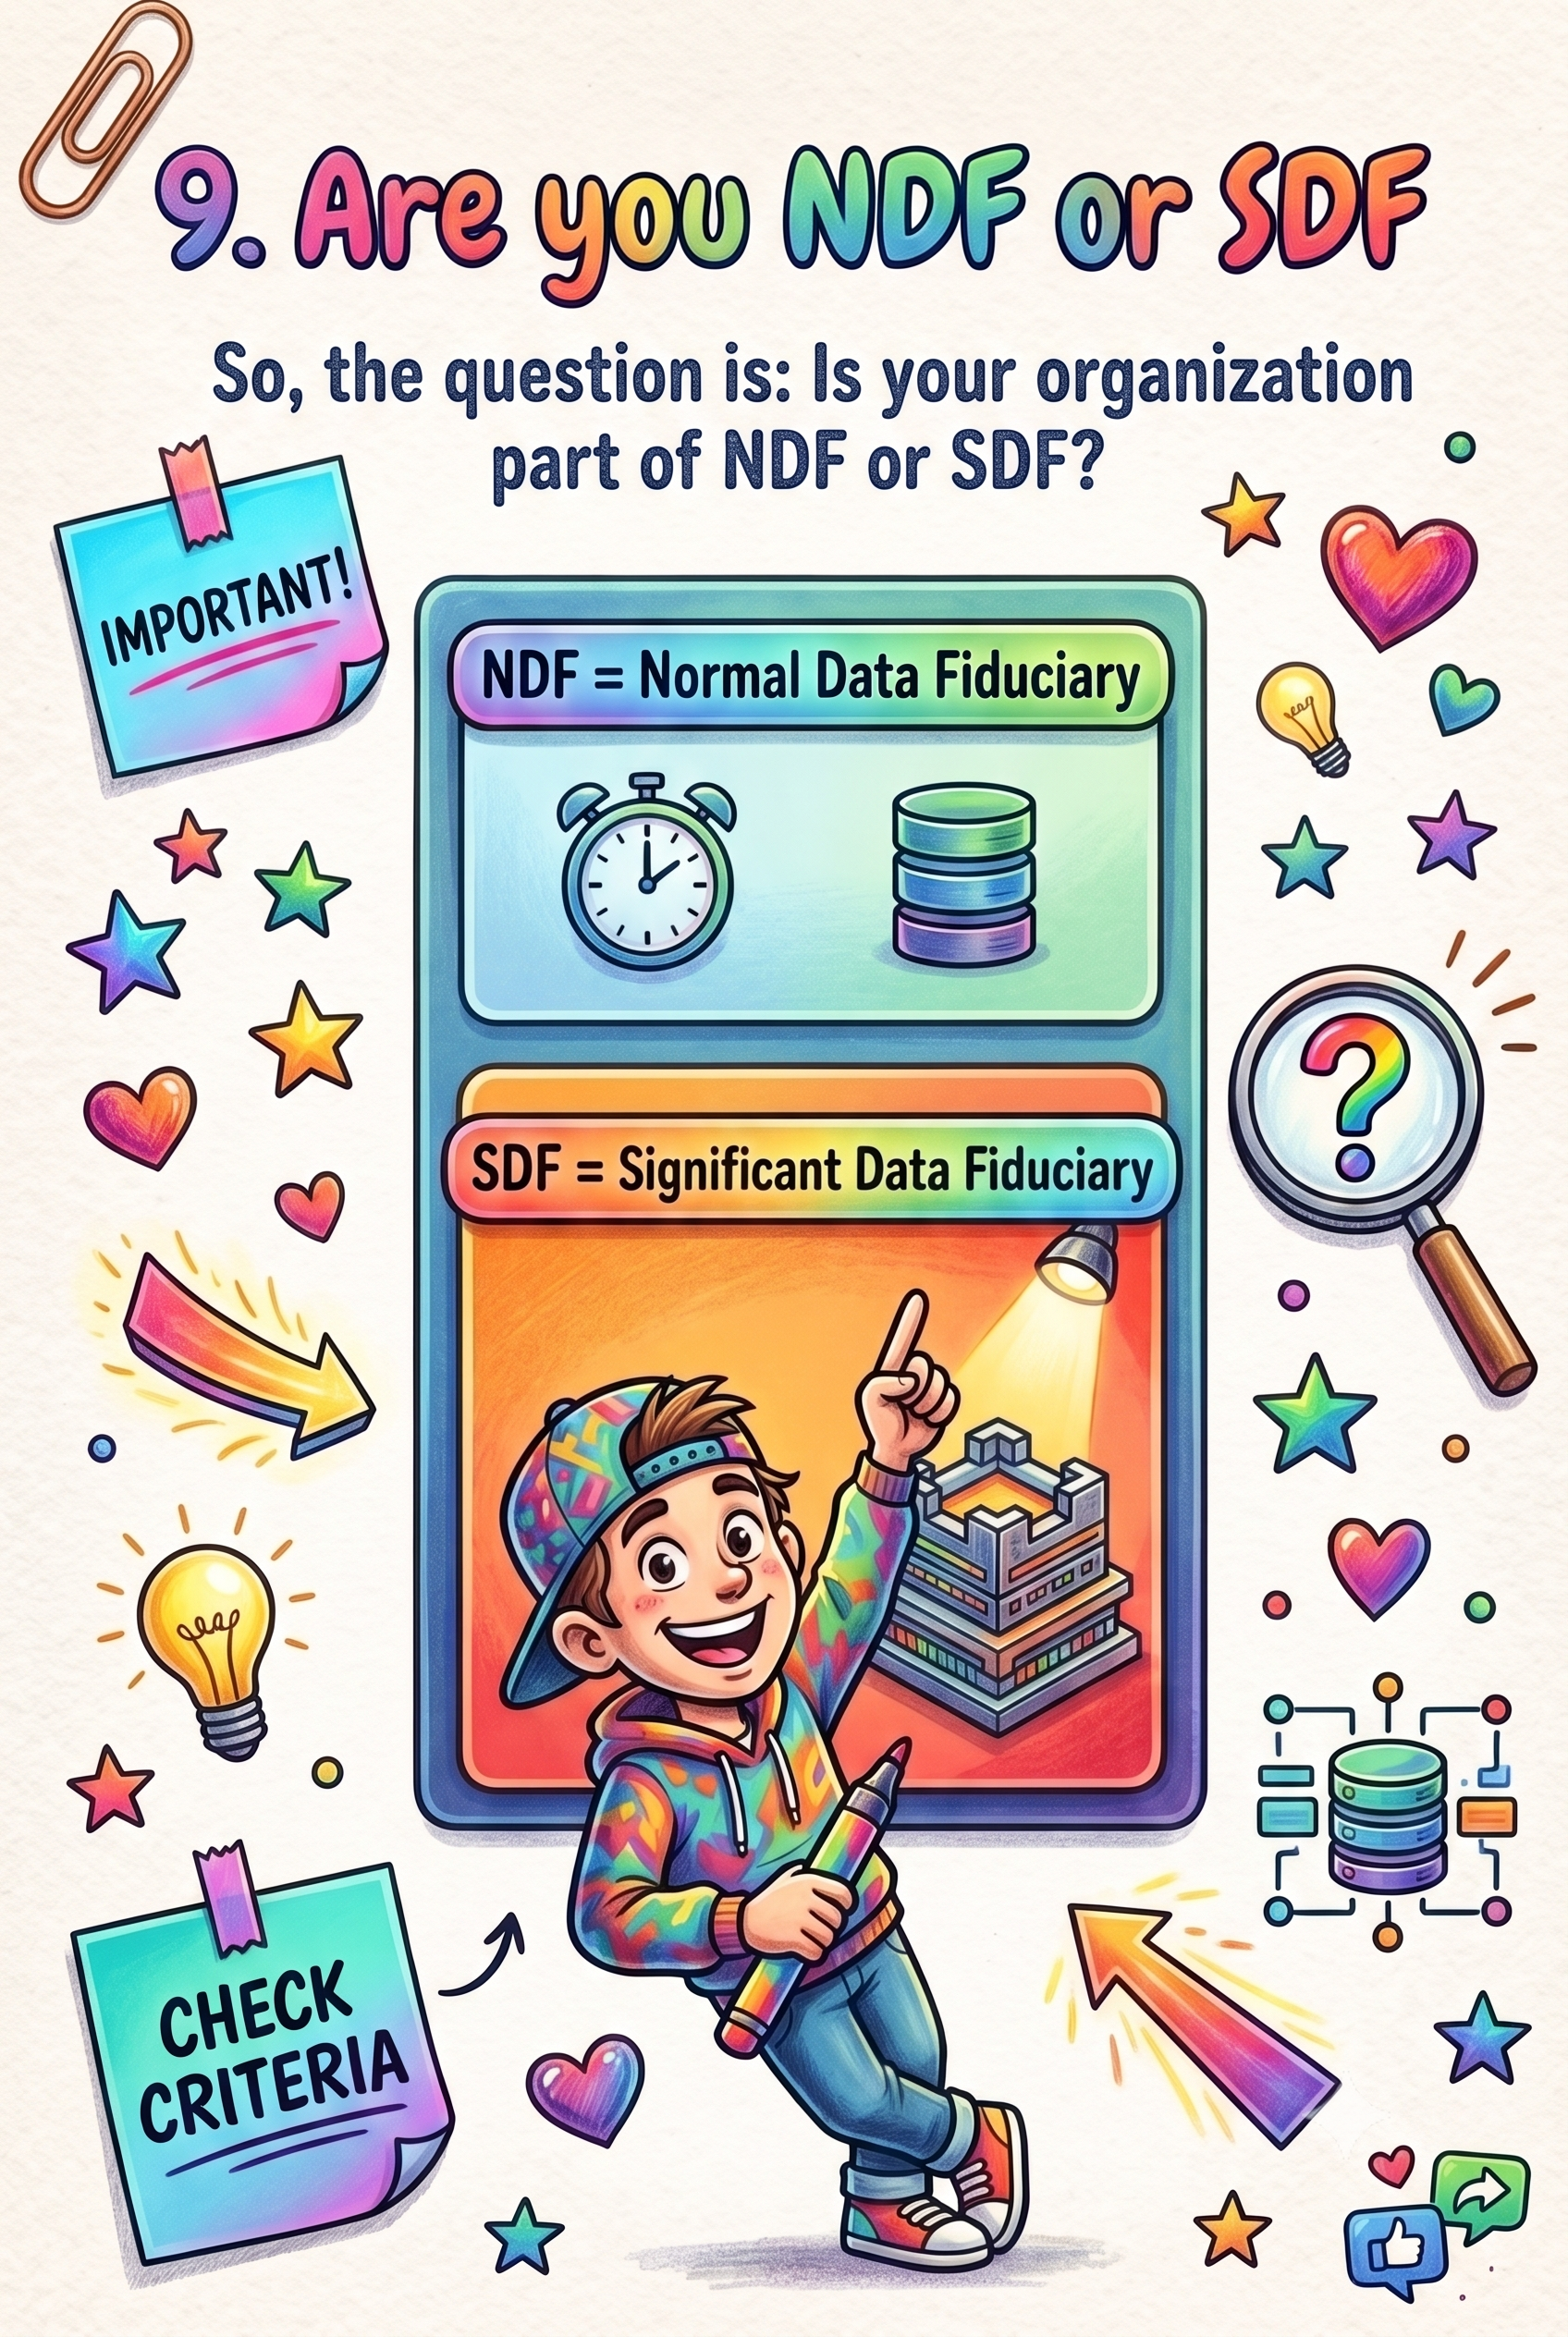
9. Are you NDF or SDF
Issue #93
10. The Three Step FIlter for SDF
Issue #94
11. Compliance Requirement for My Company
Issue #95
12. Can I Build DPDPA Compliance Without a Consultant
Issue #96
13. What Data Do You Need Before Starting
Issue #97
14. The 13-Step Compliance Process and STEP 1
Issue #98
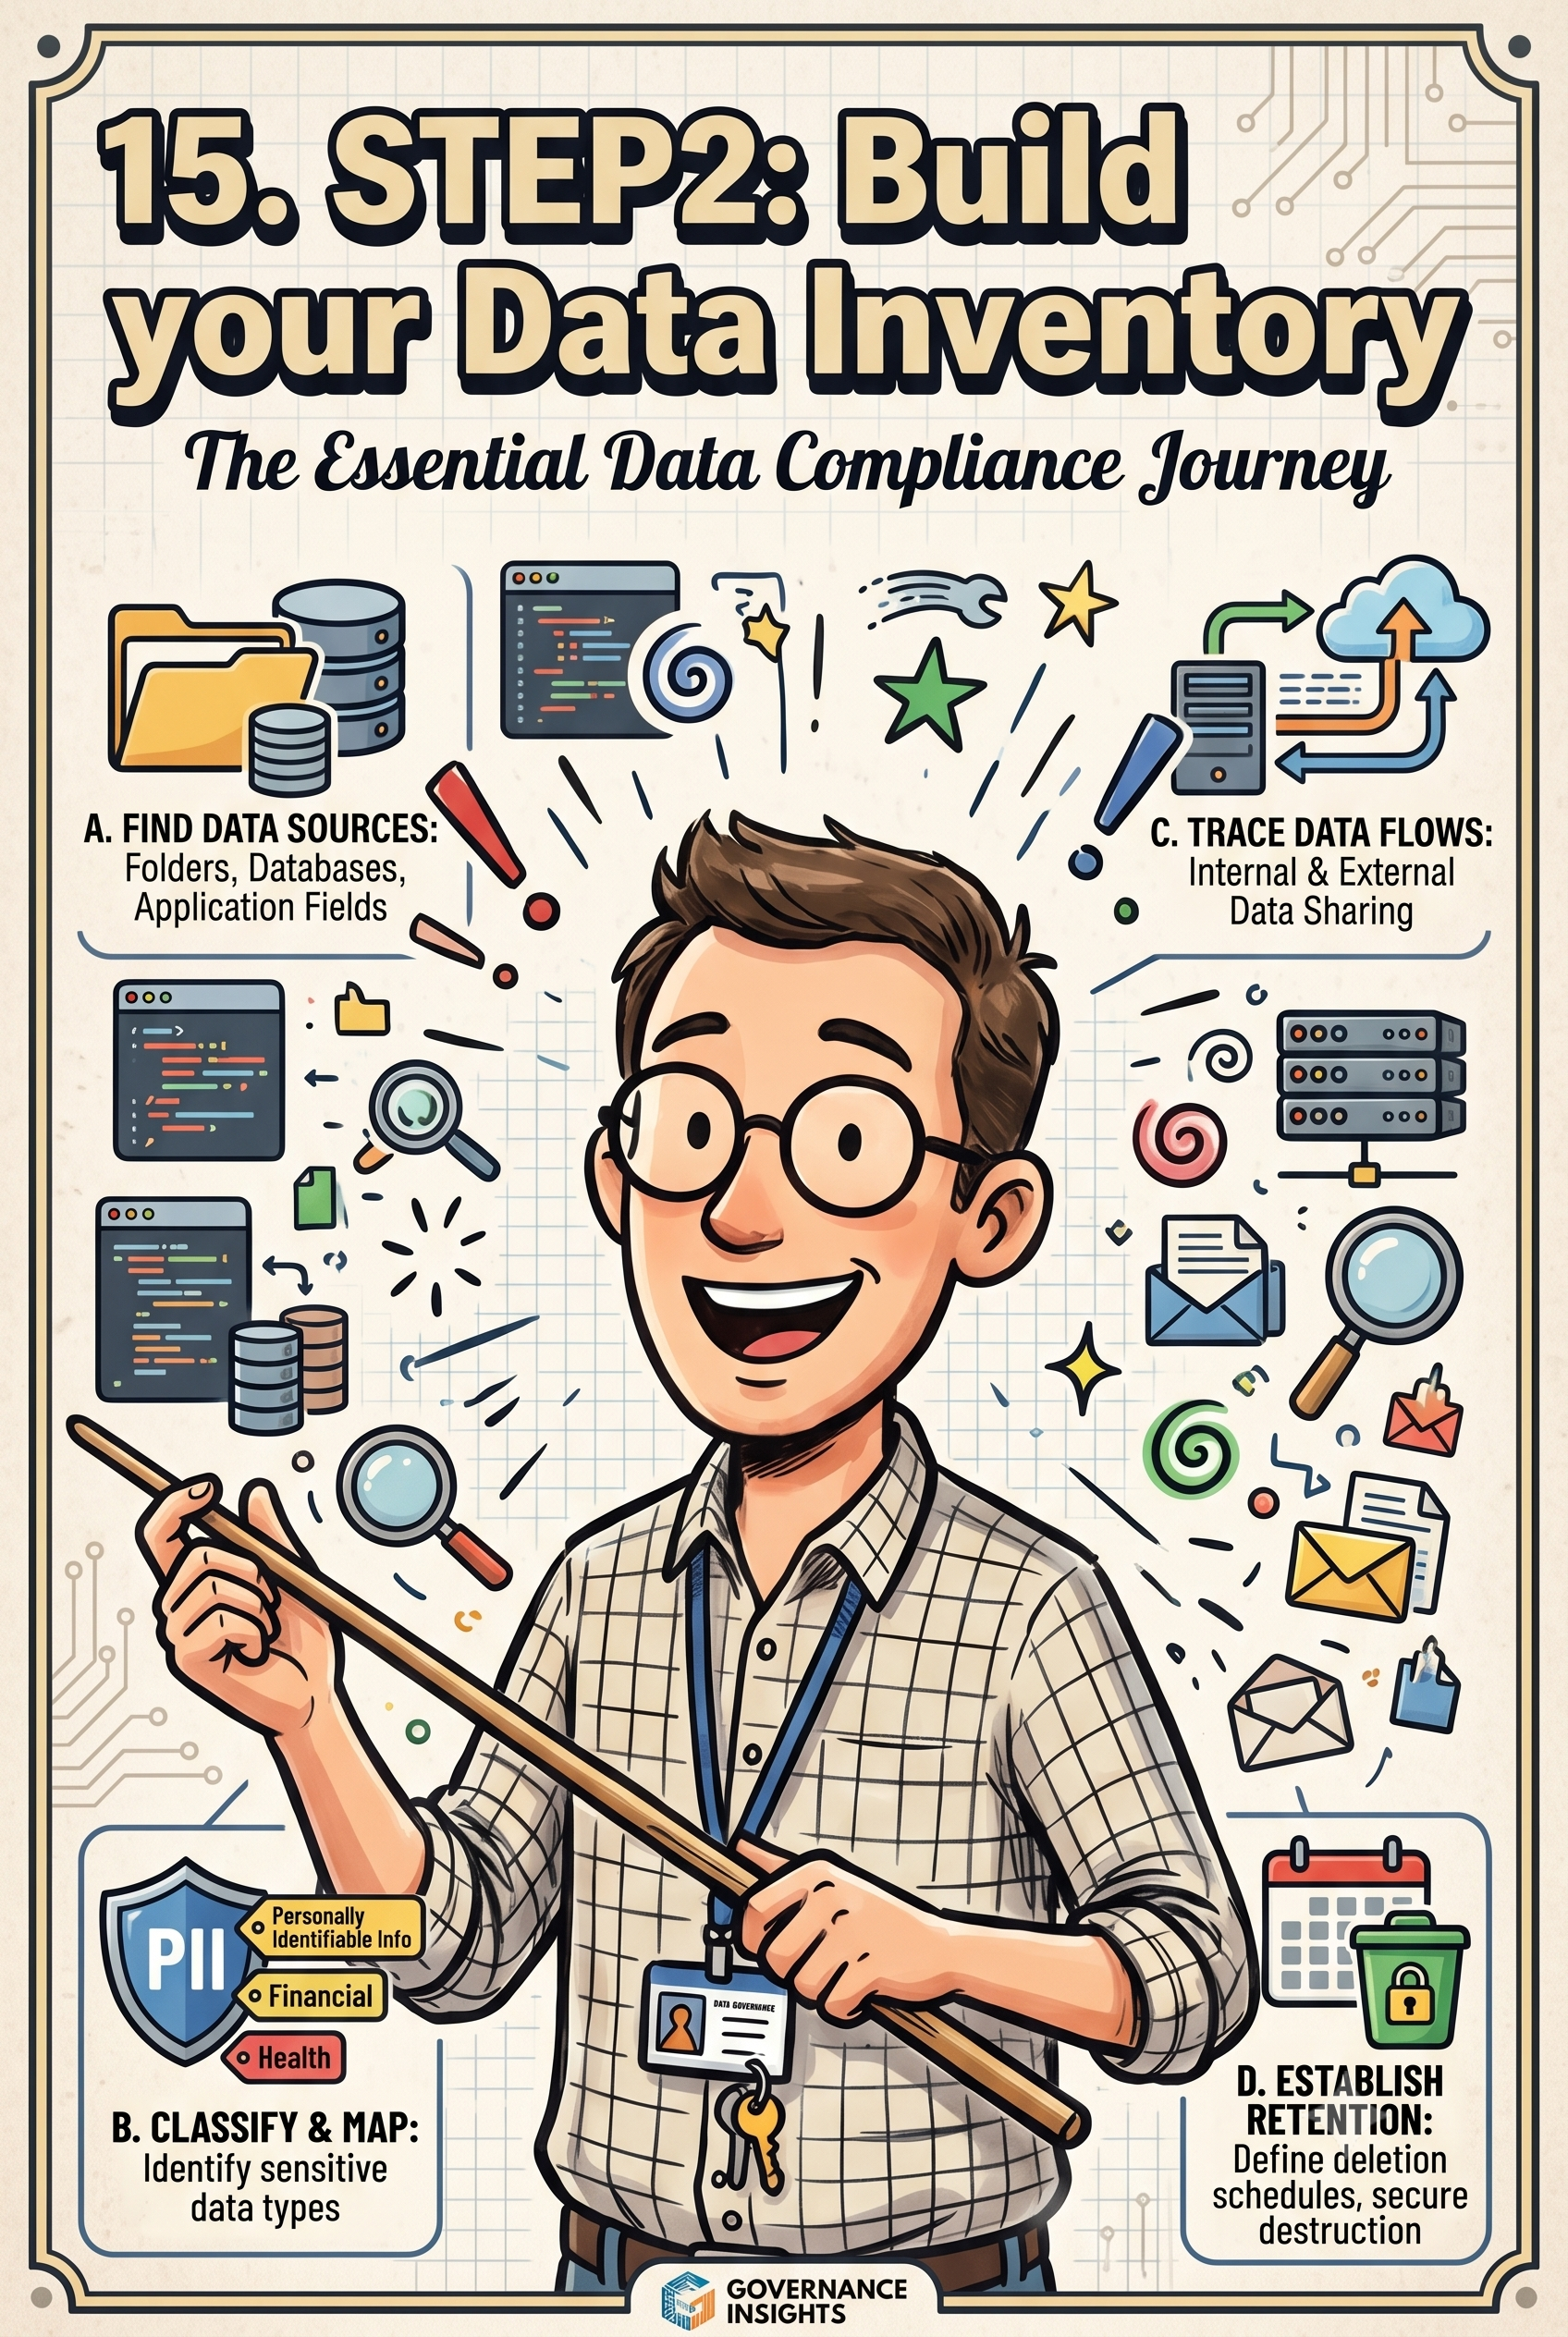
15. STEP 2 - Build Your Data Inventory
Issue #99
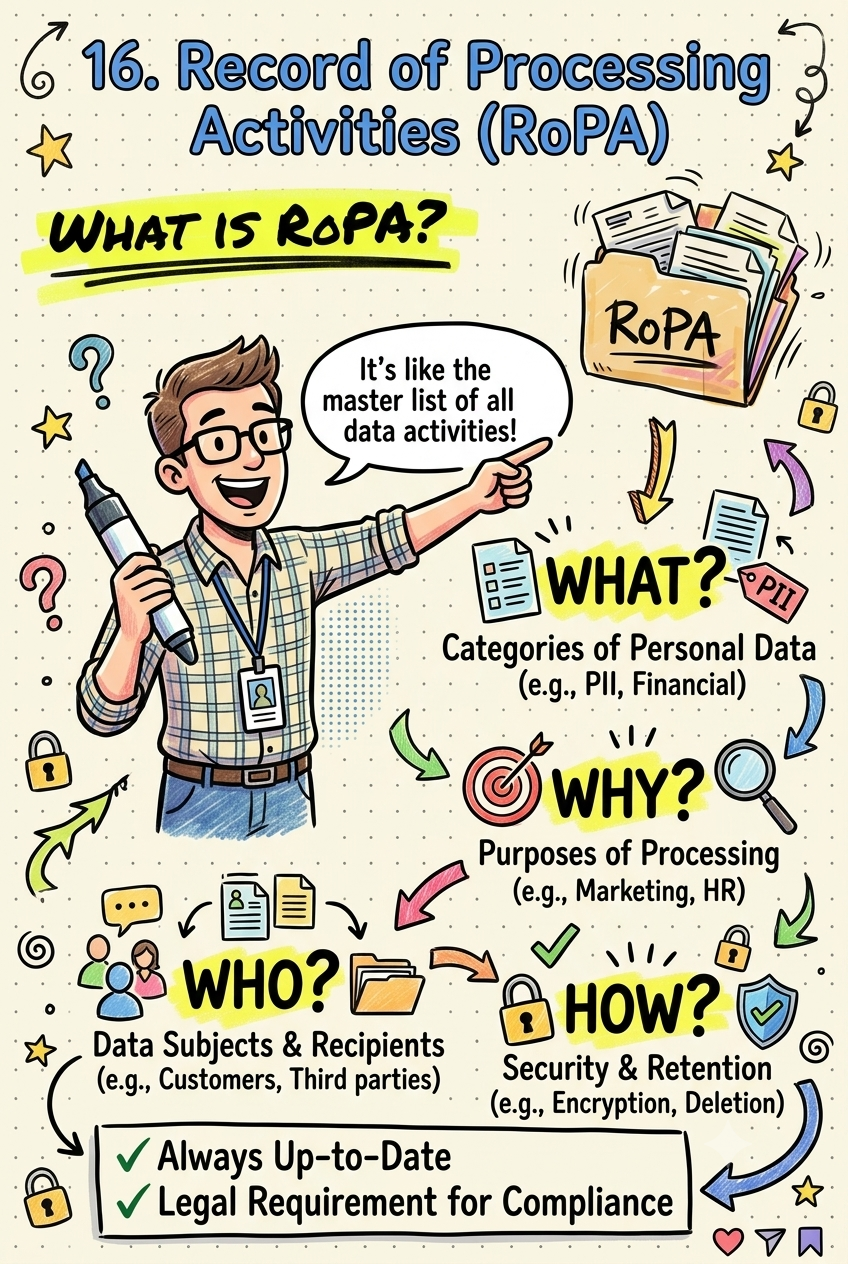
16. Record of Processing Activites
Issue #100
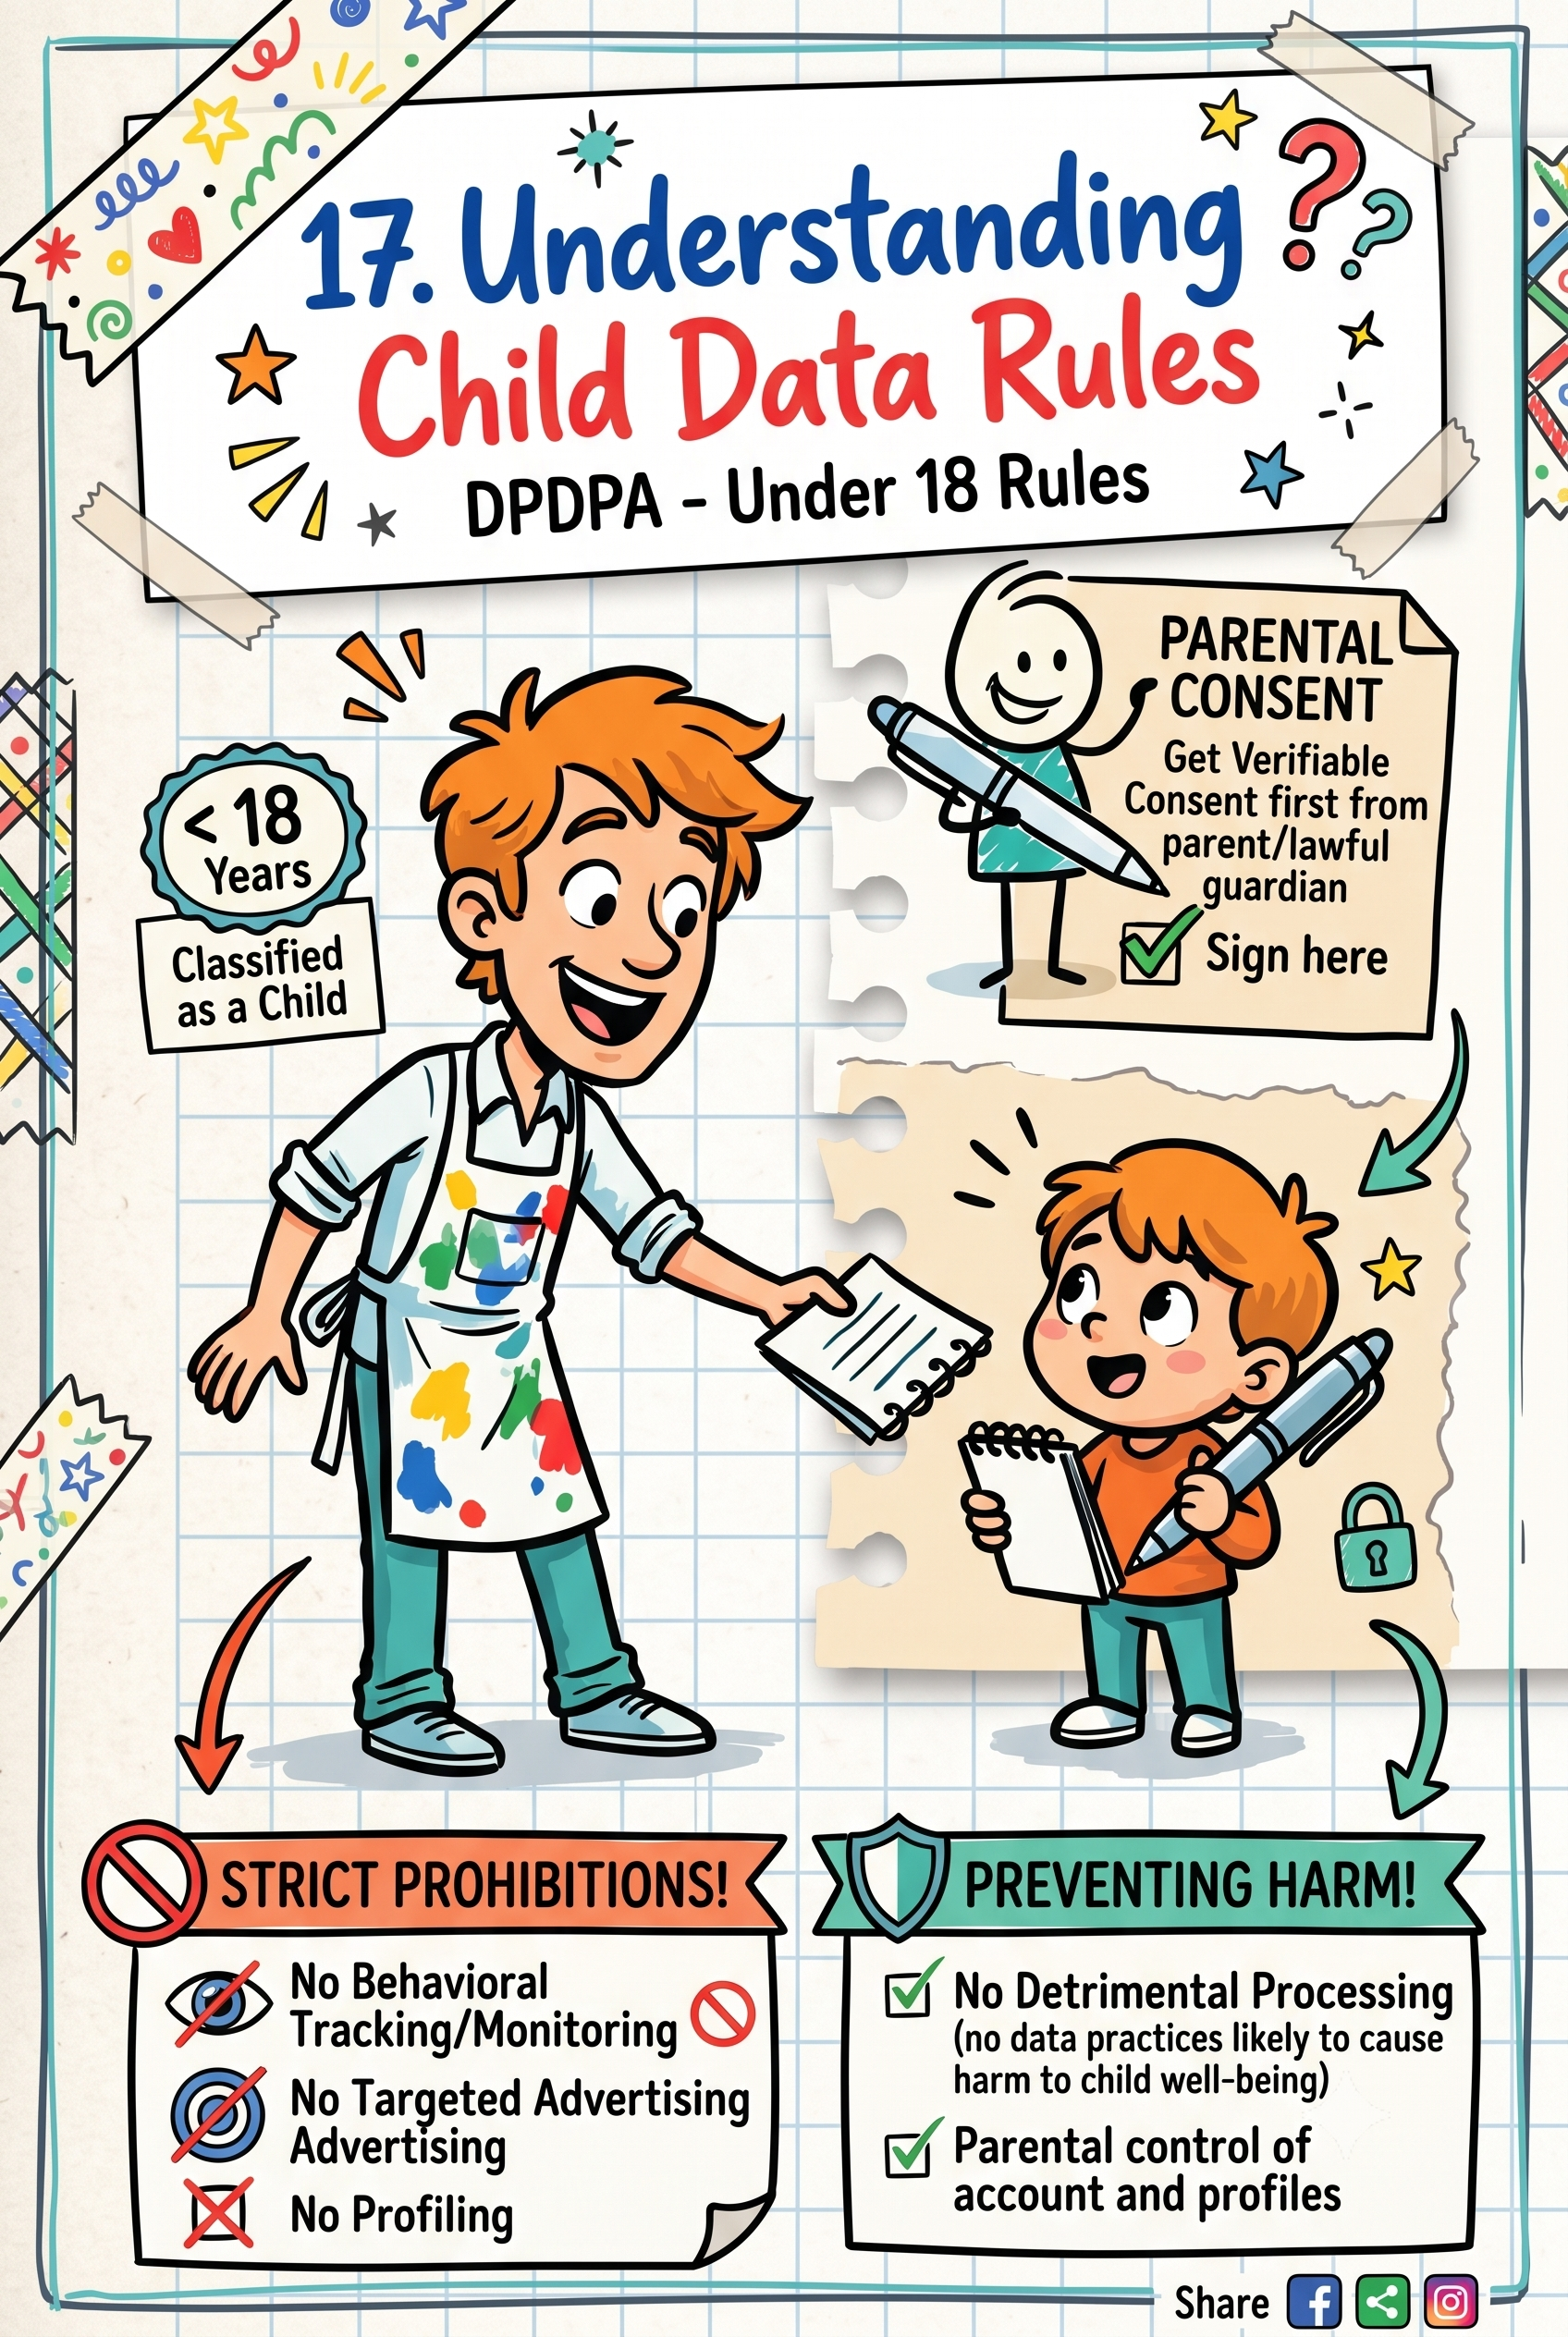
17. Understanding Child Data Rules
Issue #101
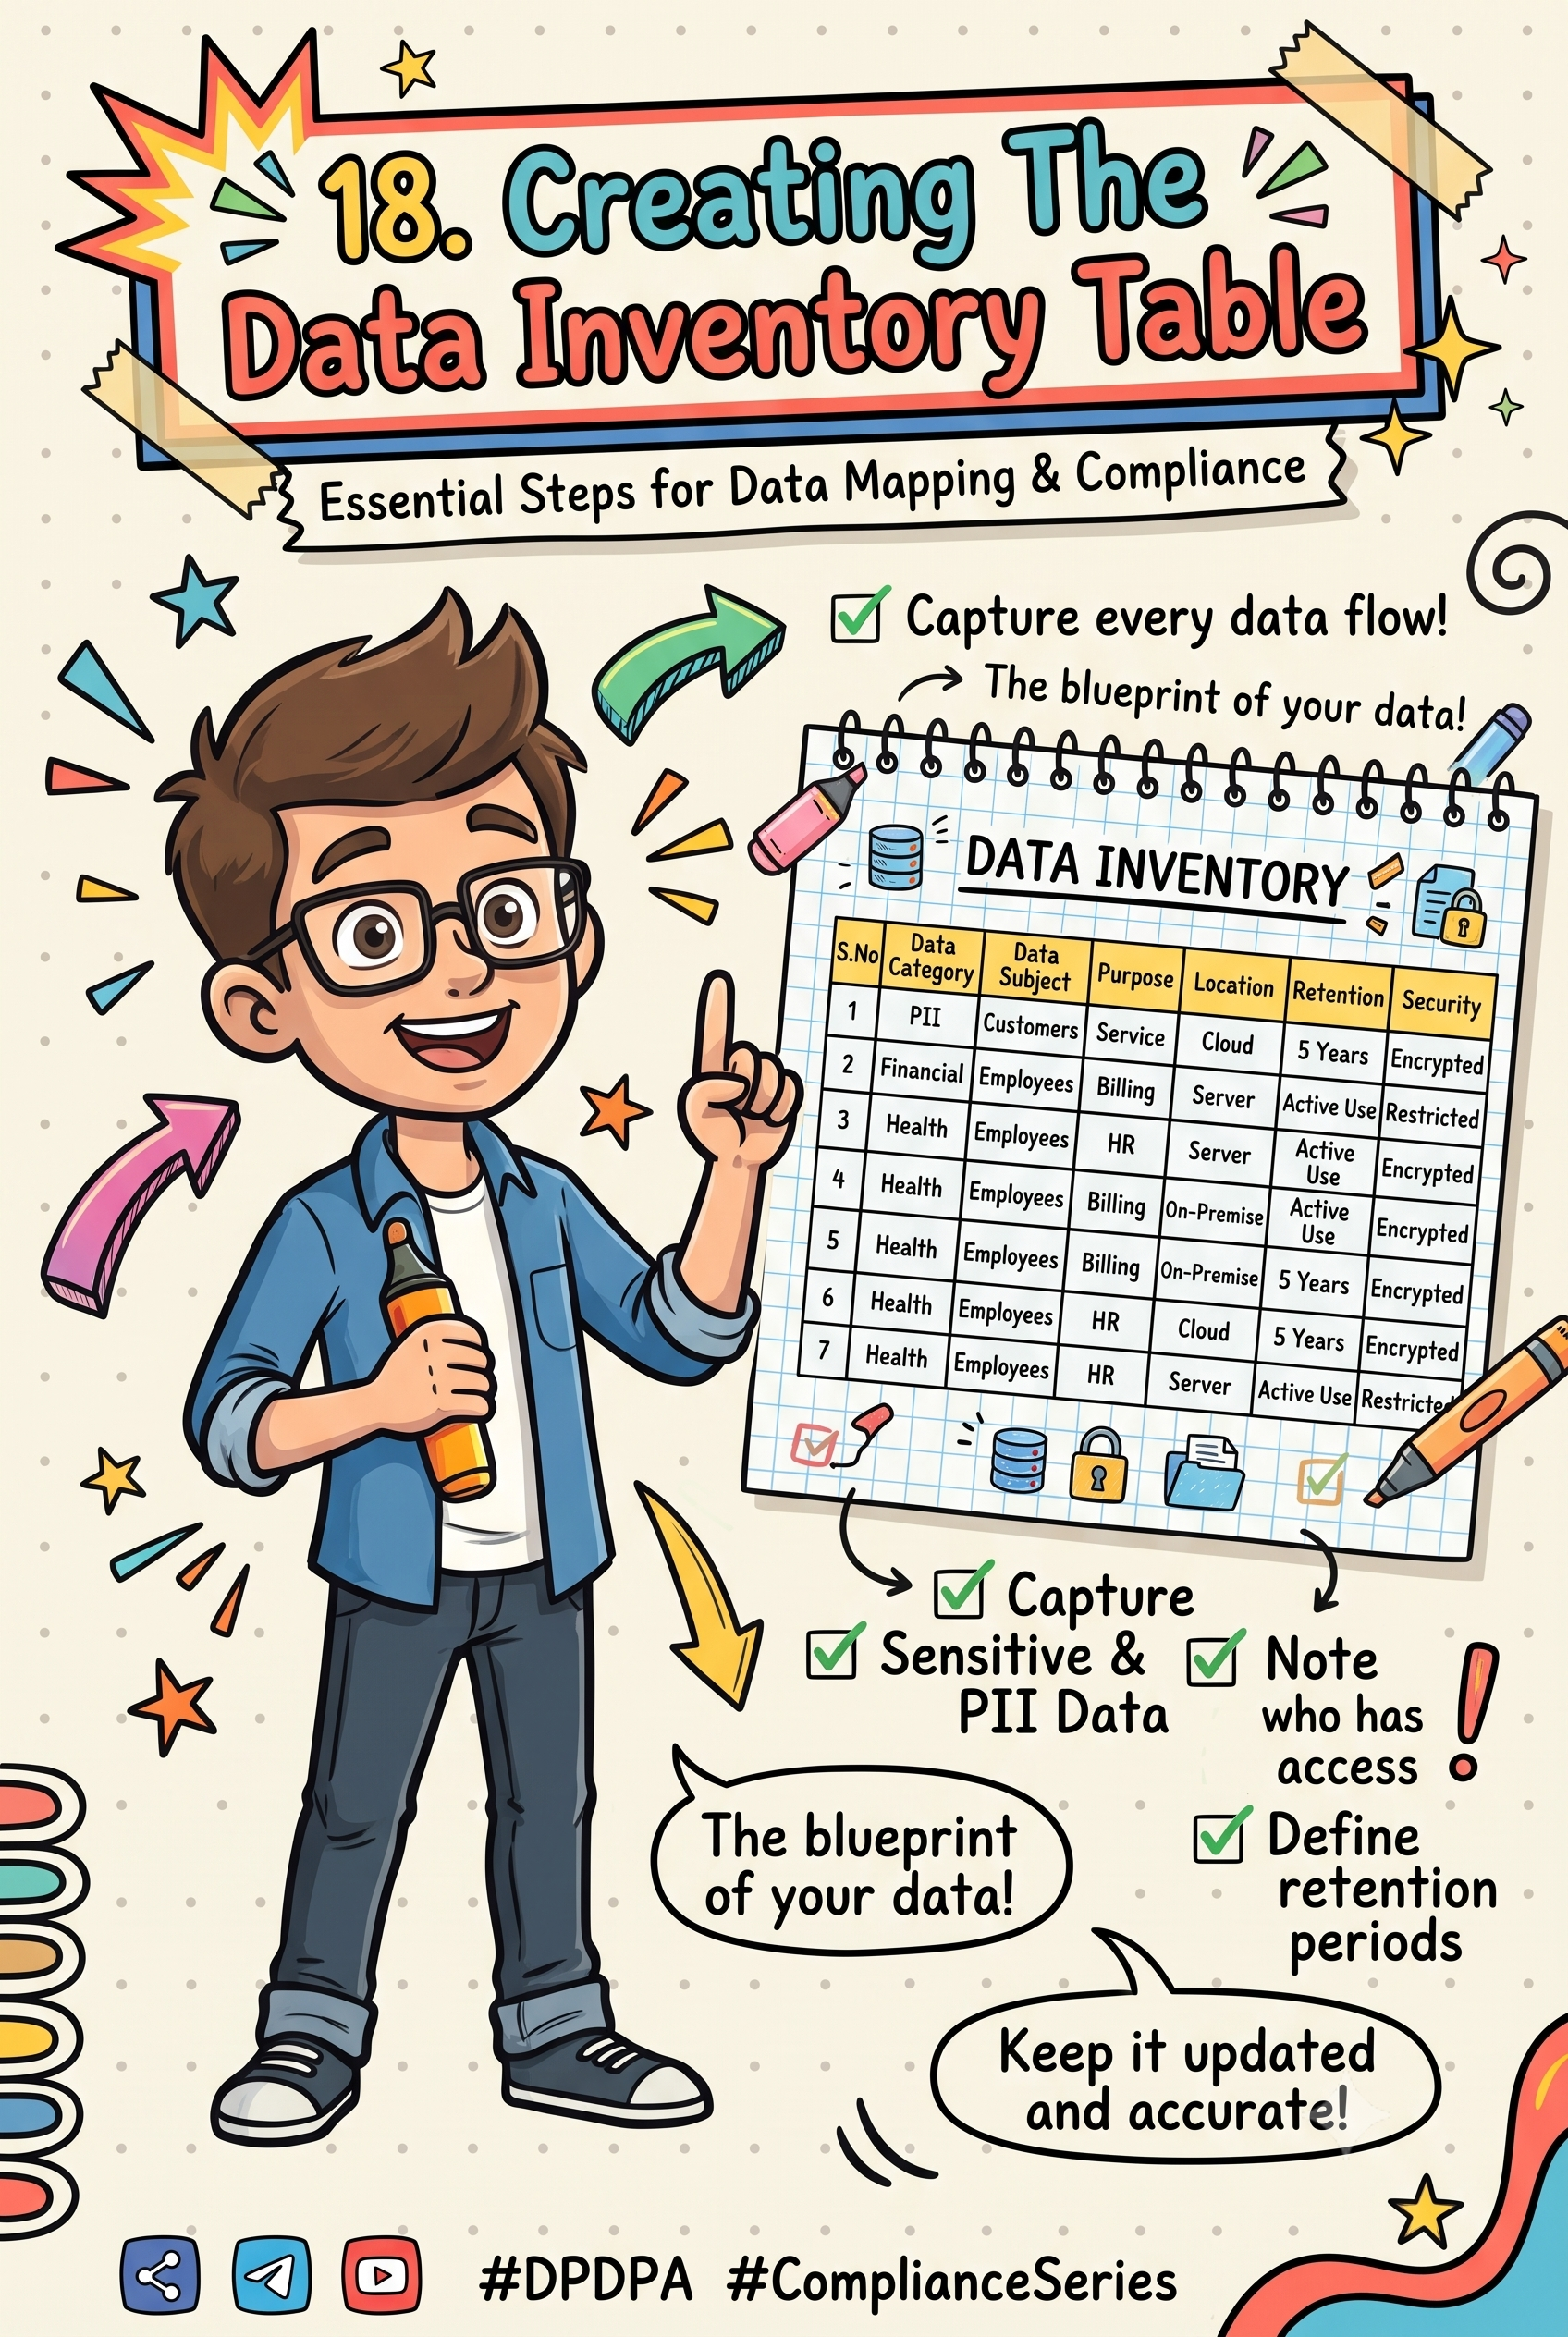
18. Creating The Data Inventory Table
Issue #102
19. Important Clauses in the Second Schedule
Issue #103
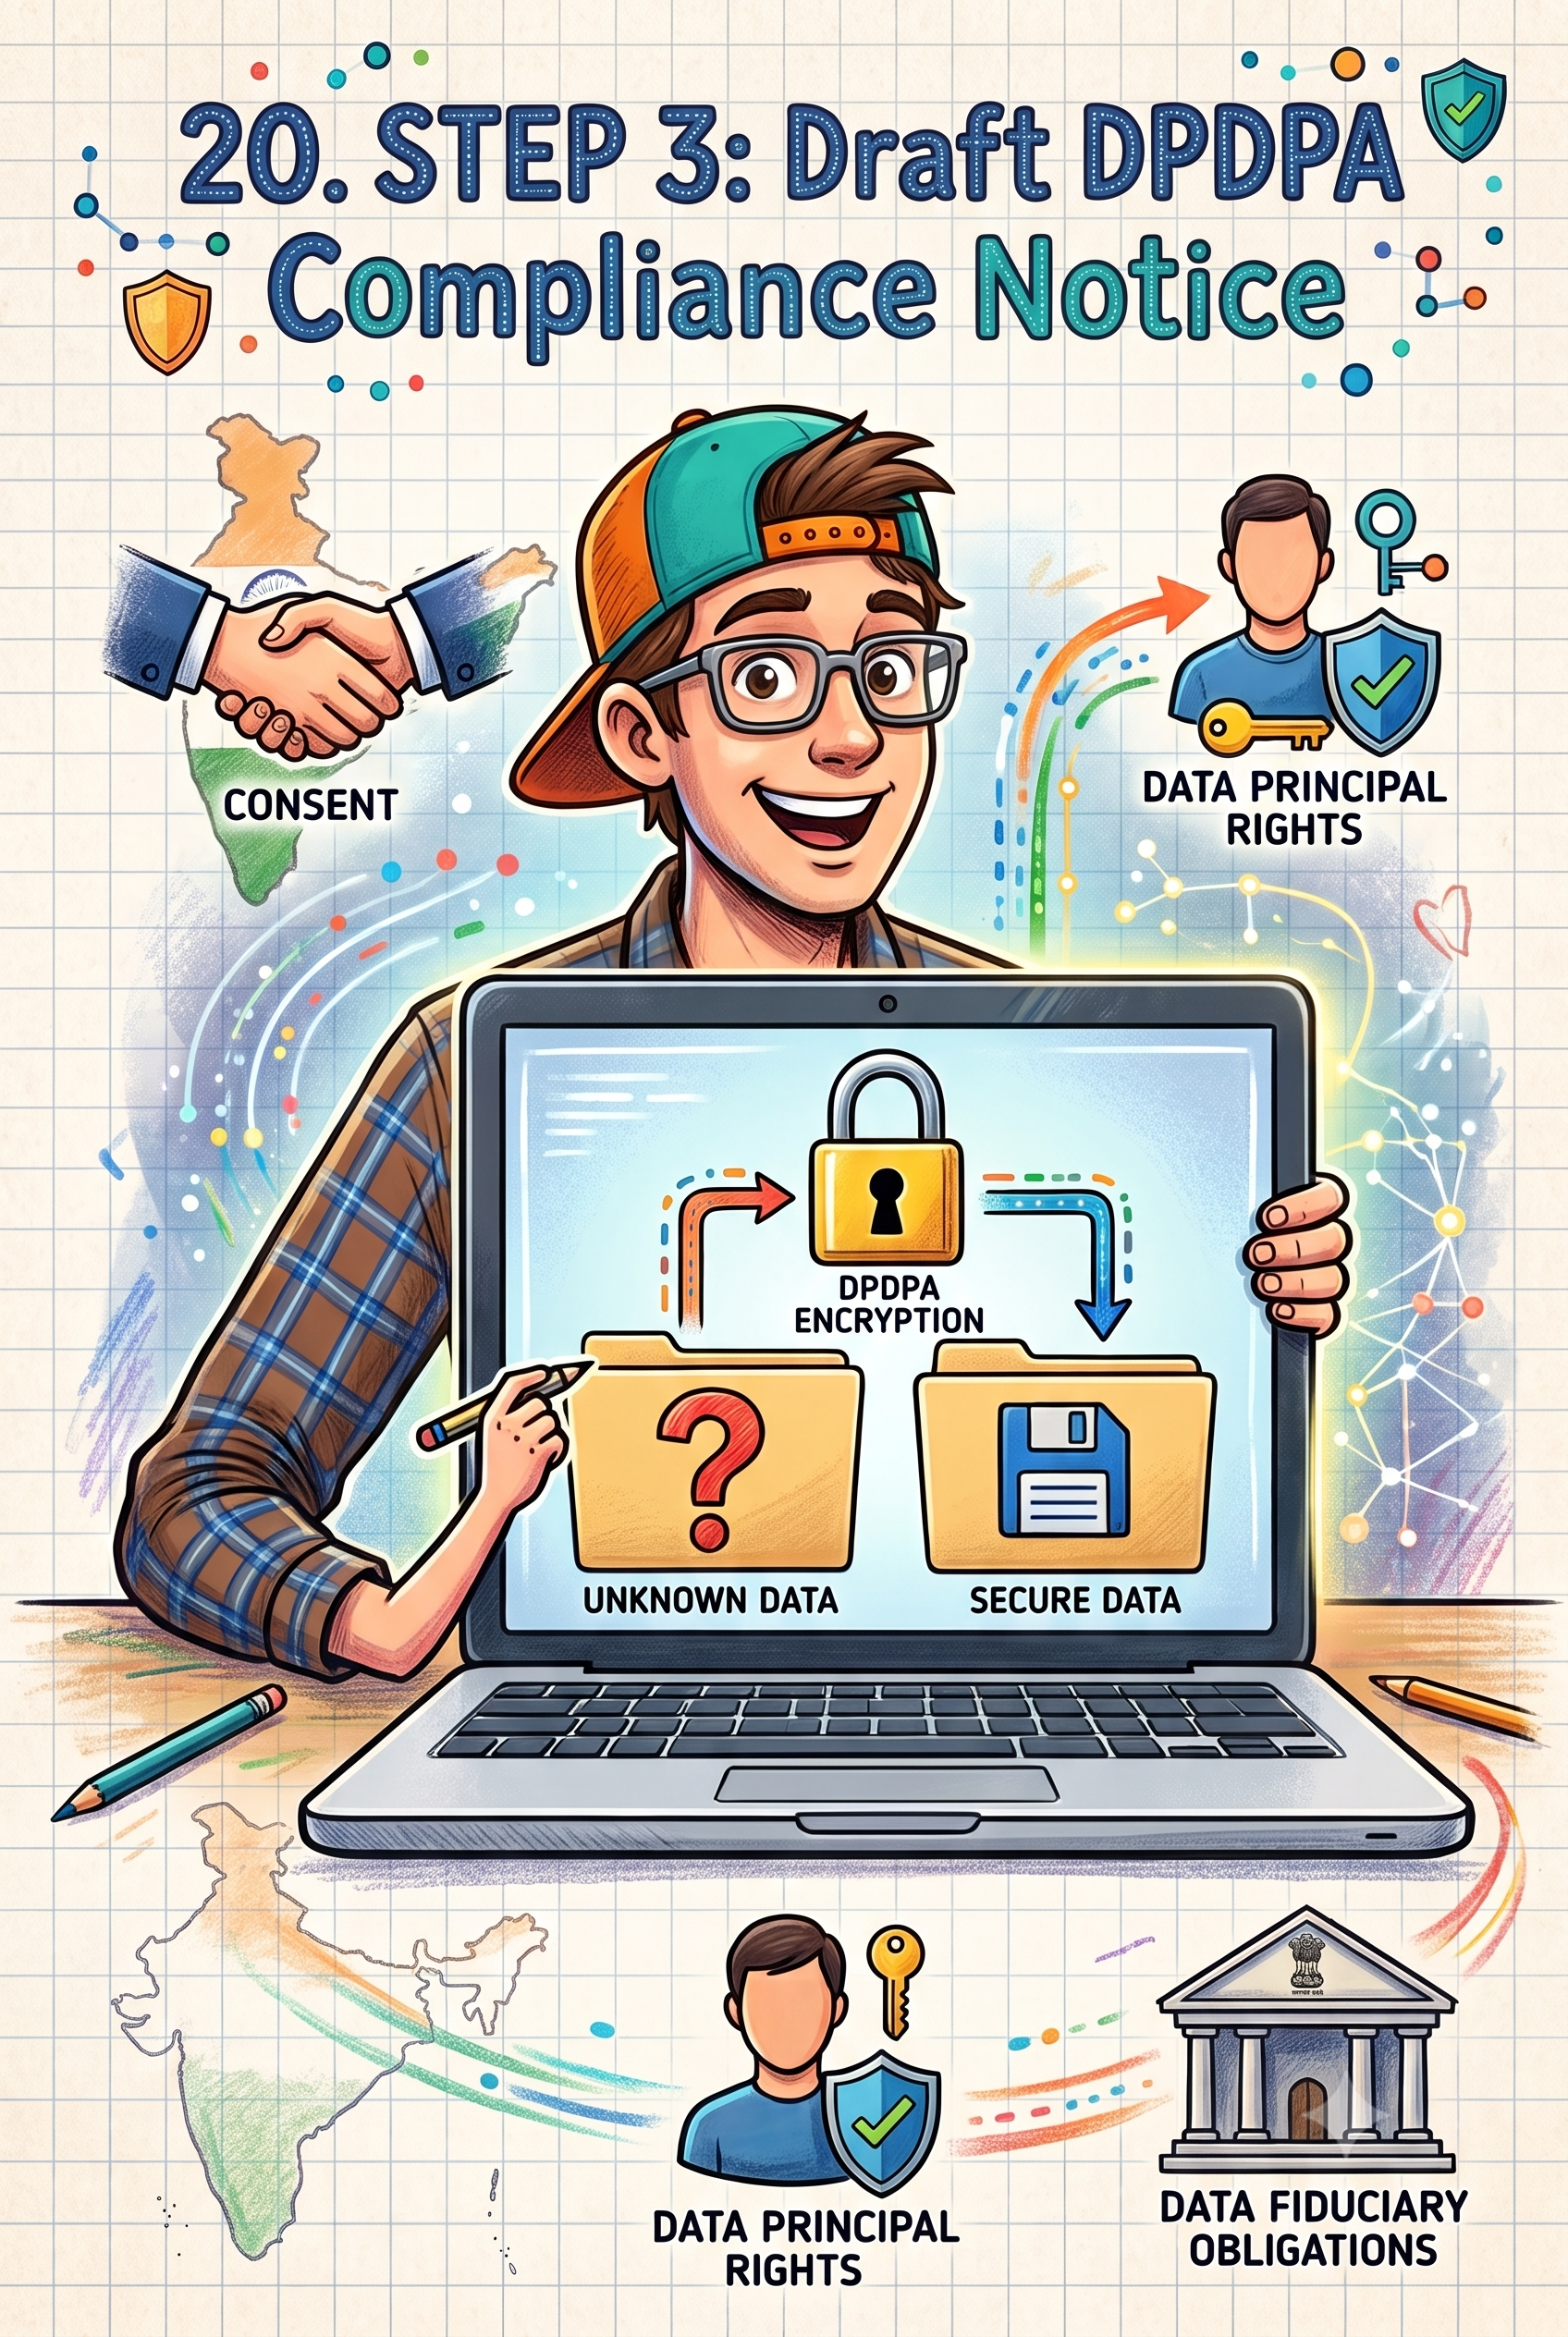
20. STEP 3: Draft DPDPA Compliance Notice
Issue #104
21. STEP4 :Map Legal Grounds Consent vs Legal Notice
Issue #105
22. STEP5: Notice and Consent
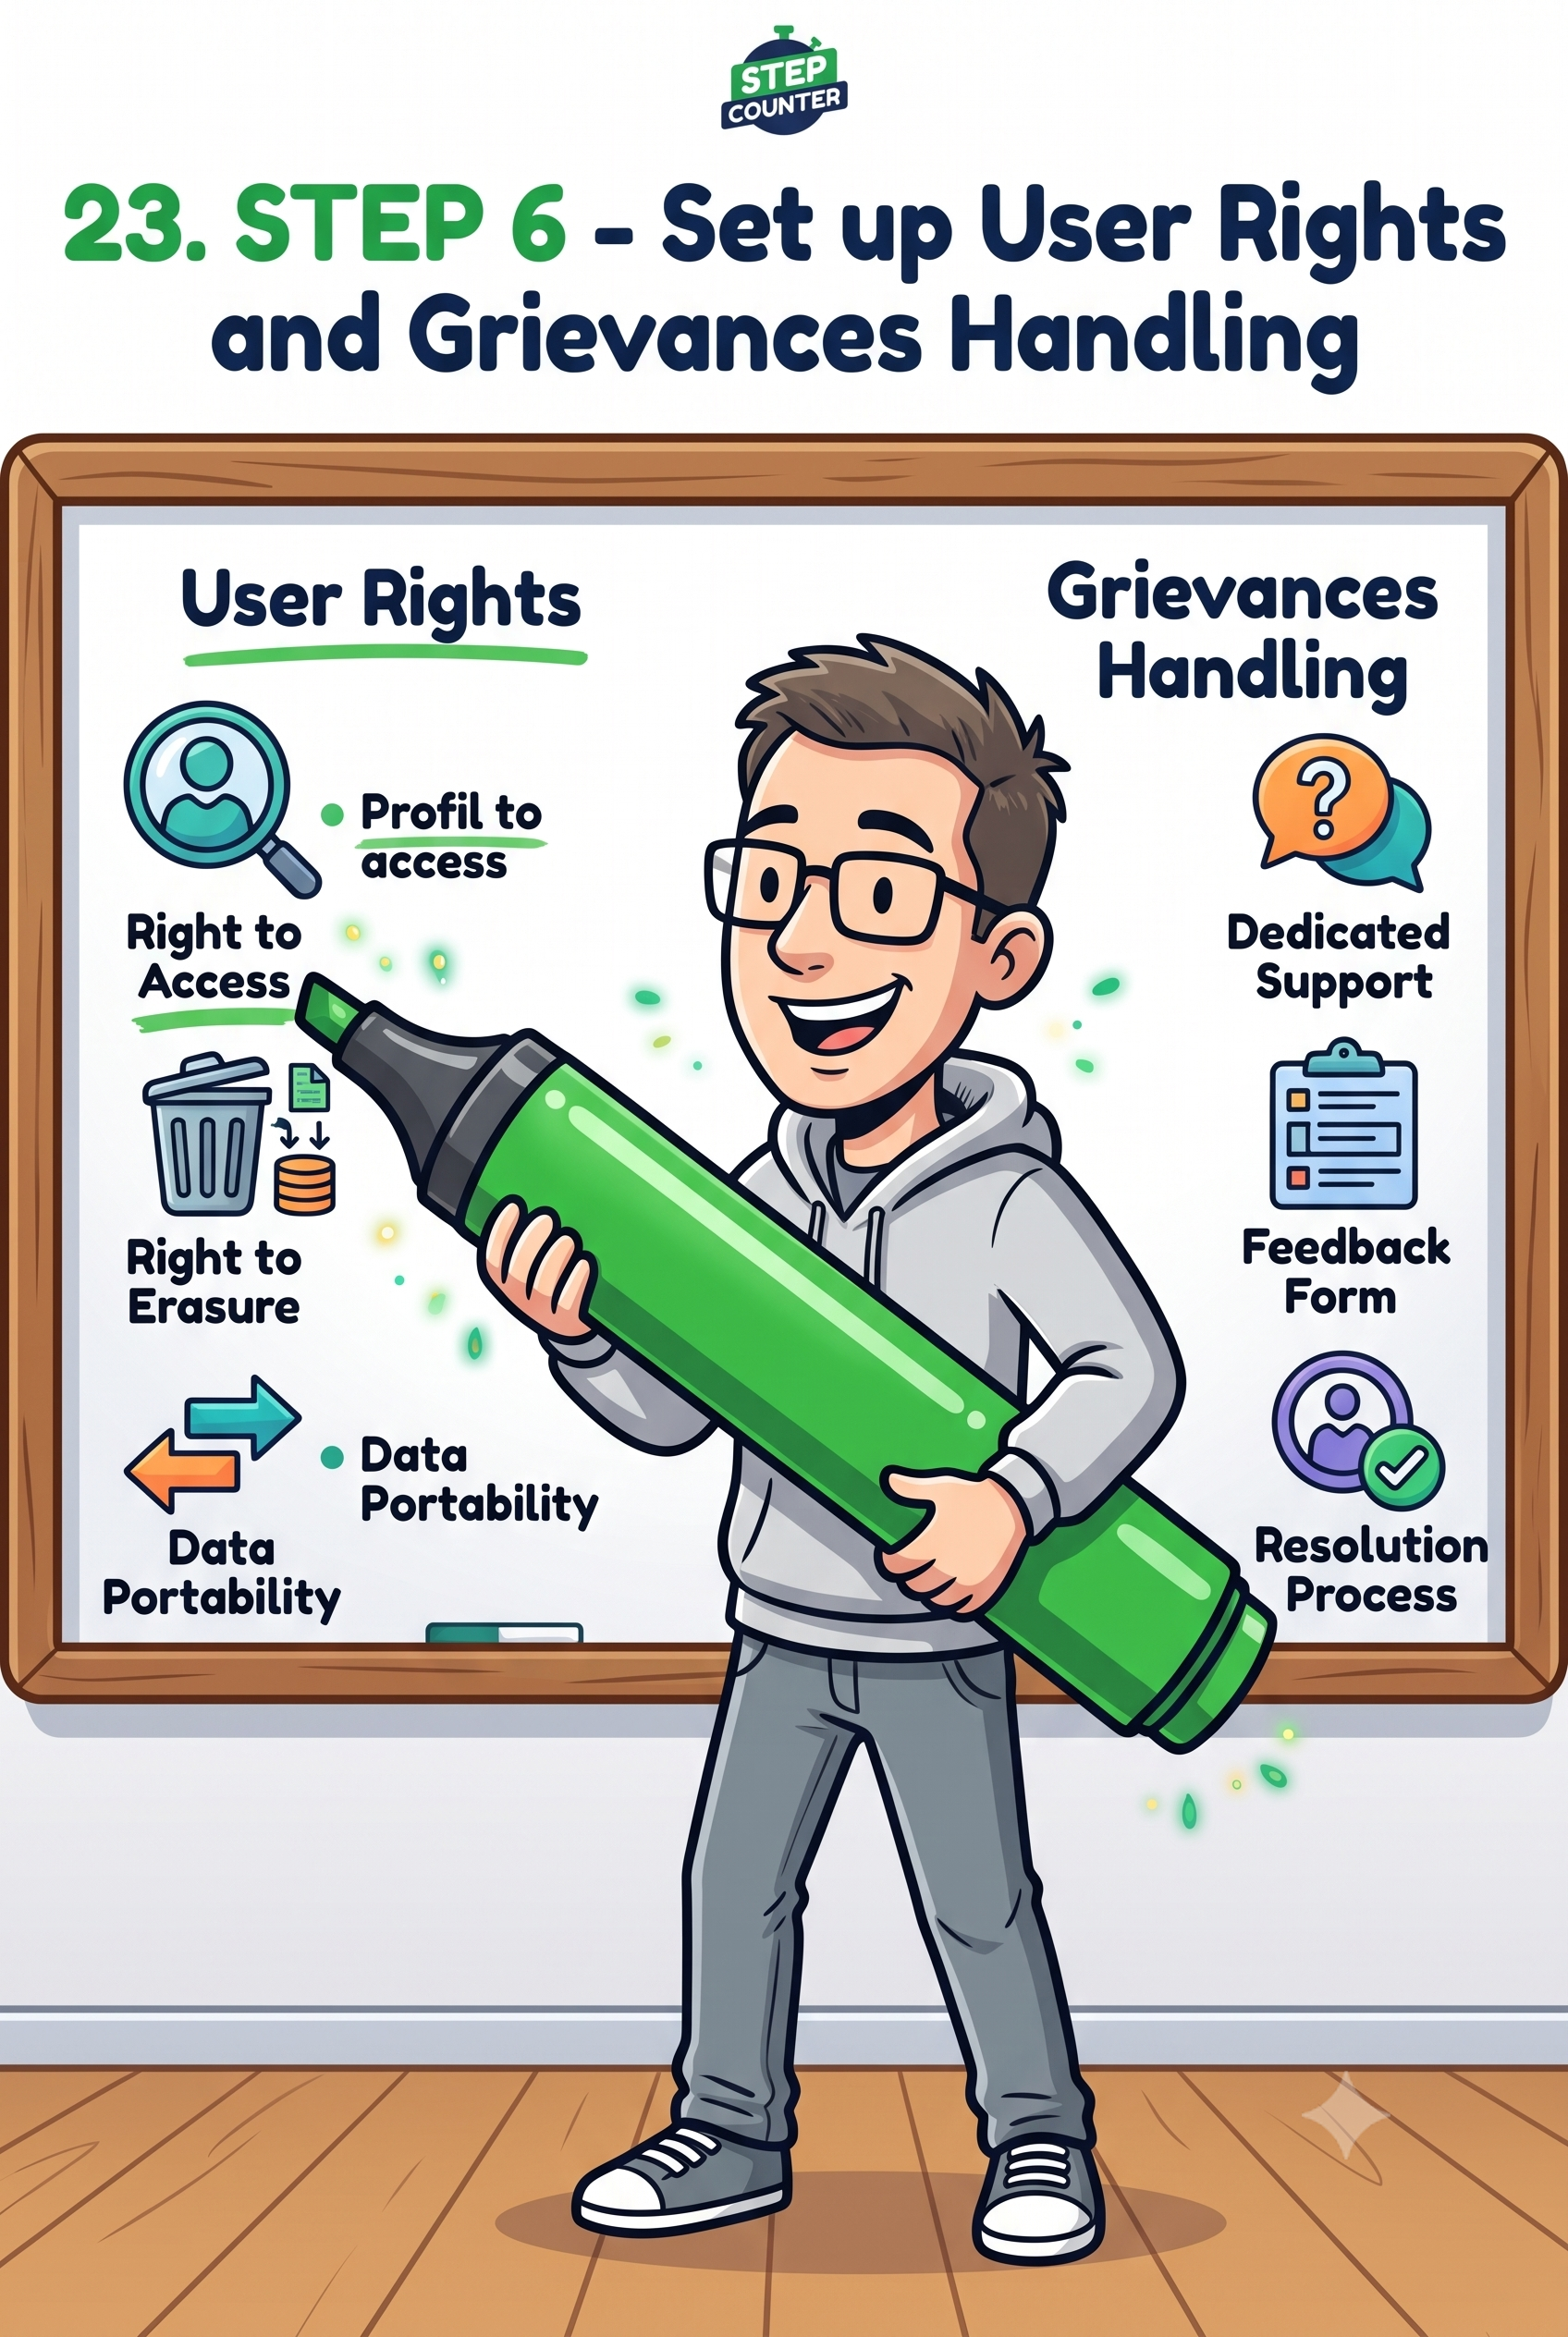
Issue #106
23. STEP 6 - Set up User Rights and Grievances Handling
Issue #107
24. STEP 7 - Data Retention
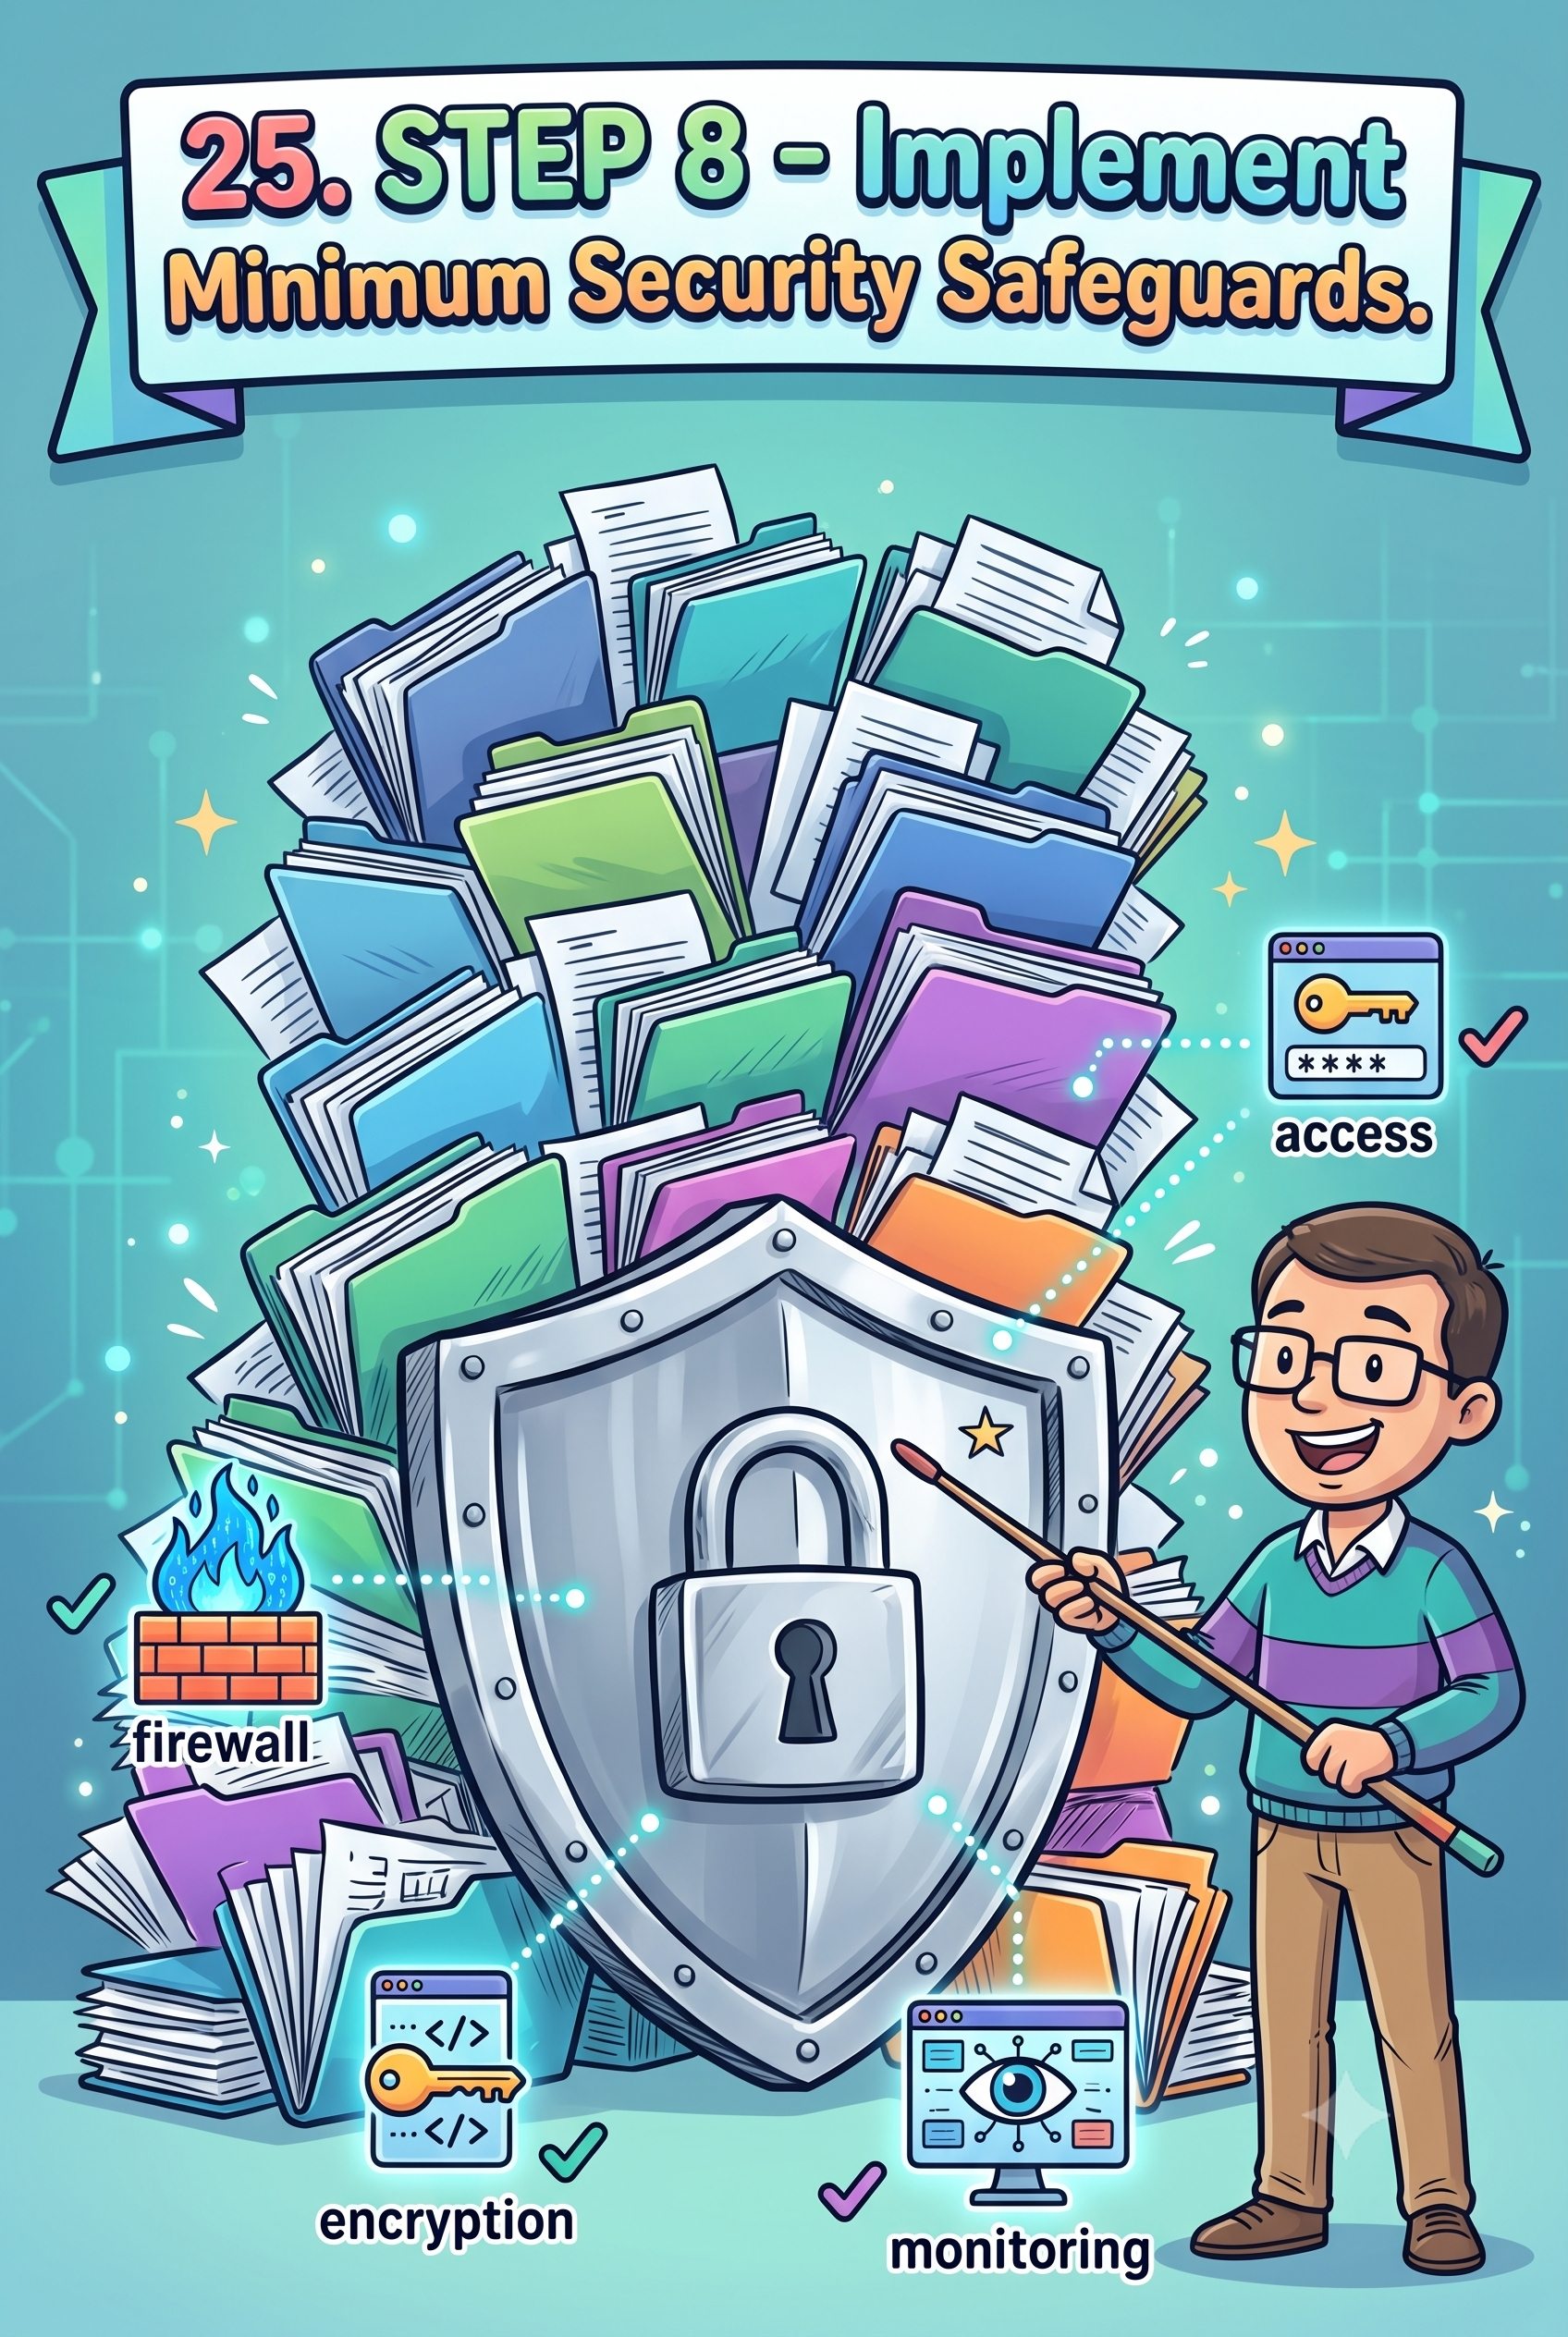
Issue #108
25. STEP 8 - Implement Minimum Security Safeguards
Issue #109
26. STEP 9 - Processor, Vendor, and Cross-Border Governance
Issue #110
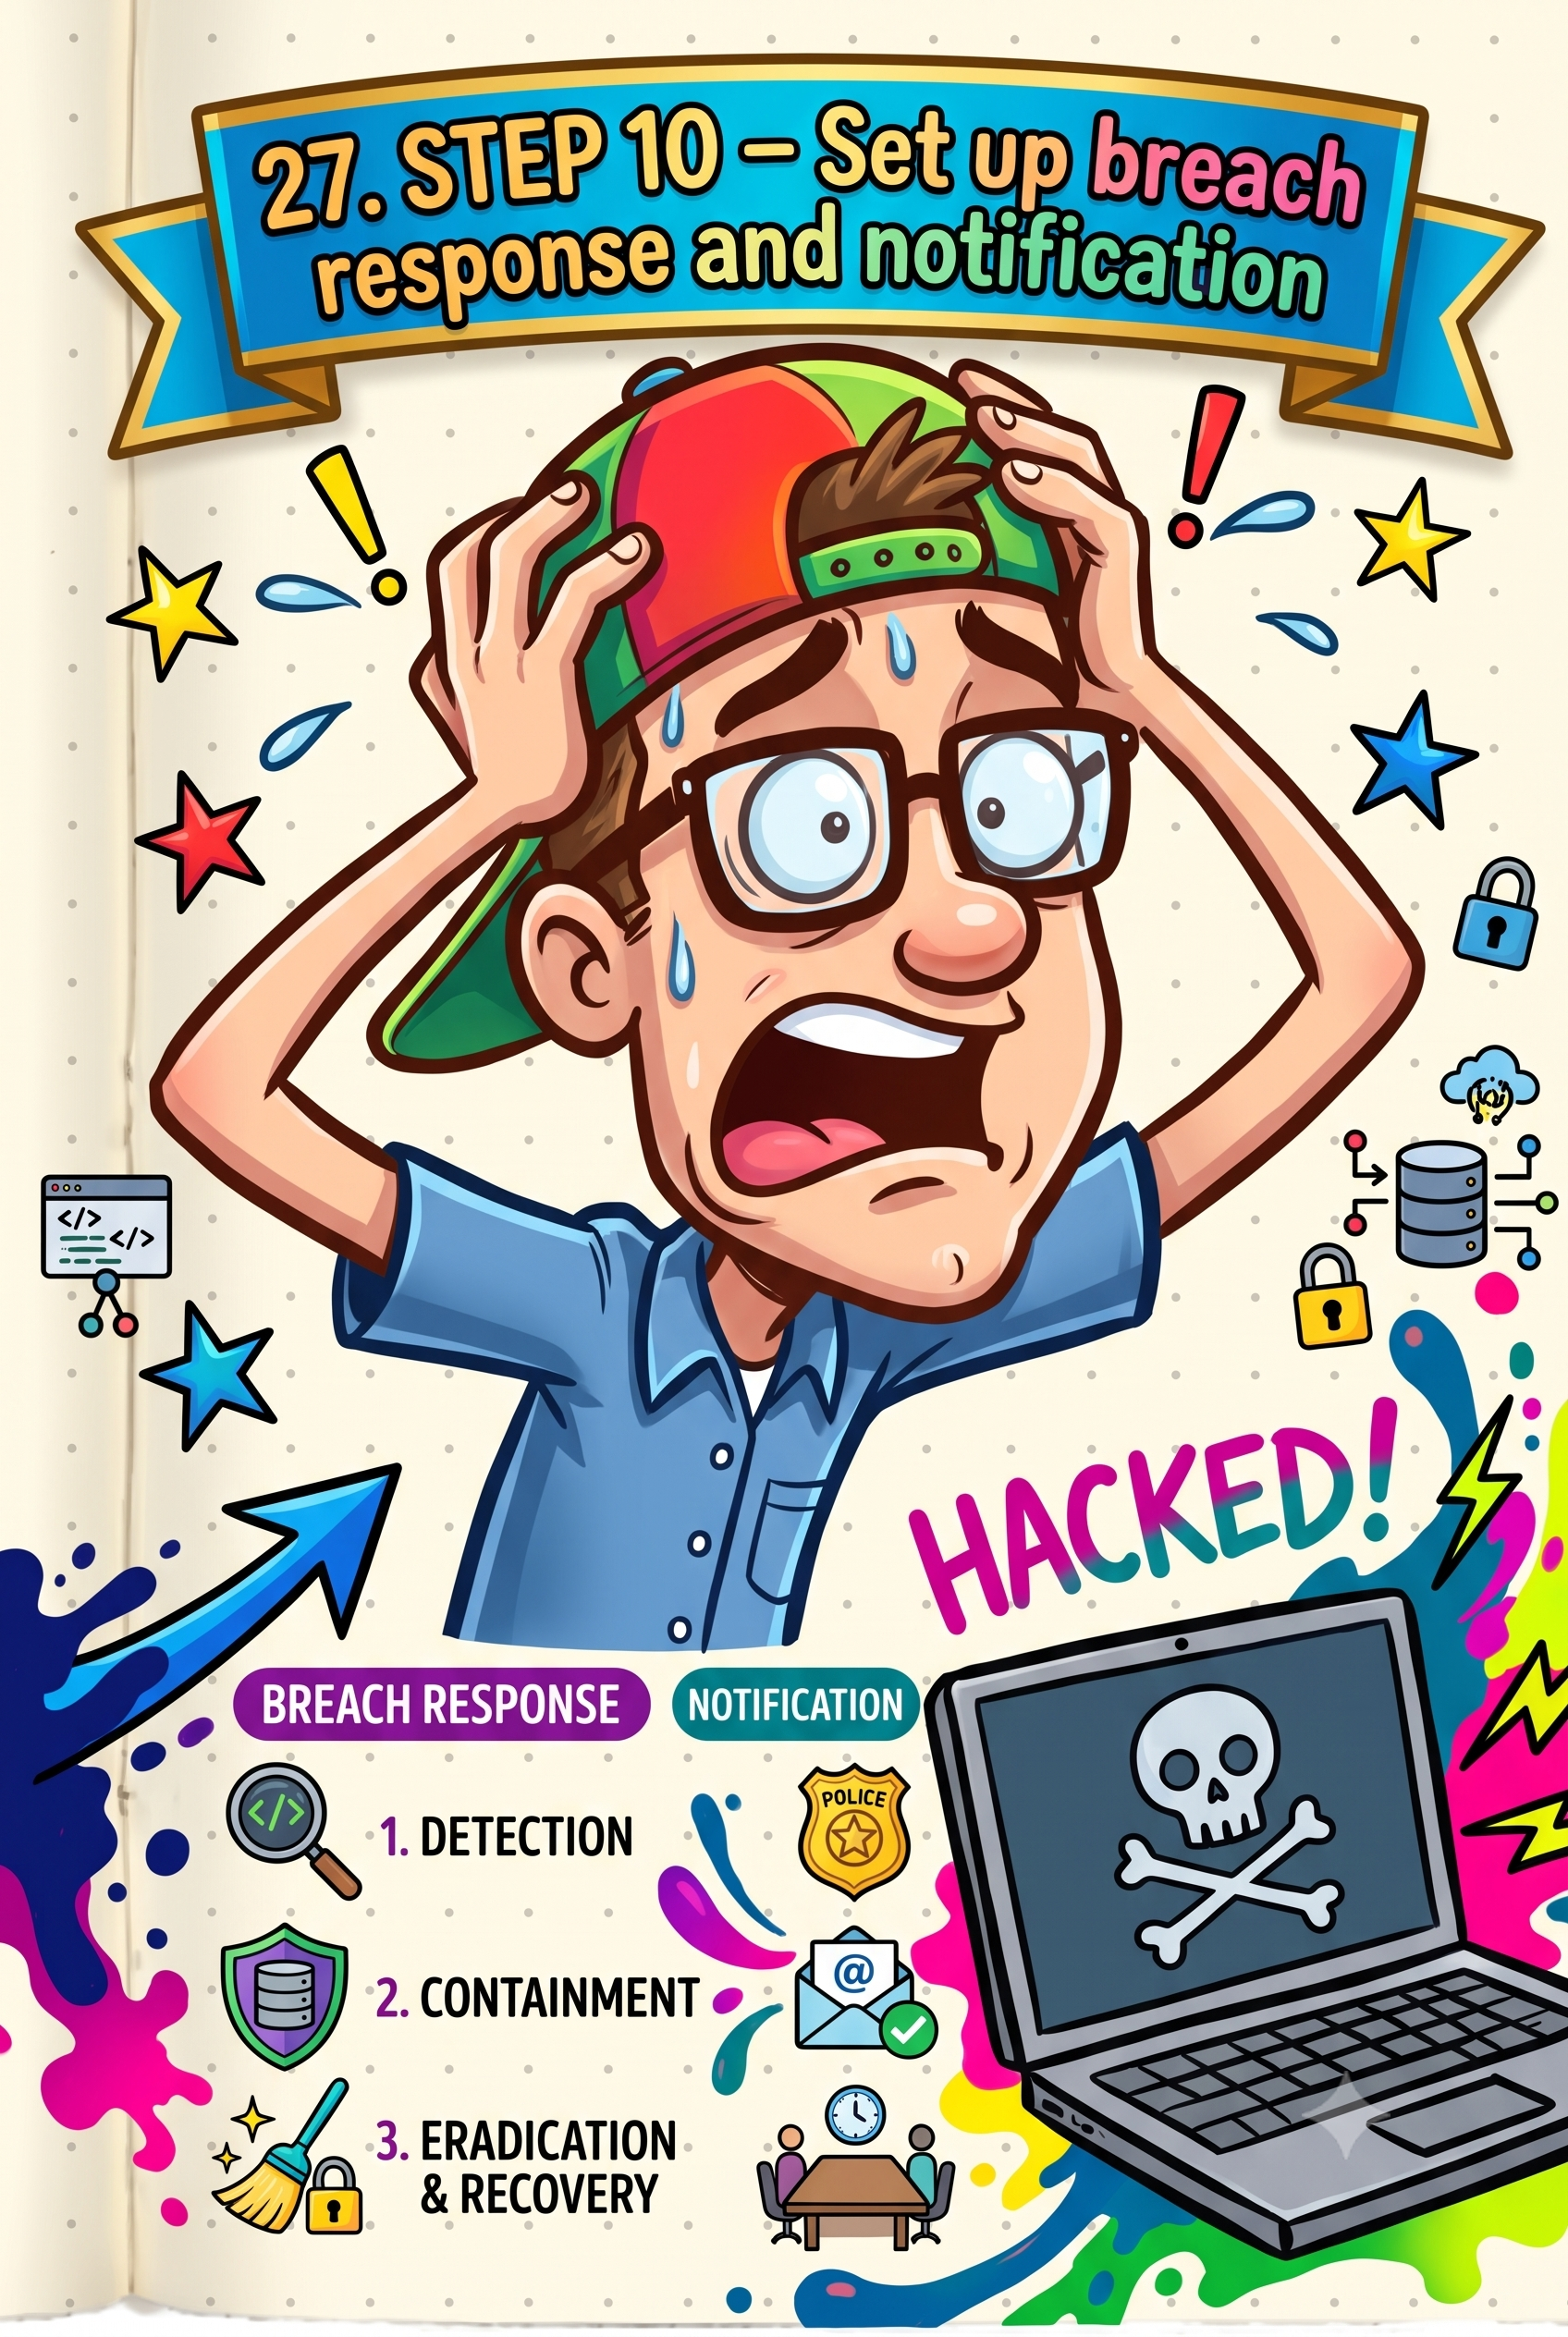
27. STEP 10 – Set up breach response and notification
Issue #111
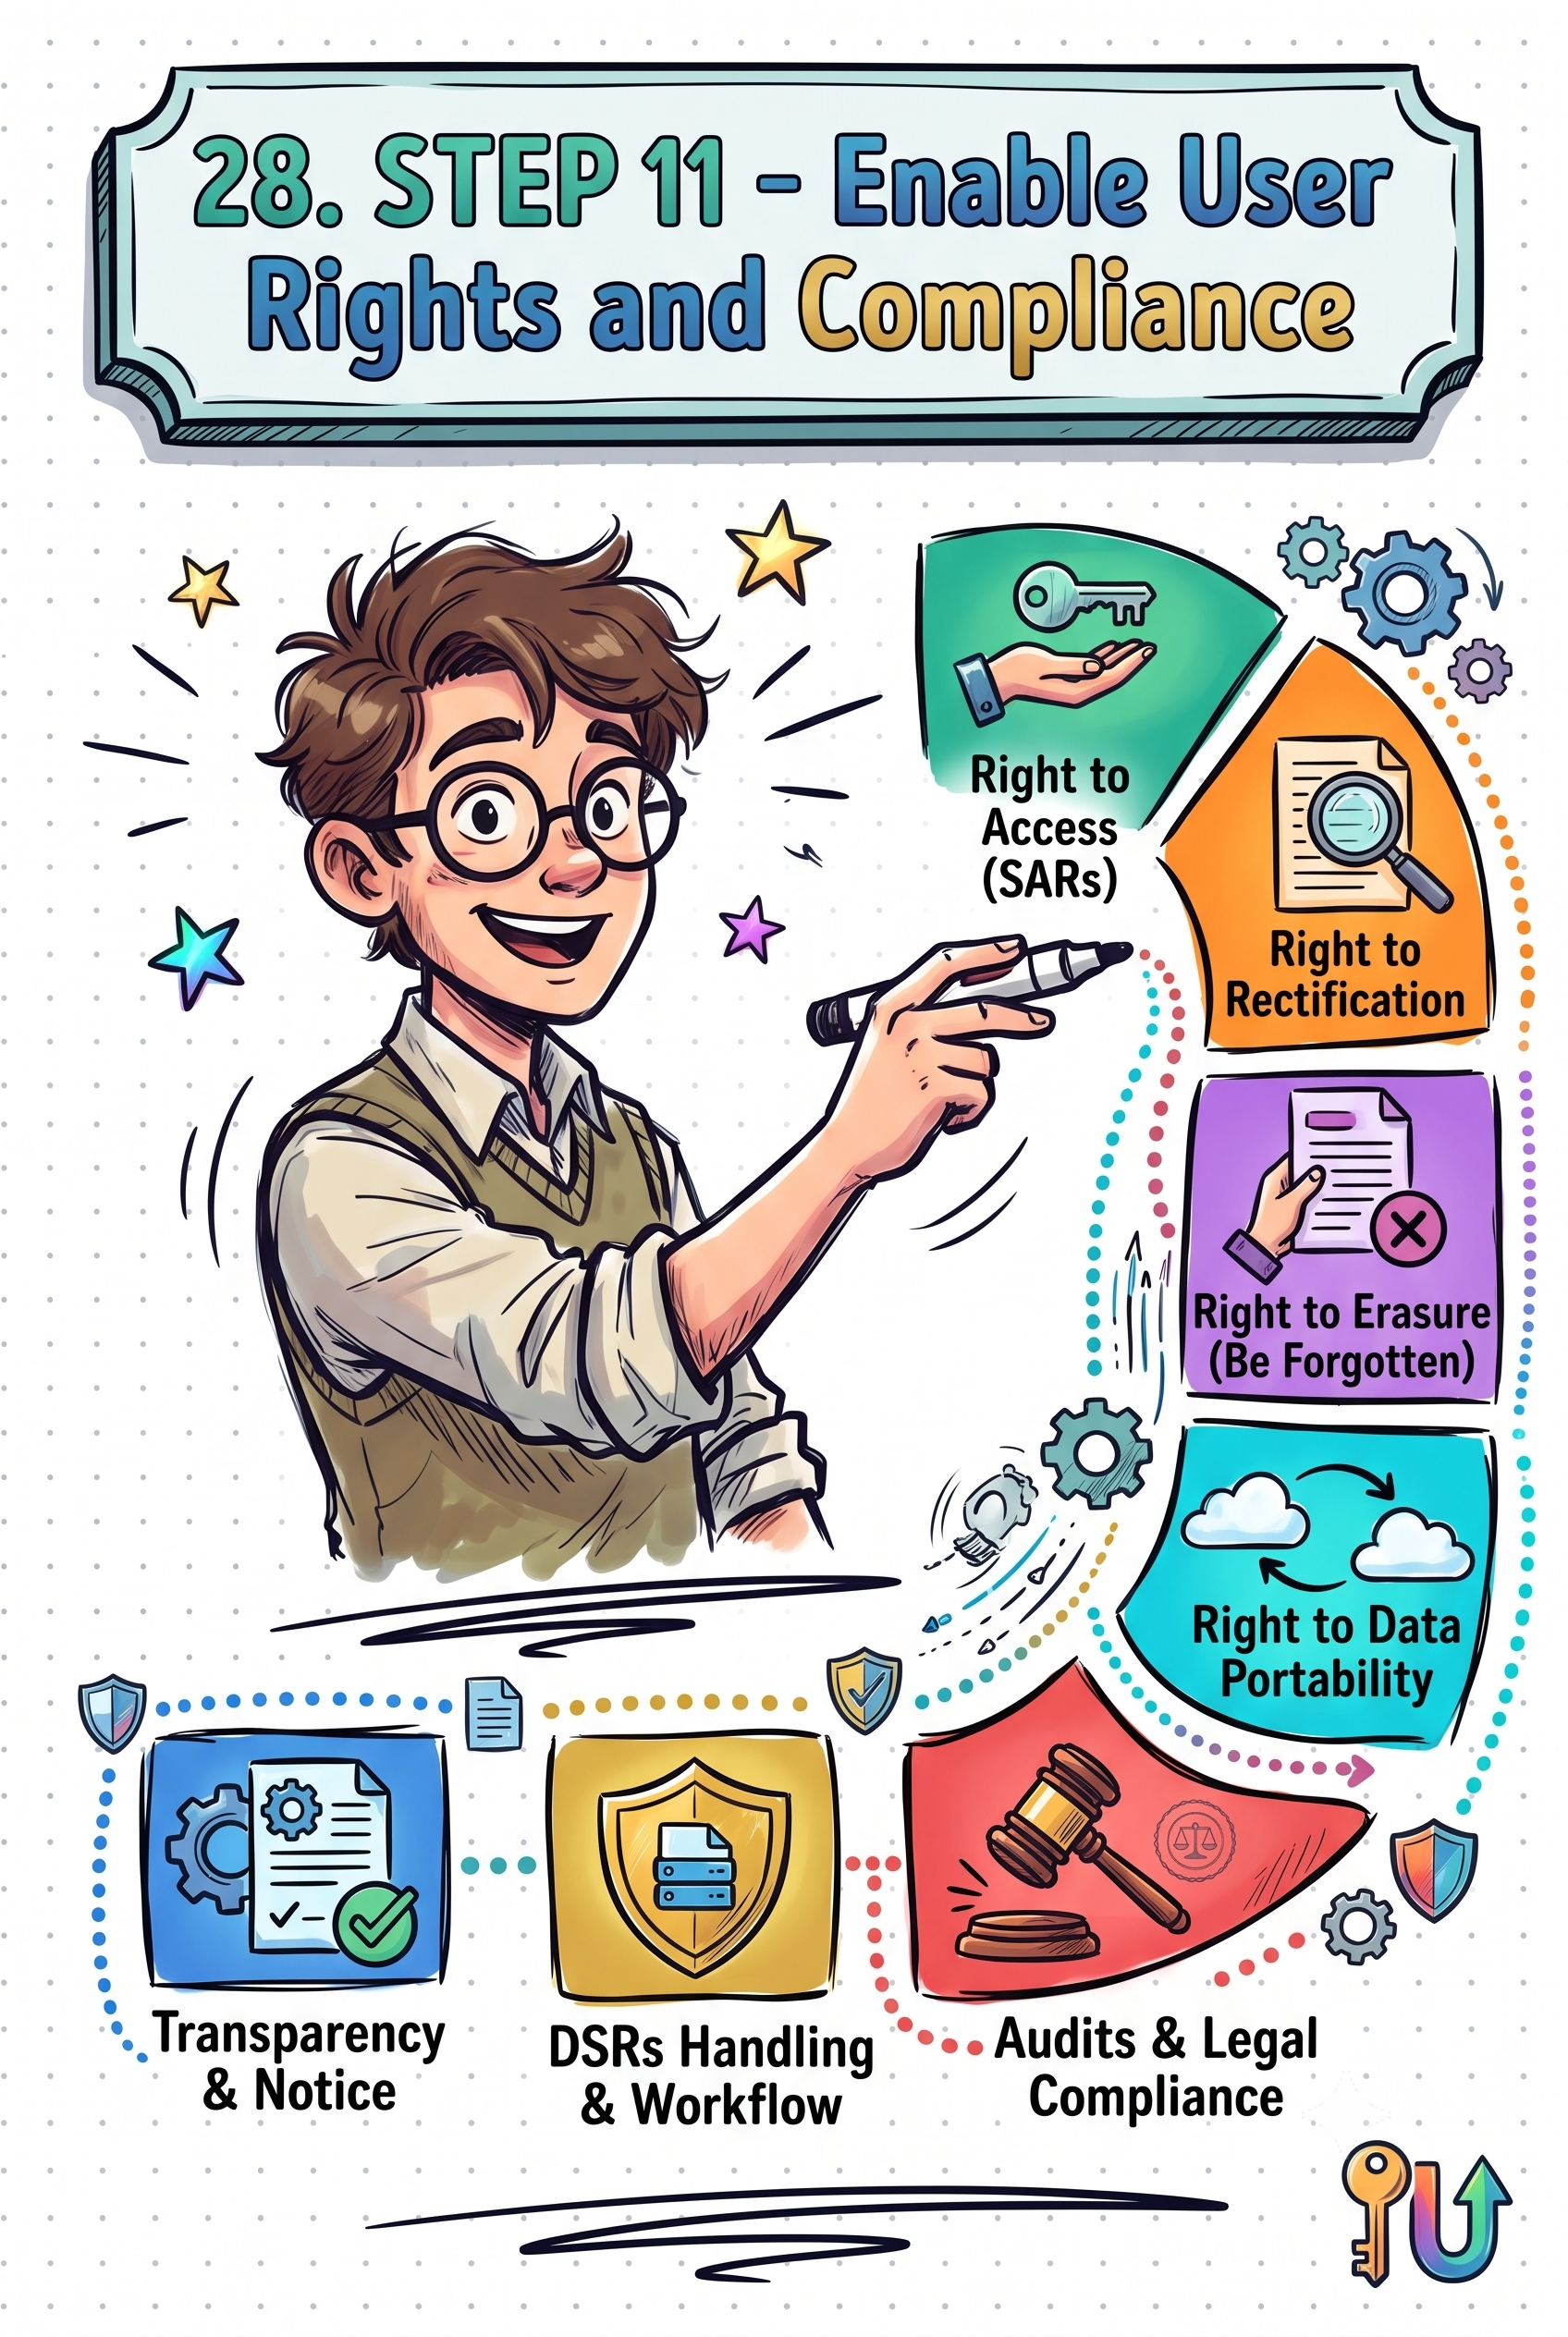
28. STEP 11 - Enable User Rights and Compliance
Issue #112
29. STEP 12 - Children, Disability, and Cross-Border
Issue #113