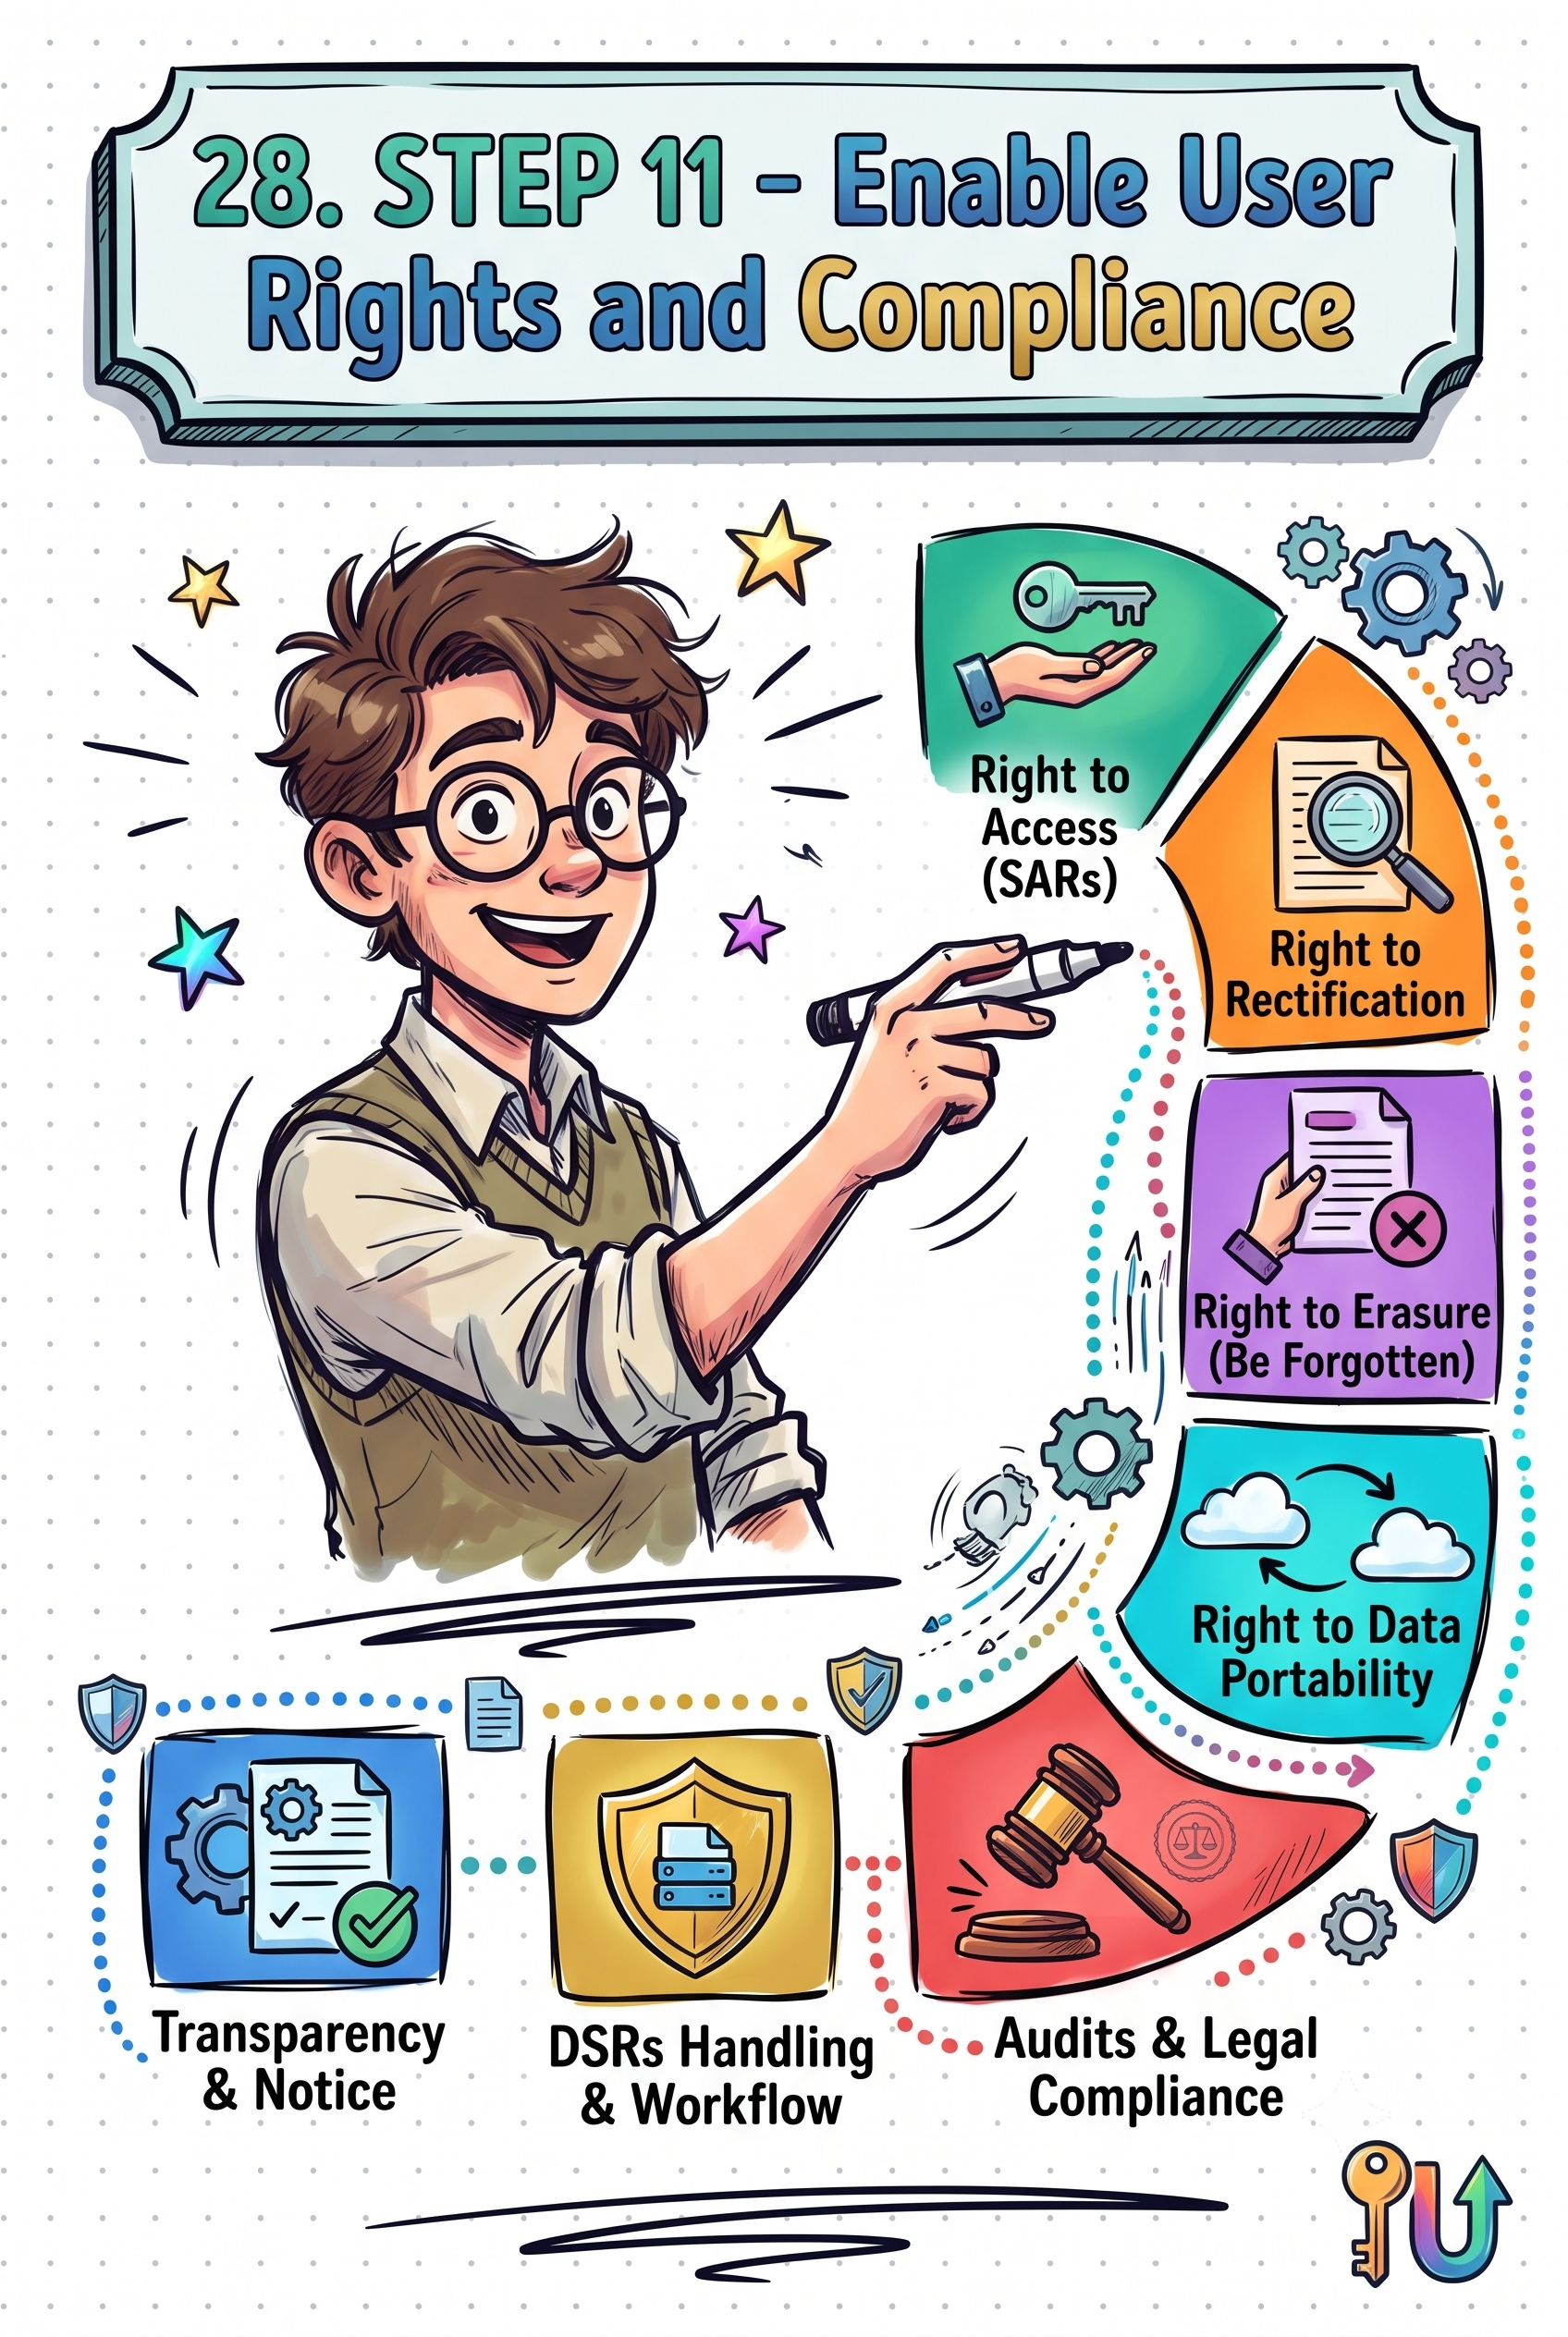
Step 11 of DPDPA compliance is enabling user rights—Data Principals must be able to access their data, request corrections, file grievances, and nominate someone to act on their behalf.
Publish a dedicated contact person and email address (like privacy@yourcompany.com) in your website footer, privacy policy, and notices.
Document SOPs for every rights request type, respond within 15–30 days (maximum 90 days), and maintain a Rights Request Log capturing date, requester, request type, and action taken.
Transparency and responsiveness here prevent escalation to the Data Protection Board.