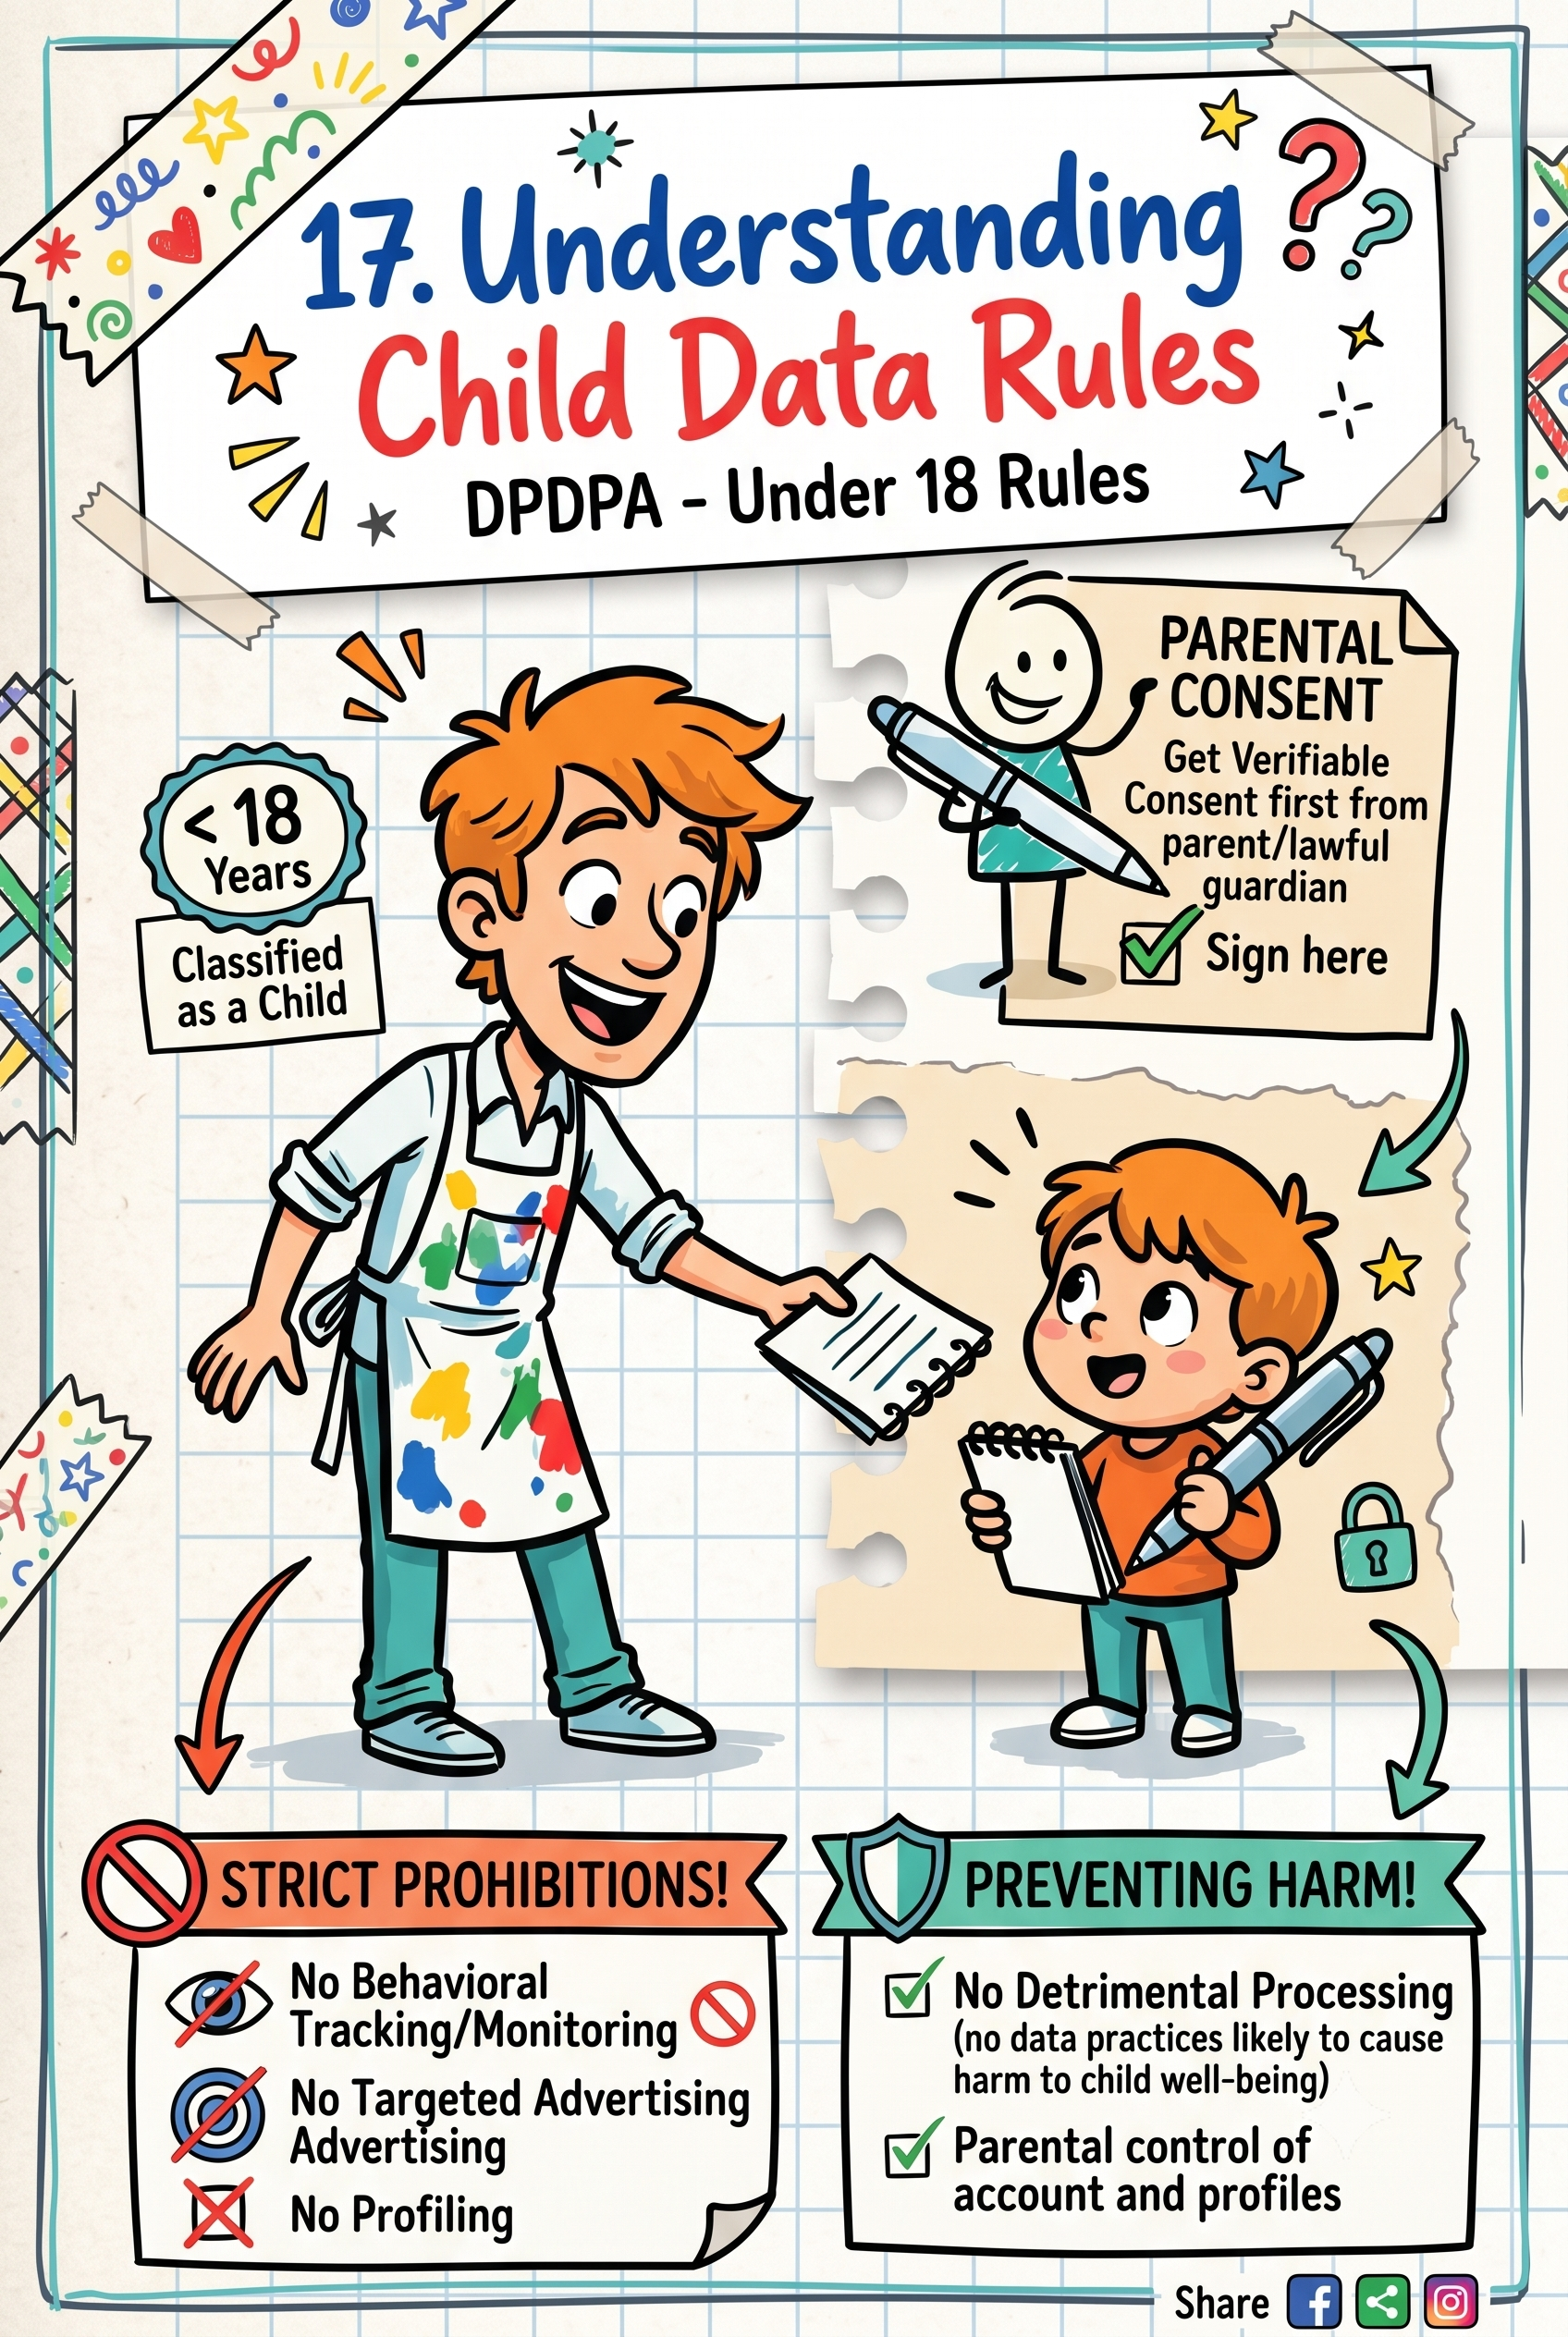
Under DPDPA Sections 9(1) and 9(3), any company processing data of a child under 18 must obtain verifiable parental consent and is strictly prohibited from tracking, behavior monitoring, targeting, or serving individualized advertising to the child.
The Fourth Schedule provides narrow exemptions for specific organizations—hospitals, schools, daycare centers, and caregivers—that must process child data for health or safety purposes, but only within those limited use cases.
Ankur Technology avoided this complexity entirely by declaring all services 18+ and refusing to collect children's data—a smart compliance strategy for most businesses.
If you ever expand to training minors, you must follow Section 9: verifiable parental consent, zero behavior tracking, and no targeted advertising to children.