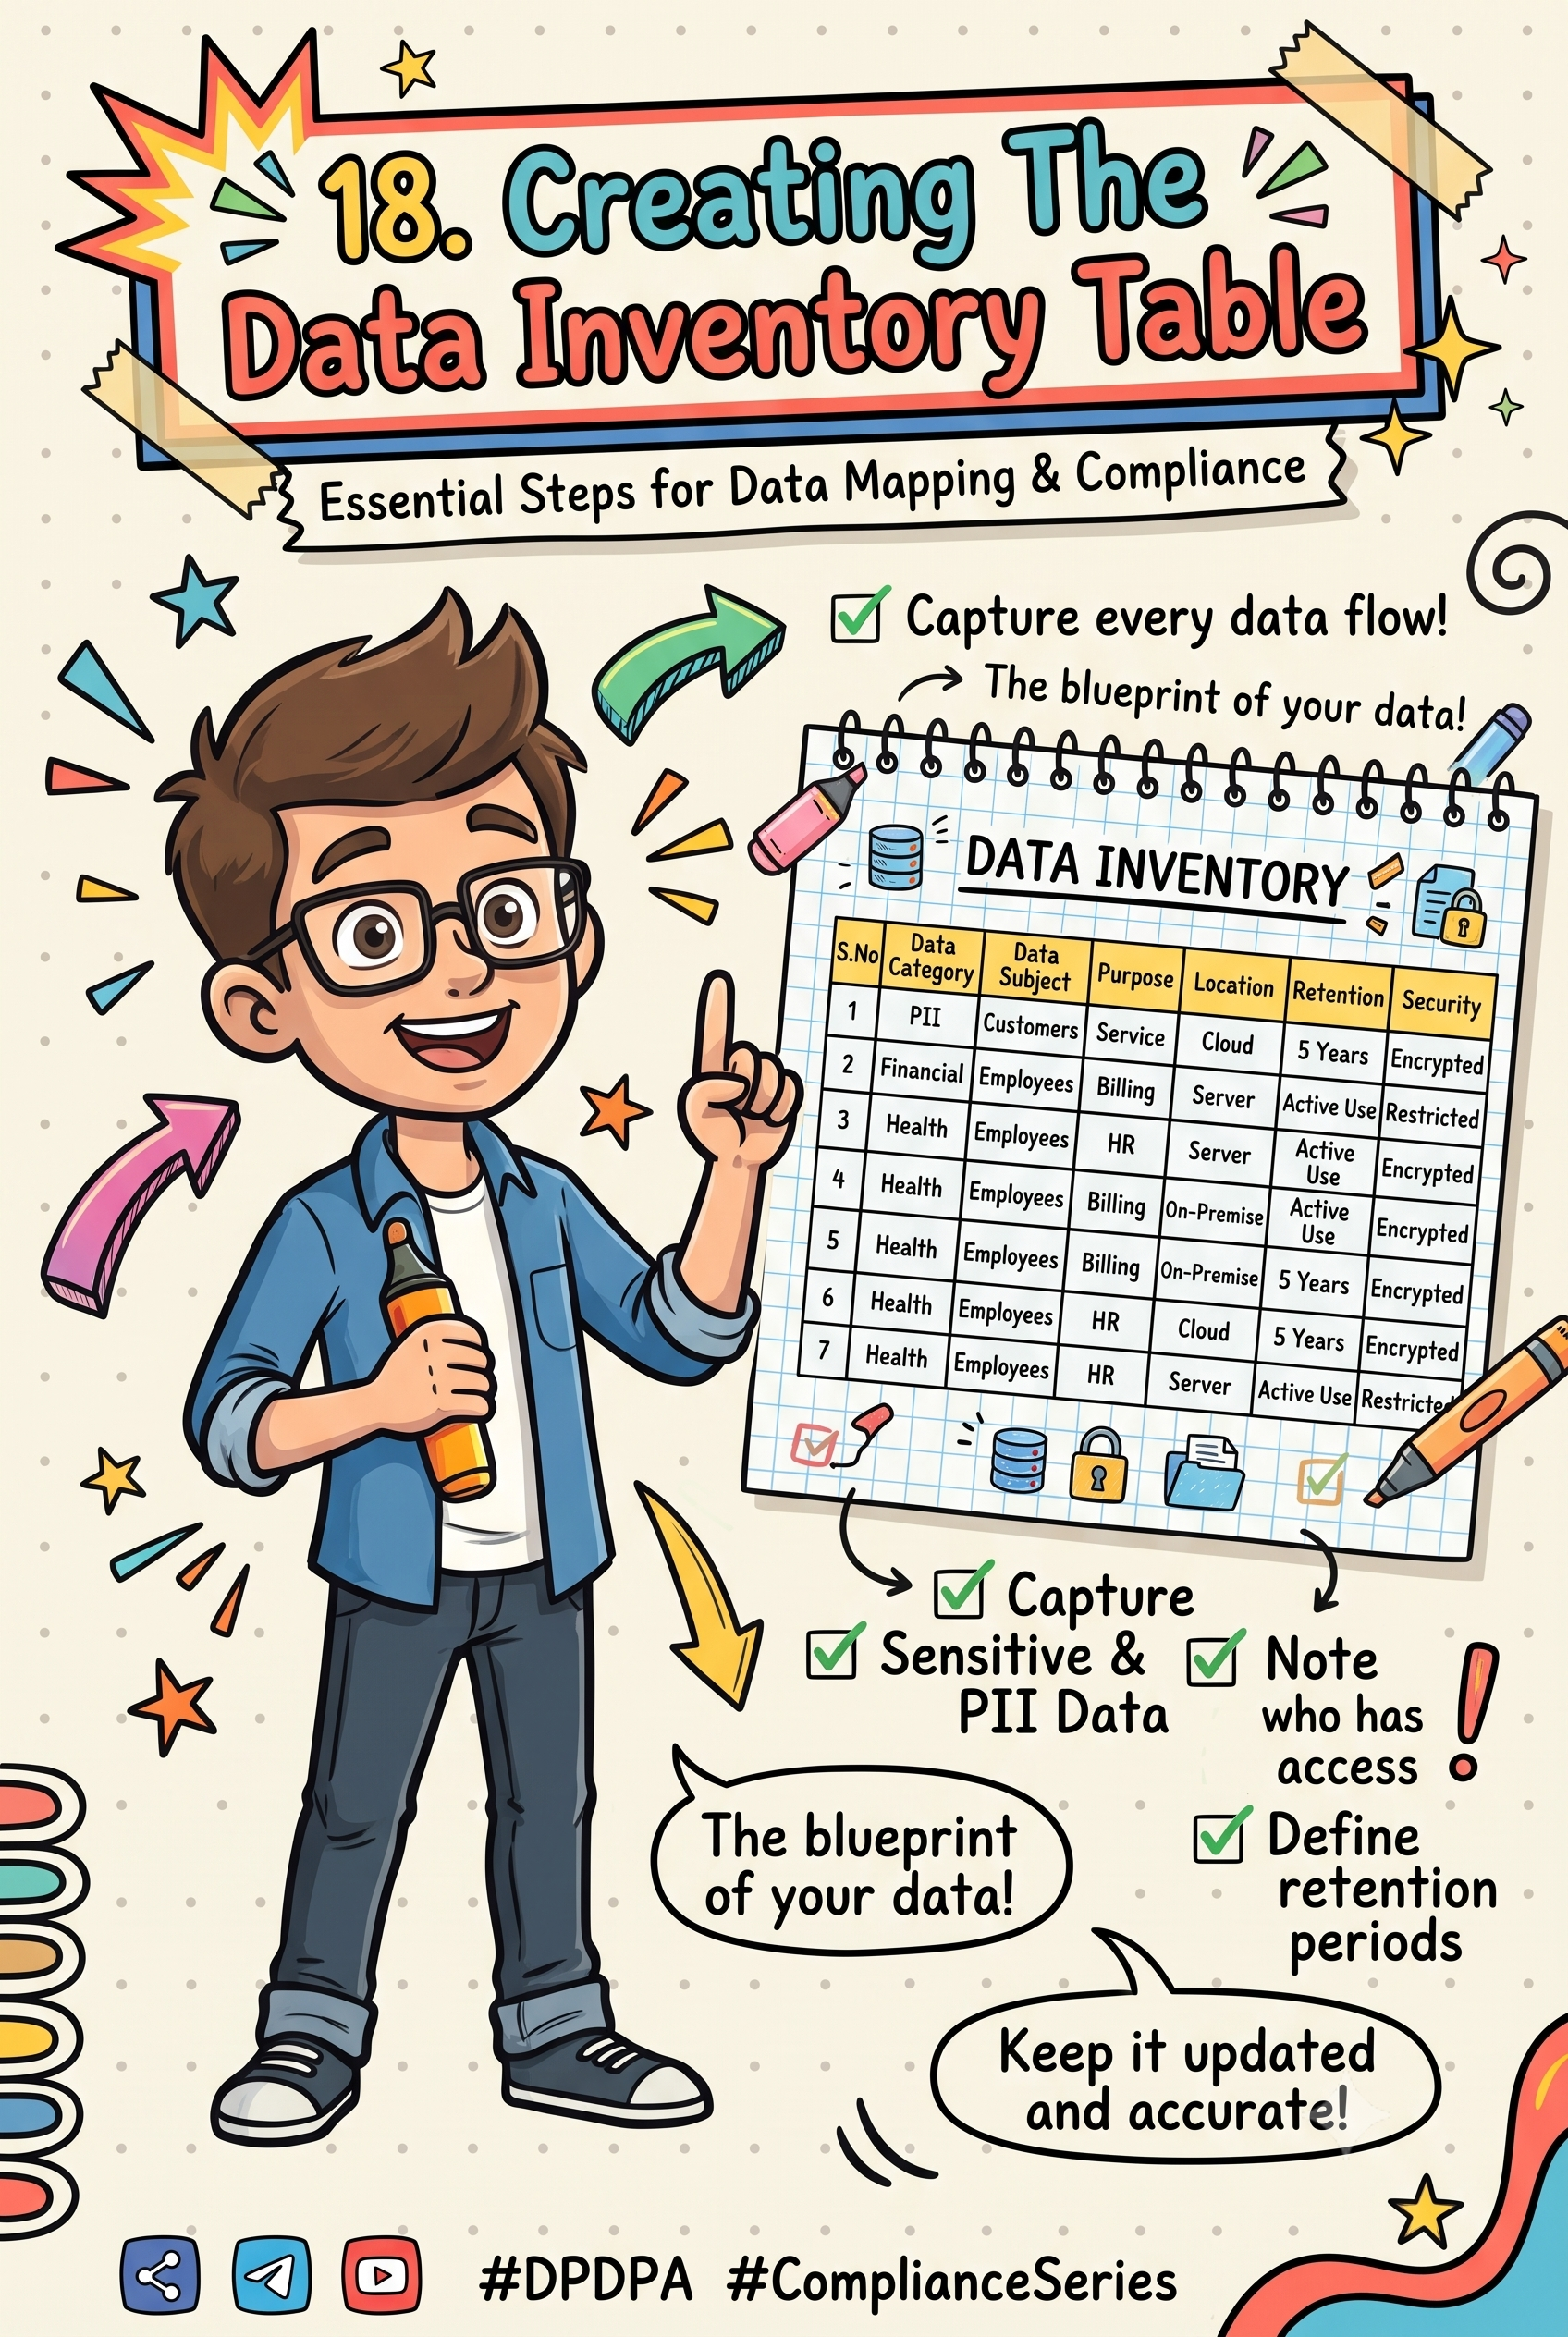
Build your DPDPA data inventory with a scope note, system list, version information, and a structured table capturing what data you collect, why, where it's stored, and retention periods—because undocumented data collection is like black money: against the law.
The Second Schedule provides minimum standards for two special situations: government schemes (Section 7(b)) and research/archival purposes (Section 17(2)(b)), offering a lighter compliance regime if you follow its checklist.
Key Second Schedule requirements include ensuring processing is lawful, data is used only for the stated purpose, and appropriate safeguards are maintained.
A well-built data inventory is the backbone of DPDPA compliance—without it, you cannot secure, retain, or delete data effectively.