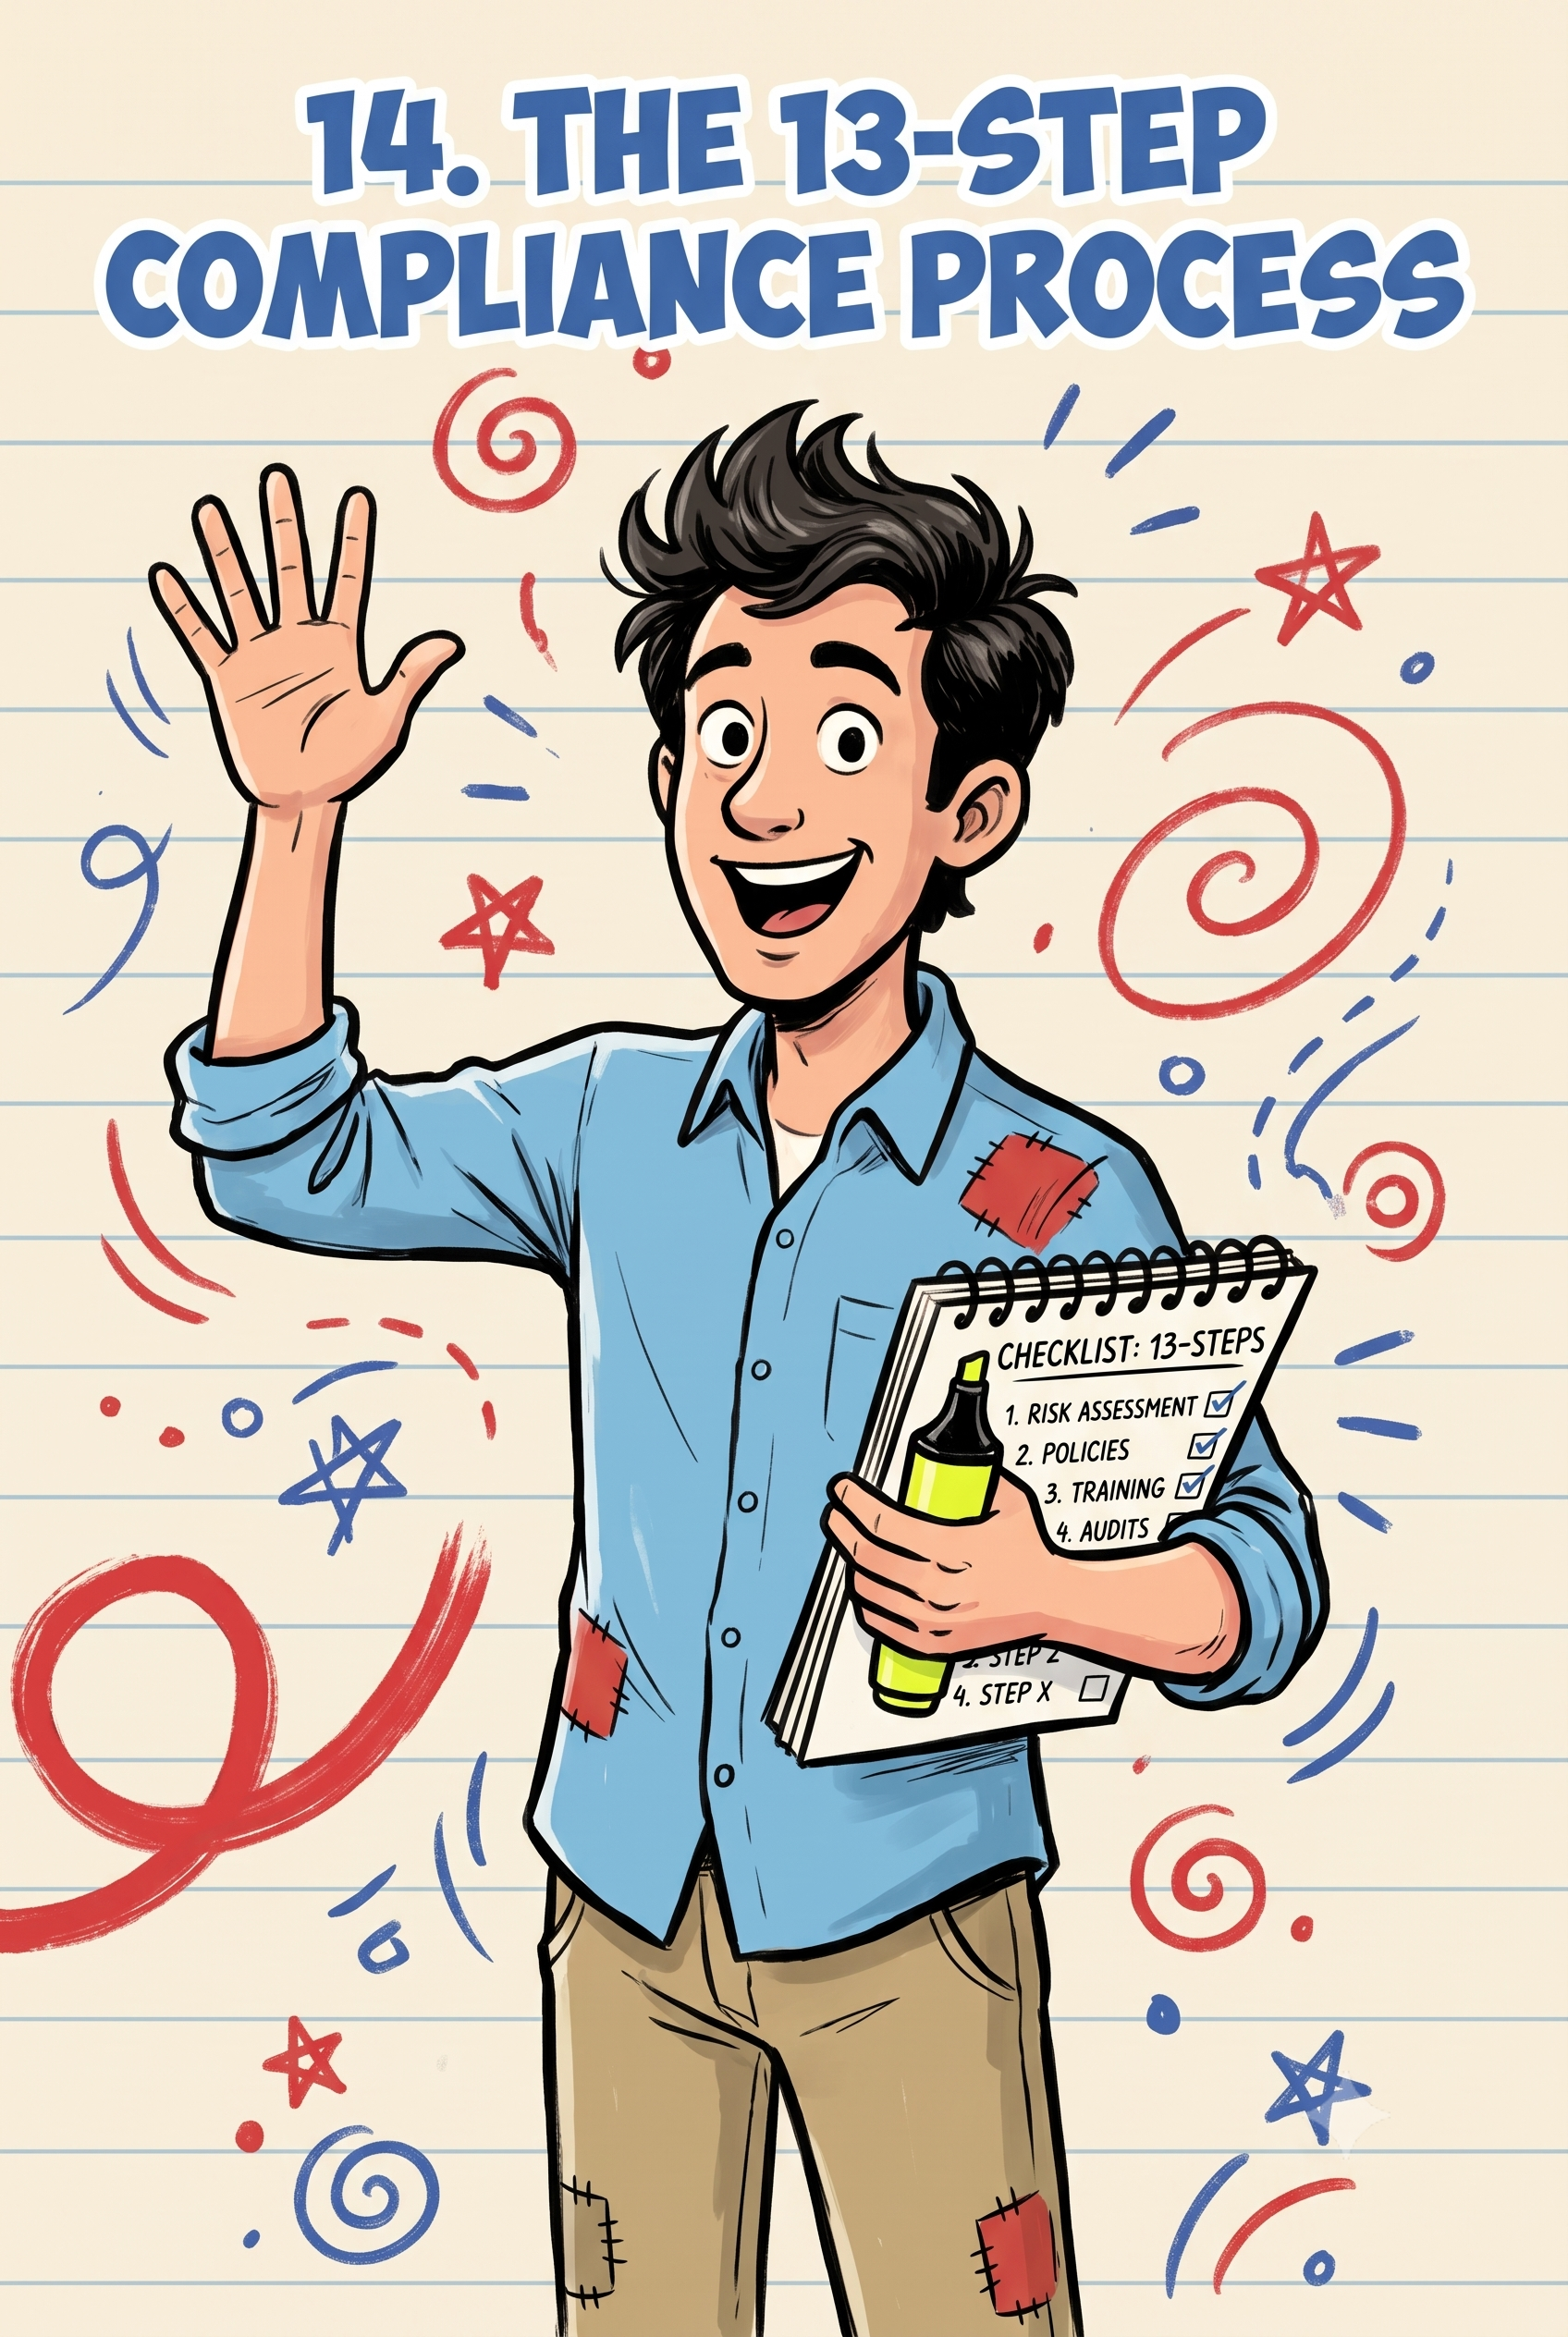
Follow this 13-step DPDPA compliance roadmap: confirm applicability, appoint a Privacy Lead, build a data inventory, draft privacy notices, map legal grounds, set up user rights and grievance handling, define retention and deletion, implement security safeguards, manage third-party processors, create a breach response plan, address children's data and cross-border transfers, and conduct awareness training with internal audits.
Step 1 is critical—confirm the Act applies to you (processing digital personal data in India or offering services to people in India) and formally appoint an internal Privacy Lead or DPDP Owner.
Unlike a DPO (mandatory only for Significant Data Fiduciaries under Section 10), a Privacy Lead is a voluntary internal role for non-SDF organizations handling day-to-day privacy issues.
Document everything in a Governance Charter that defines roles, responsibilities, and team structure—just like Ankur Technology did with representatives from Sales, Training, IT, and HR.