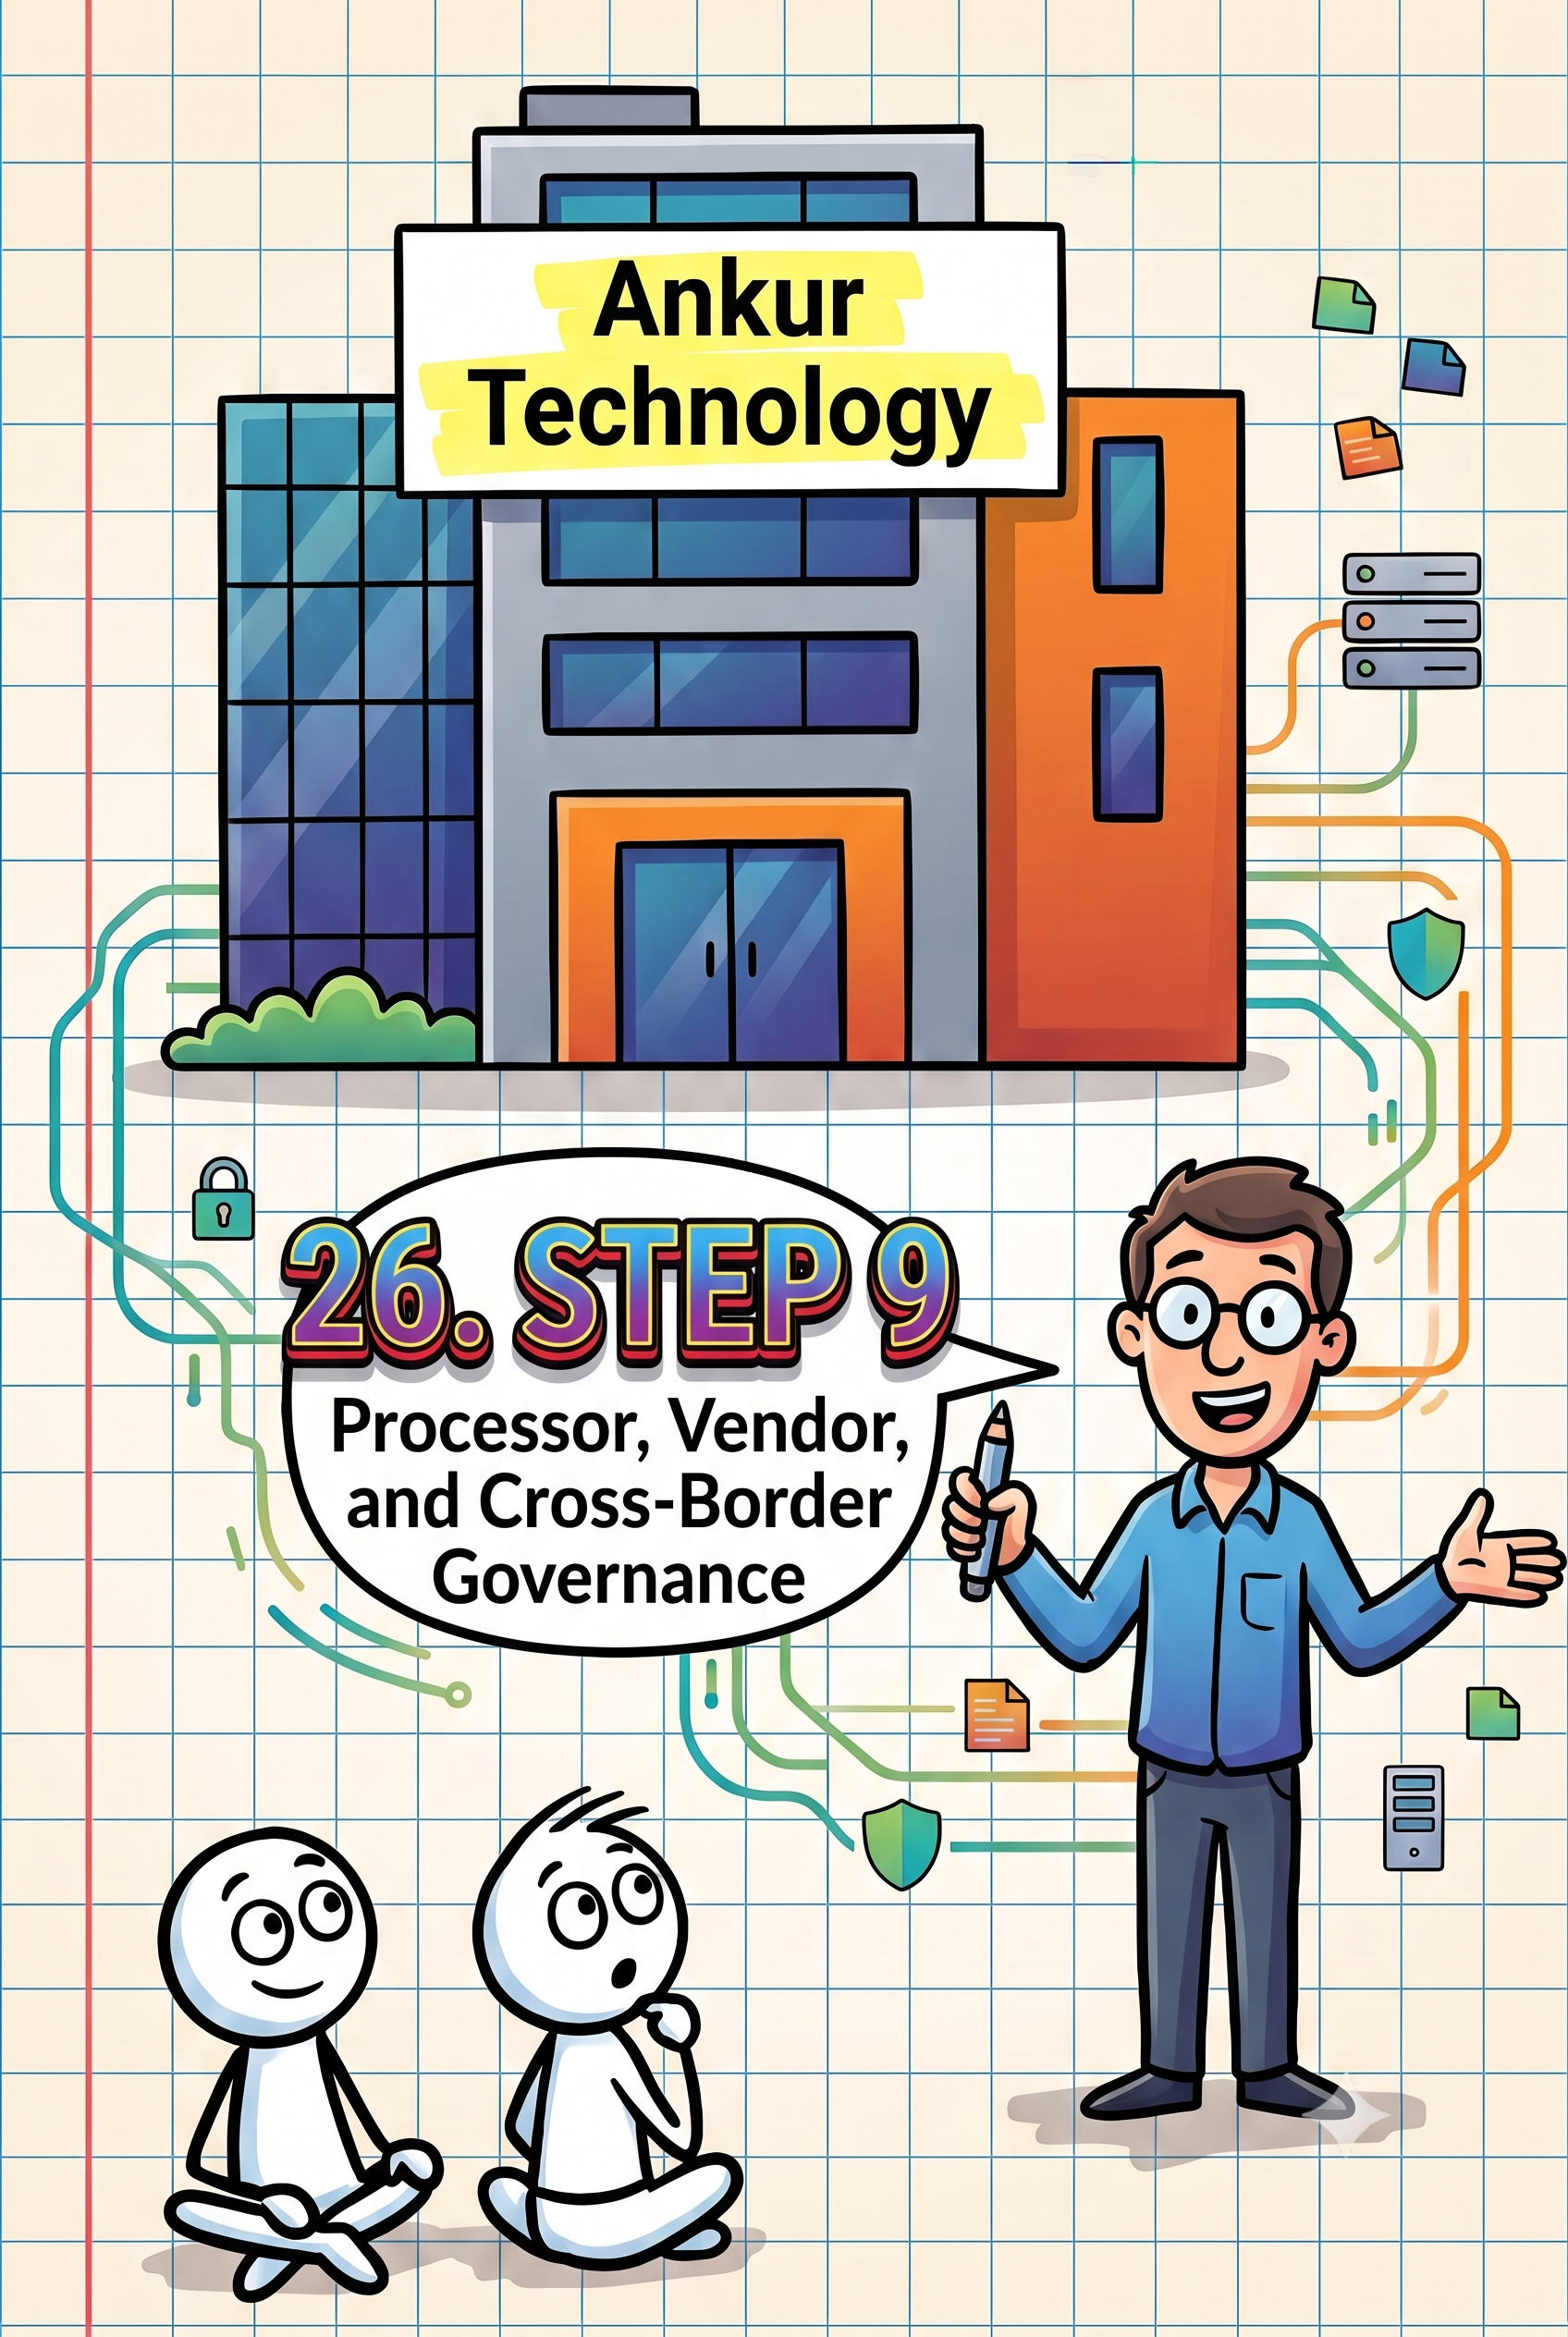
Step 9 of DPDPA compliance is governing processors, vendors, and cross-border data transfers—under Section 8, you remain fully responsible for processing done by your Data Processors, so accountability cannot be outsourced.
Create a Vendor Register listing all processors (SaaS, freelancers, marketing agencies) with data types and locations, then embed contractual clauses covering instructions, Rule 6 security safeguards, DPDP rights support, and data deletion/retention at engagement end.
Section 16 permits cross-border transfers except to government-blacklisted countries, while Rule 15 requires meeting any Central Government requirements for making data available to foreign state entities.
Ankur Technology's implementation: vendor list with data locations (India and US), privacy notice disclosing overseas processing, and readiness to adjust if transfer restrictions change.