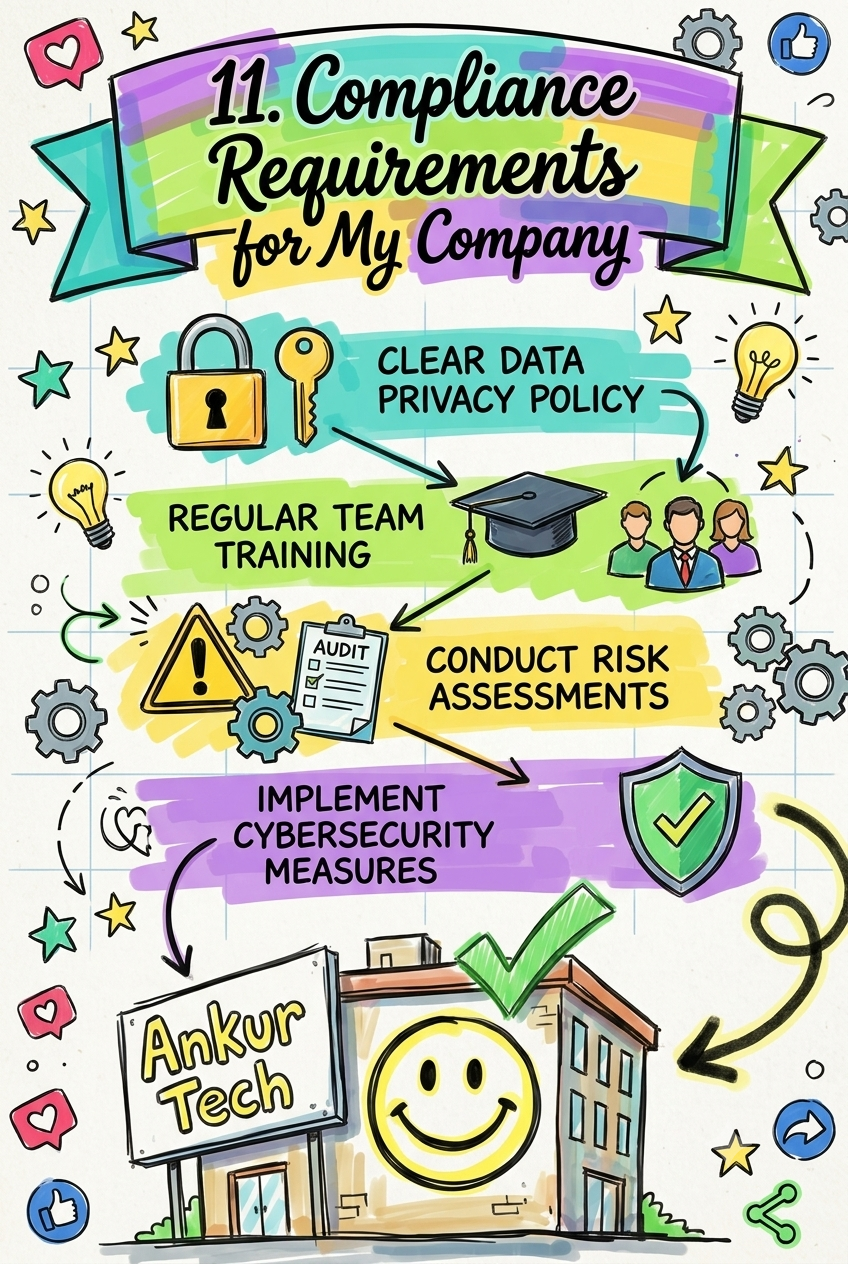
DPDPA compliance starts with Lawful Purpose and Legal Basis—collect data only for a valid reason and with clear consent, then notify Data Principals about what you collect, why, and their rights.
Core Data Fiduciary obligations include data accuracy, purpose limitation, retention limits, reasonable security safeguards, and breach notification to both the Data Protection Board and affected individuals.
You must also publish contact details of a responsible person for queries and establish a grievance redressal mechanism for Data Principals.
Follow the November 2024 Rules to operationalize these requirements—covering Data Principal rights, cross-border transfers, and penalties—and you're on your way to full DPDPA compliance.