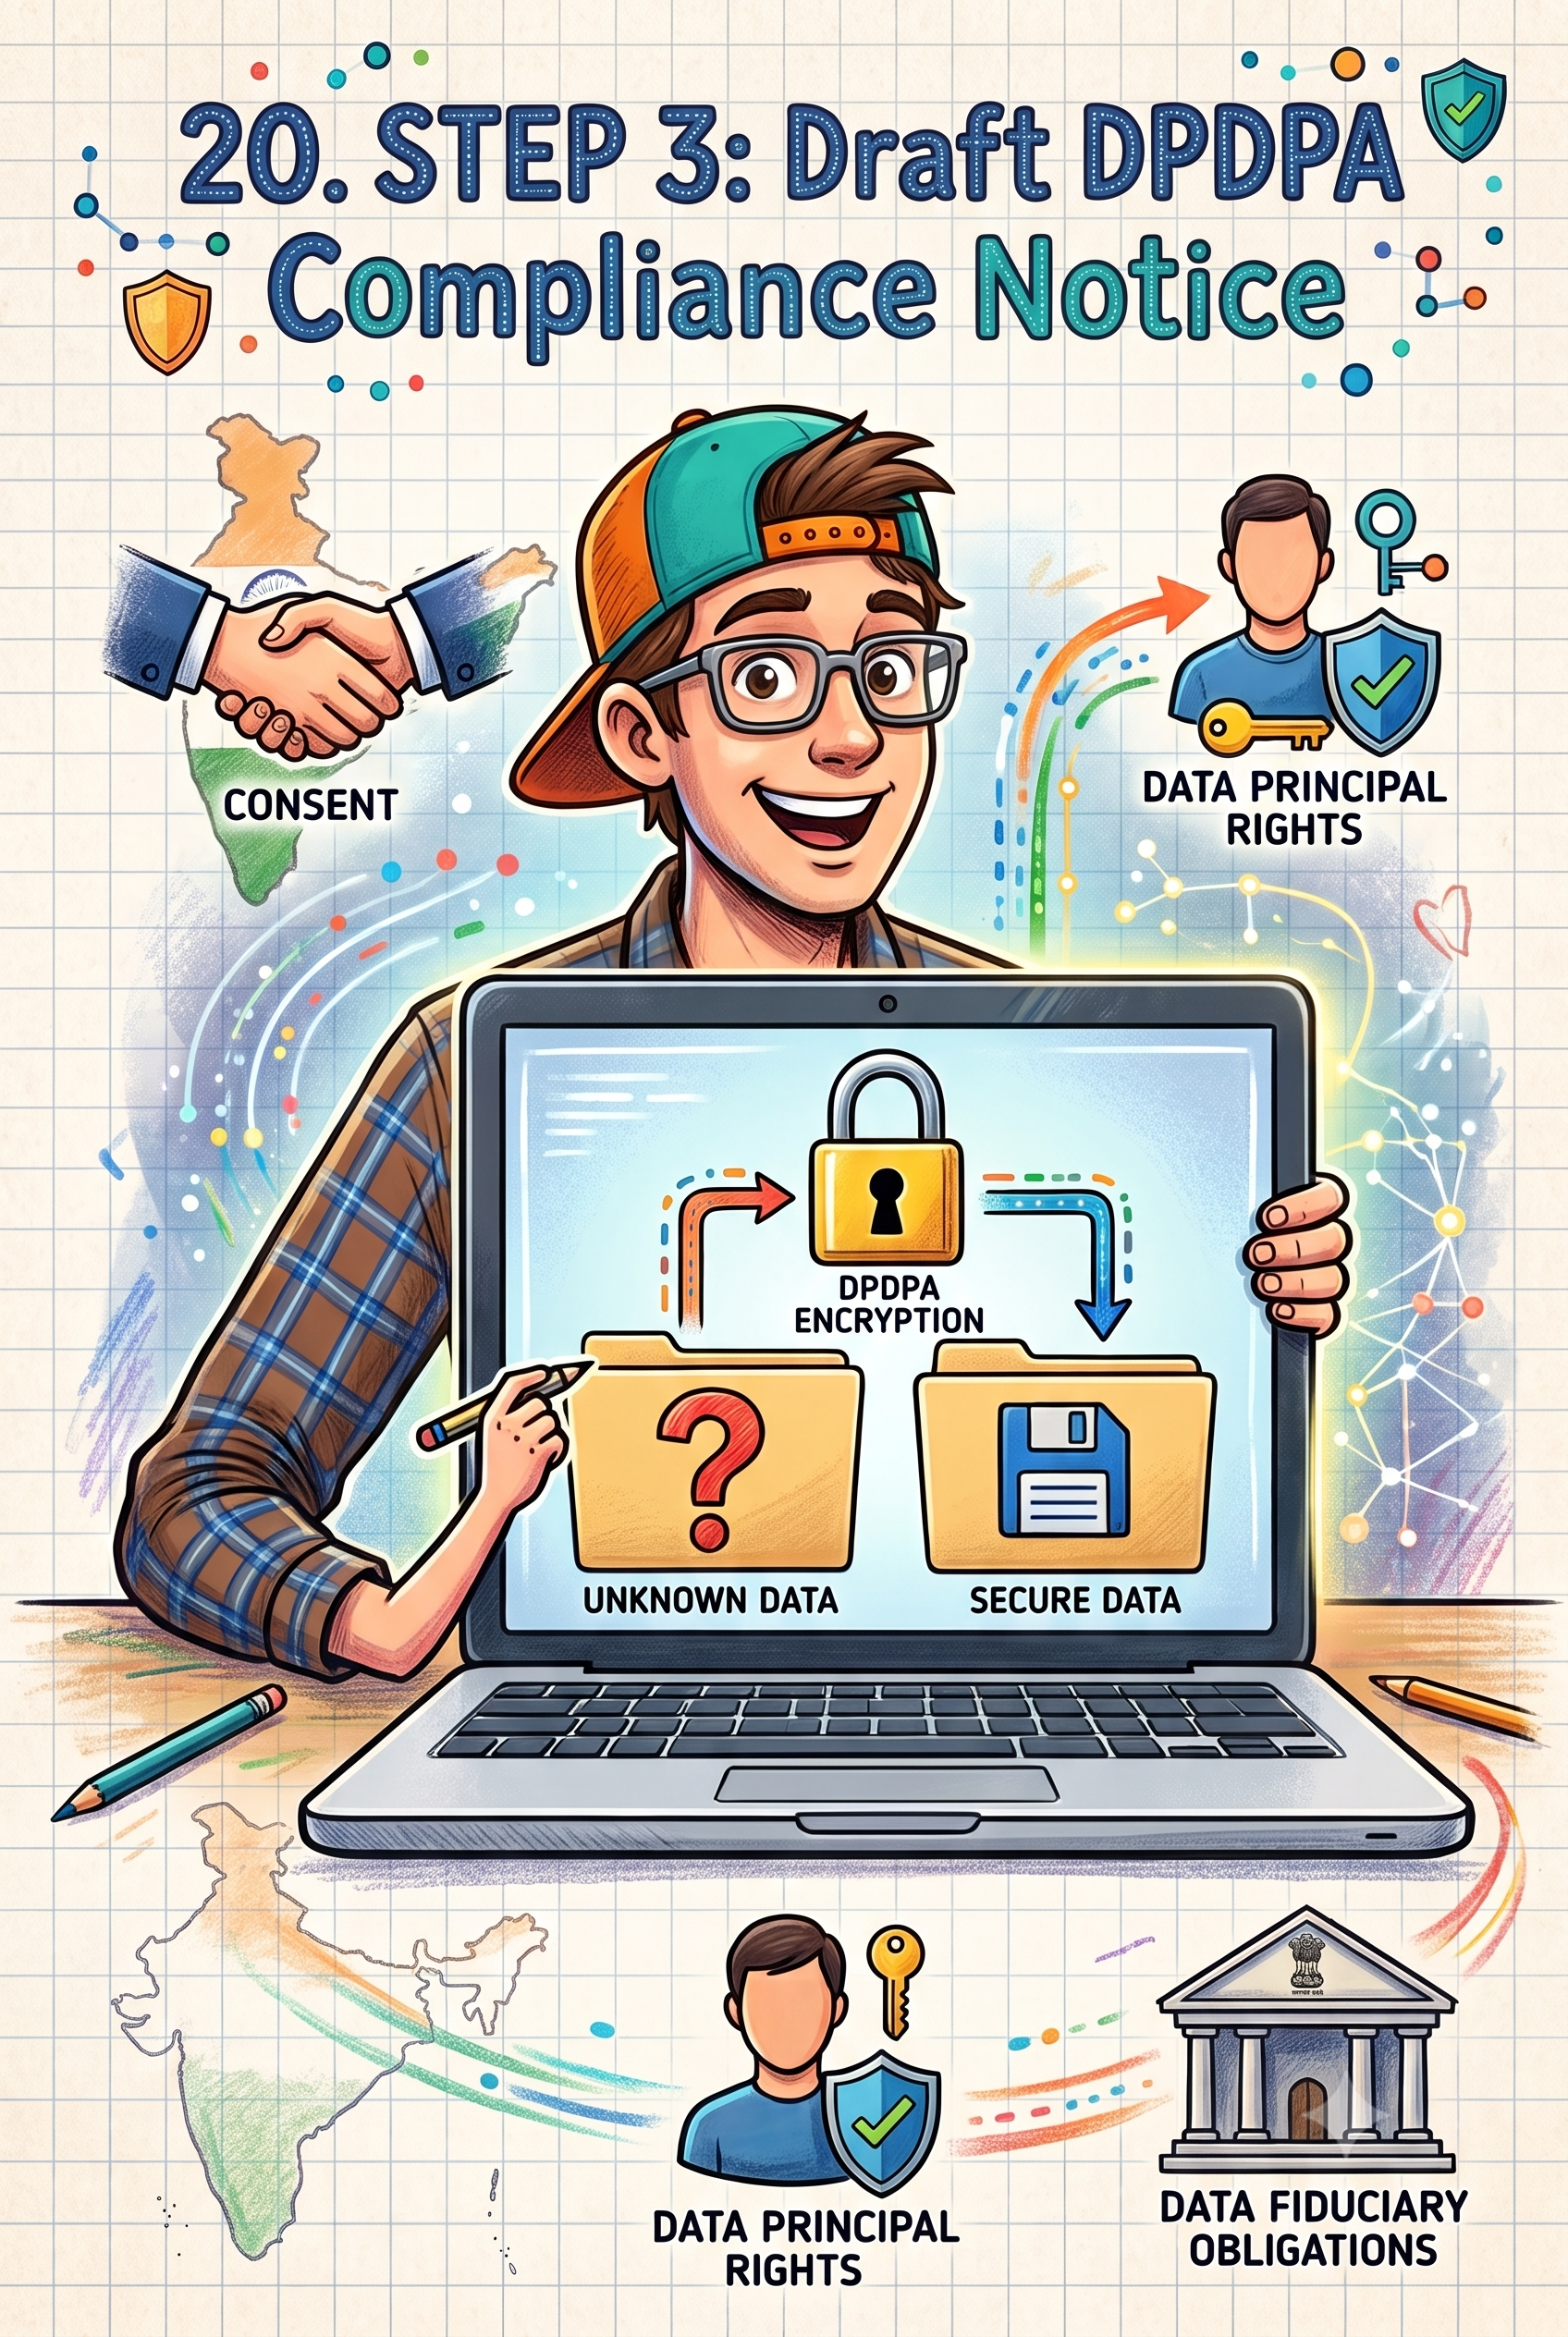
Step 3 of DPDPA compliance is drafting your privacy notice—a publicly available document that clearly explains why you collect data, how you store it, and who processes it, as mandated by Rule 3.
Your privacy notice must be easily accessible on your website, free from confusion, and include a dedicated grievance communication link (like privacy@yourcompany.com) for users to report data misuse.
The notice should cover the purpose of collection, storage locations, third-party processors, and links to your public privacy policy—ensuring transparency for every Data Principal.
For Ankur Technology, this meant publishing a clear notice with a direct contact point, turning legal requirements into customer-facing trust.