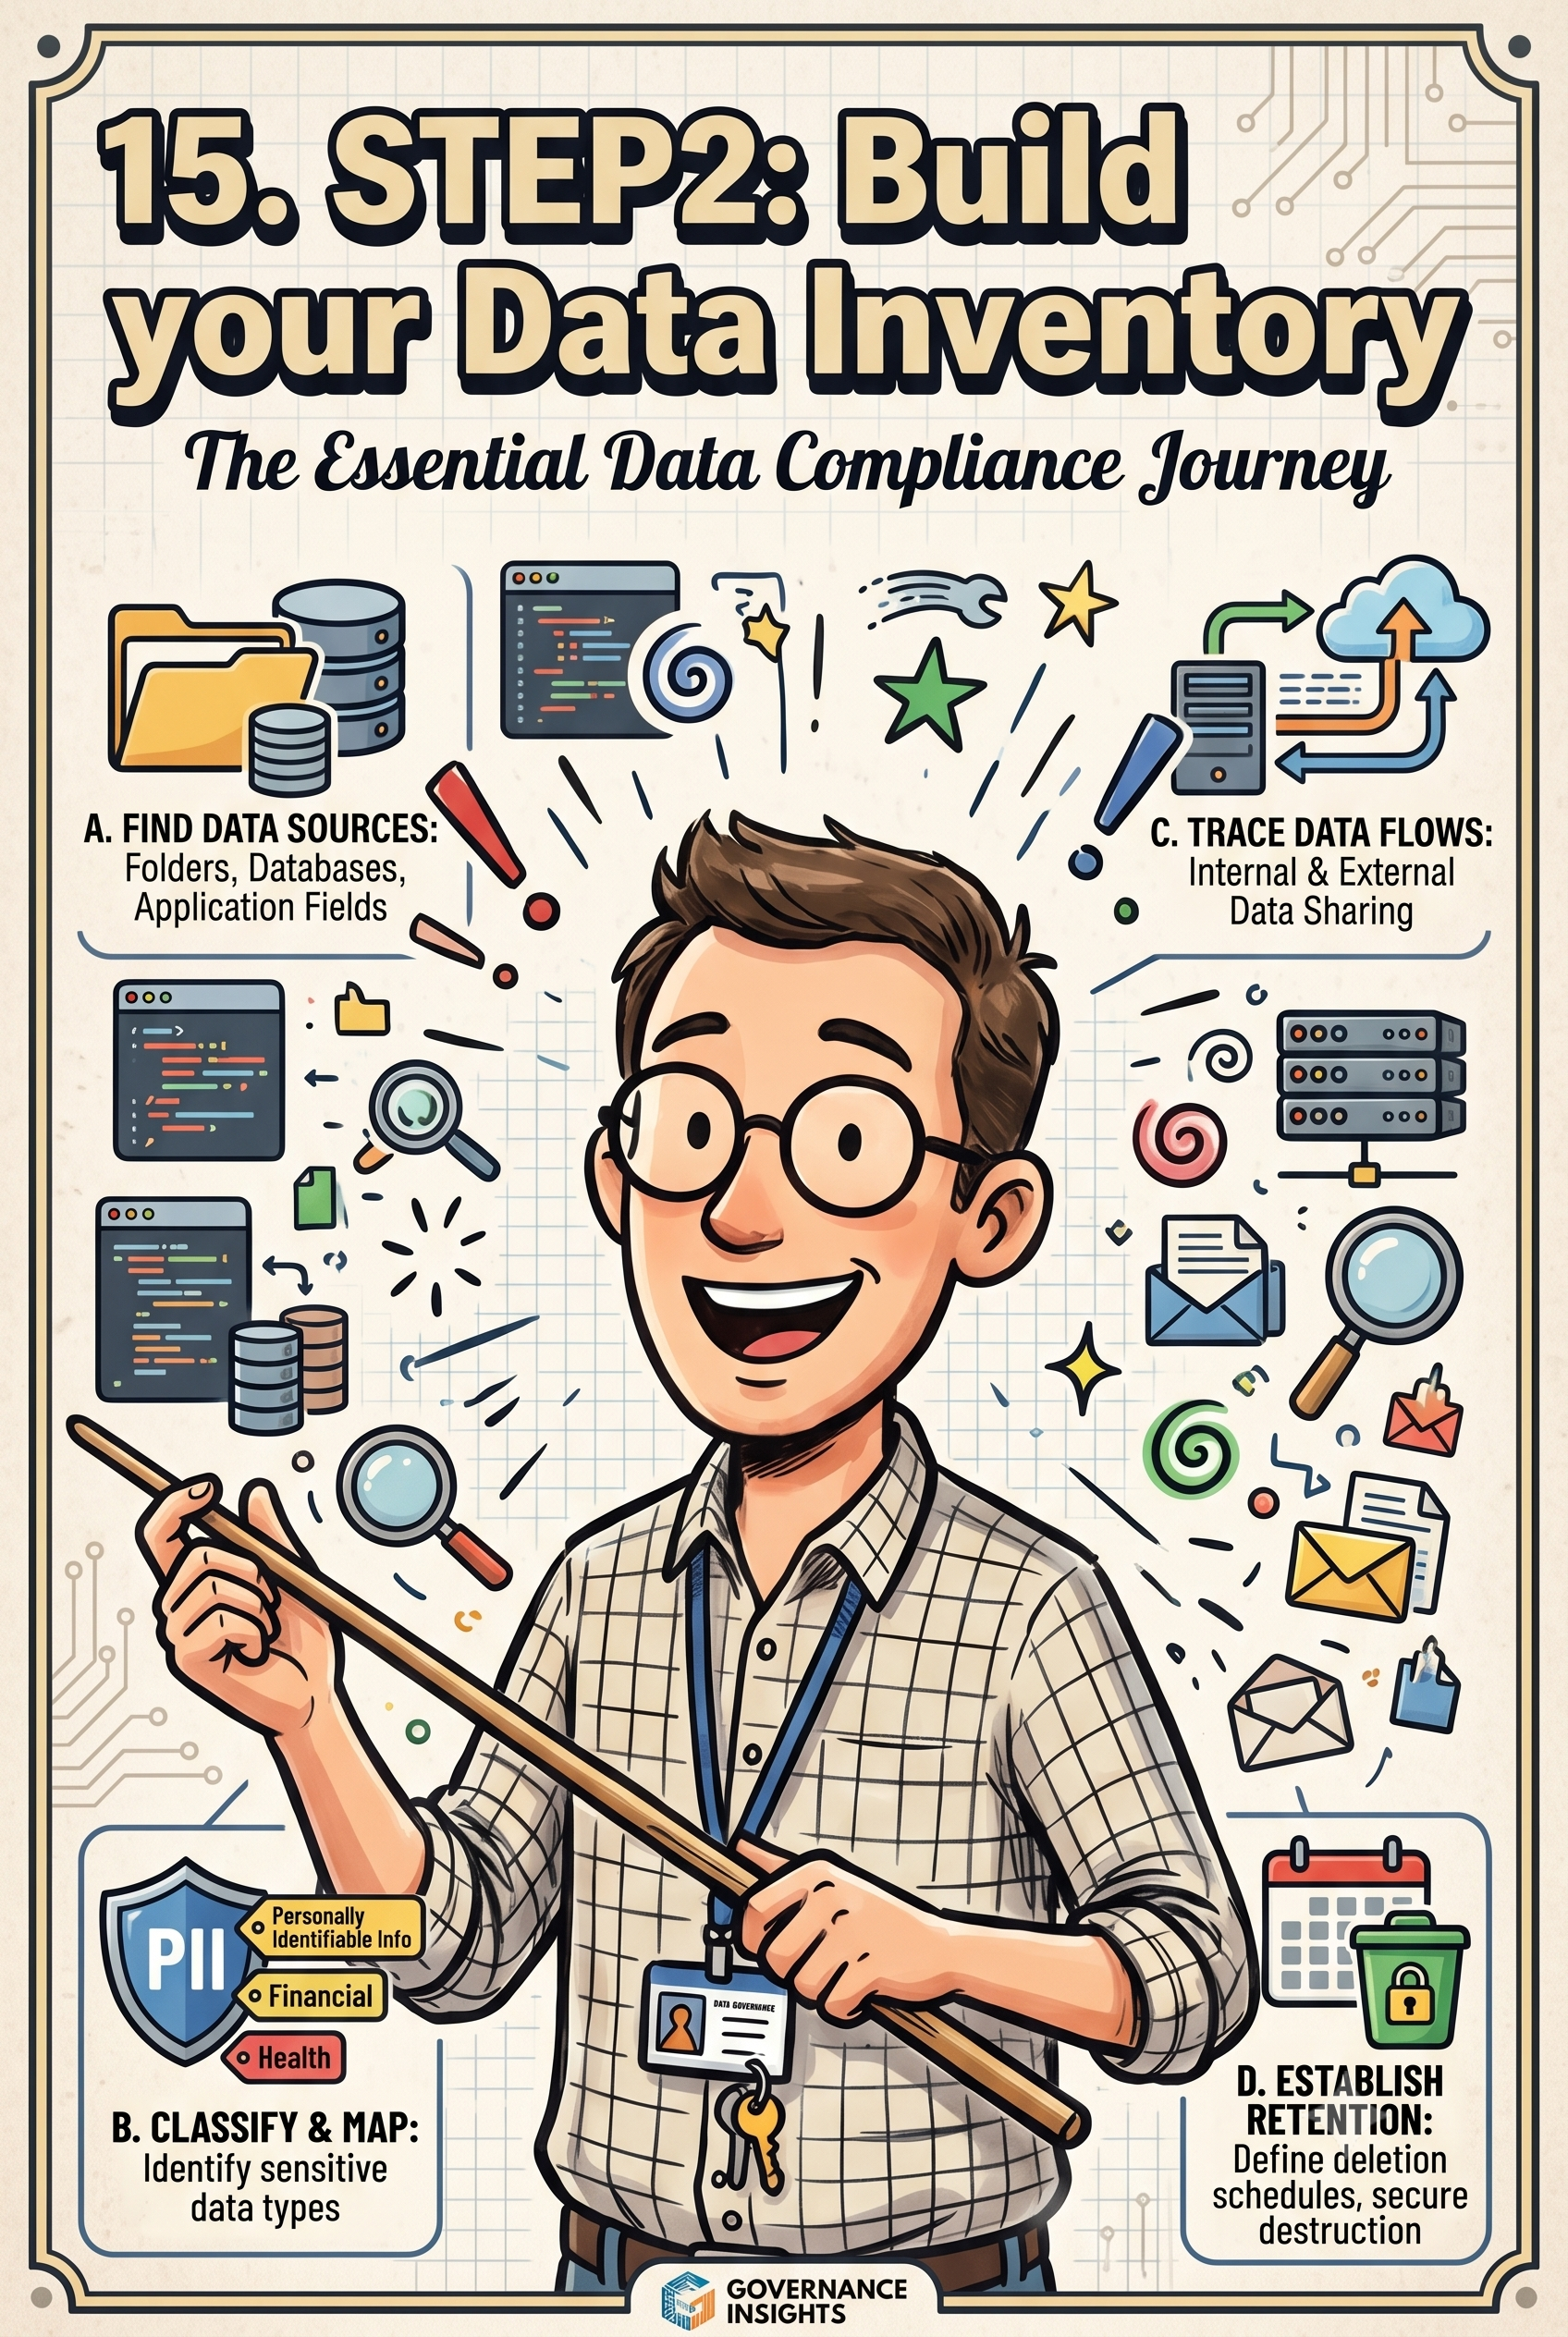
Step 2 of DPDPA compliance is building your data inventory—because without visibility into what data you collect, from whom, where it goes, and why, everything else is just guesswork.
Every organization has three data types: Regulated Data (like DPDPA), Business Data (trade secrets), and Operational Data (SIEM logs)—DPDPA focuses on regulated personal data.
Document critical inventory elements: what data you collect (name, contact, ID, payment, IP logs), whose data (employees, learners, B2B clients), purpose (training, marketing, HR), consent status, storage locations (CRM, LMS, WhatsApp), third-party processors (Mailchimp, Zoho, Razorpay, Zoom), and retention periods.
Inventory is the backbone of compliance—without it, you cannot secure, retain, or delete data effectively.